unSafe.sh - 不安全
我的收藏
今日热榜
公众号文章
导航
Github CVE
Github Tools
编码/解码
文件传输
Twitter Bot
Telegram Bot
Search
Rss
黑夜模式
Security Monitoring of AI Agents in Microsoft Defender XDR
With AI agents now running in many Microsoft 365 tenants, monitoring their activity has bec...
2026-11-3 08:31:53 | 阅读: 22 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
agents
microsoft
defender
copilot
security
Pwn2Own Ireland 2025 – Home Assistant
IntroductionPwn2Own is a renowned hacking competition organized by the Zero Day Initiat...
2026-10-2 10:3:46 | 阅读: 36 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
csnc
compass
python
56246
supervisor
CRA Reporting – What you need to know
While the full implementation of the Cyber Resilience Act (CRA) won’t take effect until Dec...
2026-9-3 08:35:39 | 阅读: 34 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
security
exploited
cra
malicious
A Note on Pentesting Passkeys
Some months ago, I performed a web application penetration test on an application that use...
2026-8-28 21:24:17 | 阅读: 18 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
webauthn
passkey
Pipeleek v1 Release
IntroIn 2024 I released the initial version of Pipeleek. At the time the tool was a...
2026-8-4 08:40:47 | 阅读: 39 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
gitlab
pipeleek
renovate
runner
github
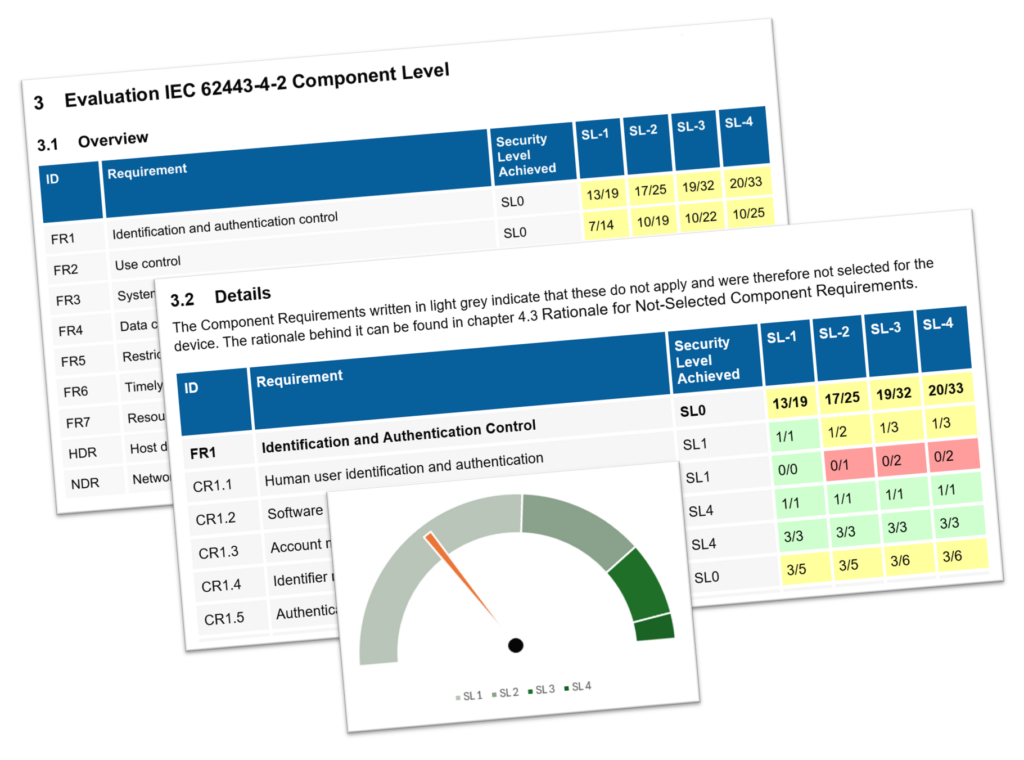
Cyber Resilience Act – Part I
The Cyber Resilience Act (CRA) is a regulation introduced by the European Union to strength...
2026-6-26 07:10:6 | 阅读: 73 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
security
cra
62443
iec
Entra Agent ID from a Security Perspective
Microsoft Entra Agent ID introduces dedicated identity concepts for AI agents in Entra ID....
2026-6-9 07:40:40 | 阅读: 43 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
blueprint
microsoft
identities
entra
client
SSH Labs
TL;DR: Visit https://sshlabs.compass-security.training to learn more about SSH security....
2026-5-27 07:41:48 | 阅读: 37 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
ssh
security
theory
reviews
secured
Common Entra ID Security Assessment Findings – Part 4: Weak Conditional Access Policies
好的,我现在需要帮用户总结一篇文章的内容,控制在100个字以内。首先,我得仔细阅读用户提供的文章内容,了解其主要讨论的主题和重点。 这篇文章主要讨论了微软Entra ID中的条件访问策略(Conditional Access Policies)的常见安全问题。作者通过几个部分详细分析了这些问题,包括身份定位、资源覆盖、过多的条件设置、内置绕过机制以及缺失的策略等。文章还举例说明了攻击者如何利用这些漏洞进行攻击,并推荐了使用EntraFalcon工具来检测这些问题。 接下来,我需要将这些内容浓缩到100字以内。首先,确定文章的核心主题:Entra ID中的条件访问策略问题。然后,列出主要问题:身份定位不当、资源覆盖不足、过多条件导致保护缺口、内置绕过机制以及缺失关键策略。最后,提到检测工具和配置建议。 现在,把这些点连贯地组织成一句话或两句话,确保不超过字数限制,并且准确传达文章的主要内容。 </think> 文章探讨了微软Entra ID中的条件访问策略(Conditional Access Policies)常见安全问题,包括身份定位不当、资源覆盖不足、过多条件导致保护缺口、内置绕过机制以及缺失关键策略等问题,并举例说明攻击者如何利用这些漏洞进行攻击。...
2026-4-14 07:56:16 | 阅读: 39 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
microsoft
security
client
entra
privileged
Common Entra ID Security Assessment Findings – Part 3: Weak Privileged Identity Management Configuration
好的,我现在需要帮用户总结一篇文章的内容,控制在100个字以内。用户的要求很明确,不需要特定的开头,直接写文章描述即可。 首先,我通读了整篇文章。文章主要讨论了微软Entra ID中的特权身份管理(PIM)及其常见配置弱点。PIM用于管理、控制和监控特权访问,提供及时访问、限时权限、审批或多重身份验证等特性。 接下来,文章列出了常见的配置问题,比如PIM未被使用、高权限角色未受保护、仅依赖内置MFA、允许永久激活等。这些配置问题可能导致安全风险,如攻击者绕过保护机制。 然后,文章通过两个攻击示例展示了这些弱点如何被利用。例如,攻击者可能通过获取令牌或利用刷新令牌来激活特权角色。这说明PIM的保护机制如果配置不当,可能效果有限。 最后,文章推荐了EntraFalcon工具来检测弱配置,并给出了针对不同层级角色的配置建议,强调结合其他安全措施的重要性。 总结时,我需要涵盖PIM的作用、常见弱点、攻击示例以及解决方案建议。同时要控制在100字以内,确保信息简洁明了。 </think> 文章讨论了微软Entra ID中的特权身份管理(PIM)及其常见配置弱点。PIM用于管理特权访问权限,但若配置不当(如依赖内置MFA、允许永久激活等),可能导致安全风险。文章通过攻击示例展示了这些弱点的潜在影响,并推荐使用EntraFalcon工具检测弱配置,并提出加强PIM设置的建议。...
2026-4-7 07:48:50 | 阅读: 51 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
pim
privileged
activation
microsoft
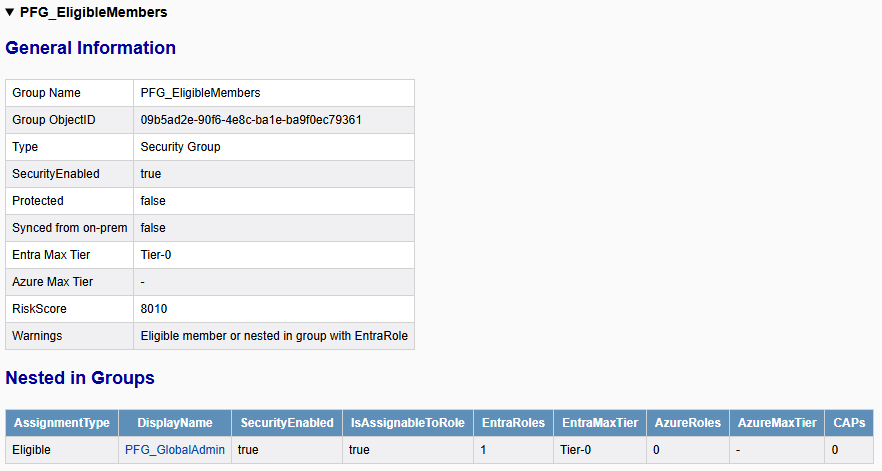
Common Entra ID Security Assessment Findings – Part 2: Privileged Unprotected Groups
嗯,用户让我帮忙总结一篇文章的内容,控制在一百个字以内,而且不需要特定的开头。首先,我需要理解文章的主要内容。文章讨论的是Entra ID中的安全问题,特别是未受保护的组带来的风险。 文章提到这些组可能被低权限的管理员或外部应用滥用,导致敏感权限被篡改。比如,条件访问策略、特权身份管理和Azure角色分配都可能受到影响。最后,文章推荐使用受限管理行政单元来保护这些组。 接下来,我需要将这些要点浓缩成一句话,确保不超过一百个字。要突出未受保护的组的风险、潜在影响以及推荐的解决方案。 可能的表达是:“文章探讨了Entra ID中未受保护组的安全风险,包括被低权限管理员或外部应用滥用的可能性,并可能导致敏感权限被篡改。建议使用受限管理行政单元来保护这些组。” 这样既涵盖了主要问题和影响,也提出了解决方案。 </think> 文章探讨了Entra ID中未受保护组的安全风险,包括被低权限管理员或外部应用滥用的可能性,并可能导致敏感权限被篡改。建议使用受限管理行政单元来保护这些组。...
2026-3-31 09:48:34 | 阅读: 56 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
assignable
security
microsoft
unprotected
privileged
Common Entra ID Security Assessment Findings – Part 1: Foreign Enterprise Applications With Privileged API Permissions
嗯,用户让我帮忙总结一下这篇文章的内容,控制在一百个字以内,而且不需要用“文章内容总结”或者“这篇文章”这样的开头。直接写描述即可。 首先,我需要通读整篇文章,抓住主要点。文章主要讨论了Entra ID中的企业应用程序安全问题,特别是来自其他租户的“外部企业应用”。这些应用通常拥有广泛的API权限,虽然没有特权角色,但可能存在风险。 接下来,文章解释了企业应用是什么,以及它们如何在多租户环境中工作。重点在于这些外部应用的API权限可能被滥用,比如访问 SharePoint 或其他敏感数据。此外,文章还提到了检测工具EntraFalcon和缓解措施。 我需要将这些要点浓缩到100字以内。关键点包括:外部企业应用、API权限风险、潜在滥用案例、检测工具和缓解建议。 最后,确保语言简洁明了,直接描述内容,不使用任何开头语。 </think> 文章探讨了Entra ID中外部企业应用程序的安全风险,特别是其API权限可能导致的数据泄露或系统滥用。通过示例展示了攻击者如何利用这些权限访问敏感资源或提升权限,并介绍了检测工具EntraFalcon和缓解建议。...
2026-3-24 09:33:28 | 阅读: 34 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
microsoft
entra
20260226
compass
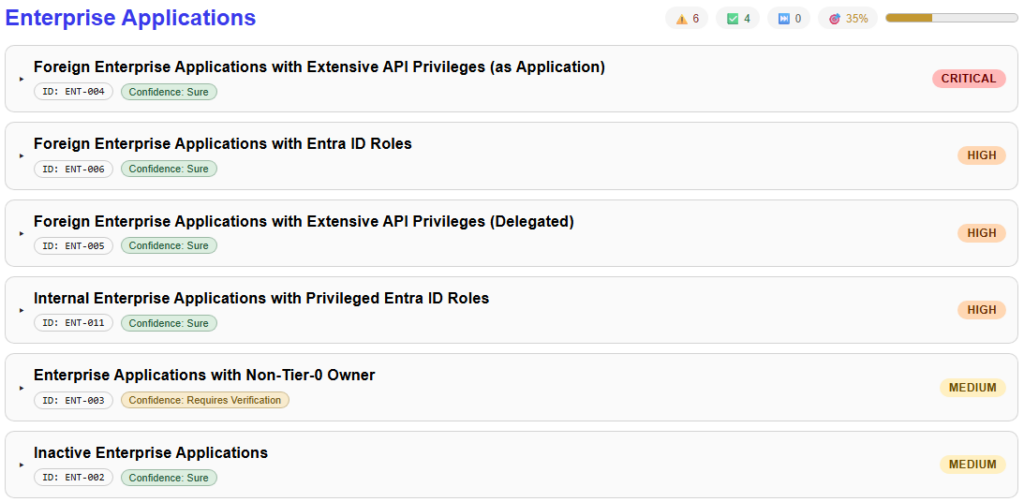
From Enumeration to Findings: The Security Findings Report in EntraFalcon
嗯,用户让我帮忙总结一下这篇文章的内容,控制在100个字以内,而且不需要用“文章内容总结”之类的开头。首先,我需要仔细阅读这篇文章,抓住主要信息。 文章主要讲的是EntraFalcon工具的更新,特别是新增的安全发现报告功能。这个报告整合了租户设置和基于对象的检查,生成结构化的安全发现,并且有60多个检查项、图表、过滤和导出功能。 接下来,我需要提取关键点:工具名称、更新内容、新增功能、检查数量、图表和交互性。然后把这些信息浓缩到100字以内,确保语言简洁明了。 可能会遇到的问题是如何在有限的字数内涵盖所有重要信息,比如工具的用途、新增功能的作用以及可用性。可能需要舍弃一些细节,比如具体的检查项或技术细节,以确保整体描述清晰。 最后,检查一下是否符合用户的要求:中文总结、100字以内、直接描述内容。确保没有使用禁止的开头语,并且信息准确无误。 </think> EntraFalcon工具新增安全发现报告功能,整合租户设置和对象检查,生成结构化安全发现并提供63项检查、图表和交互式过滤功能。...
2026-3-17 09:34:23 | 阅读: 47 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
security
entrafalcon
github
entra
tier
WinGet Desired State: Initial Access Established
嗯,用户让我帮忙总结一篇文章,控制在一百个字以内,而且不需要特定的开头。首先,我需要仔细阅读这篇文章,理解它的主要内容。 文章主要讲的是利用winget配置指令和自引用LNK文件作为初始访问载荷。看起来这是一个安全相关的技术,可能用于红队项目。作者提到winget虽然不是新的,但防御社区似乎忽视了它的滥用潜力。 接下来,文章详细介绍了winget的配置功能,如何通过DSC执行系统配置,甚至可以下载和运行恶意软件。然后讨论了如何减少用户交互,比如使用LNK快捷方式来触发winget命令,并隐藏执行过程。 最后,文章还提到了检测和缓解措施,建议禁用Microsoft Store或winget功能,或者移除.winget文件关联。 总结一下,文章的核心是展示如何利用winget和LNK文件进行初始访问攻击,并提供了一些防御建议。所以,在总结的时候需要涵盖这些要点:技术手段、攻击方法、防御措施。 控制在100字以内的话,我需要简洁明了地表达这些内容。确保涵盖winget、LNK文件、初始访问载荷、防御建议等关键词。 </think> 文章介绍了一种利用winget配置指令和自引用LNK文件作为初始访问载荷的技术。通过结合合法的系统功能和自引用快捷方式,攻击者可以在目标环境中执行恶意操作。该方法利用了winget的配置功能和PowerShell脚本执行能力,并通过减少用户交互和隐藏执行过程来规避检测。防御方可以通过禁用Microsoft Store或winget功能来降低风险。...
2026-3-3 09:33:33 | 阅读: 49 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
winget
windows
powershell
microsoft
Continuous Learning – Inside our Internal Security Training
文章描述了公司在2025年为客户提供数百次安全评估,并通过参加外部会议、课程及内部培训保持团队技能更新。重点包括Kubernetes安全培训、专家指导及实践演练,同时开展其他技术专题培训,并举办年度训练营培养新人。...
2026-1-20 09:17:16 | 阅读: 17 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
security
kubernetes
2026
camp
trainings
NTLM Relaying to HTTPS
NTLM is the legacy authentication protocol in Windows environment. In the past few years, I...
2025-11-26 10:17:2 | 阅读: 38 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
relaying
certipy
esc8
windows
bRPC-Web: A Burp Suite Extension for gRPC-Web
文章介绍了gRPC及其变体gRPC-Web的技术细节、应用场景及挑战,并展示了如何通过Burp Suite扩展bRCP-Web来解决渗透测试中的数据解码难题。该工具支持对二进制或Base64编码的Protobuf消息进行解析、编辑及流式通信处理。...
2025-10-21 07:9:39 | 阅读: 51 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
grpc
echorequest
protobuf
submessage1
submessage2
LockBit Breach: Insights From a Ransomware Group’s Internal Data
LockBit勒索软件团伙遭对手入侵致数据泄露,涉及35名 affiliates 和208次谈判记录。仅8%的谈判成功支付赎金,赎金从2千到2百万美元不等,部分有折扣。比特币为主要支付方式。平均解密时间为4天左右。文章建议企业加强预防措施以减少风险。...
2025-10-7 09:31:46 | 阅读: 41 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
lockbit
affiliates
victim
ransomware
decryptor
Ensuring NIS2 Compliance: The Importance of Penetration Testing
欧盟发布《网络与信息安全指令2》(NIS2),旨在加强关键行业网络安全韧性。该指令扩大适用范围至"重要实体"和"基础实体",涵盖能源、交通、金融、医疗等领域,并要求实施强化安全措施和事件报告机制。合规需通过风险管理和渗透测试等手段提升安全性。违规者将面临高额罚款。...
2025-9-23 09:17:0 | 阅读: 39 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
security
nis2
regulatory
ensuring
penalties
Collaborator Everywhere v2
Collaborator Everywhere for Burp Suite Professional has been upgraded with features like editable payloads, a dedicated interaction tab, and persistent storage. These improvements enhance detection and analysis of out-of-band communication, such as SSRF or Host header vulnerabilities. The extension is available in the BApp Store or on GitHub....
2025-9-9 09:31:30 | 阅读: 58 |
收藏
|
Over Security - Cybersecurity news aggregator - blog.compass-security.com
oastify
payload
spoofed
burp
Previous
1
2
3
4
5
6
7
8
Next