Microsoft’s November Patch Tuesday fixes more than 1,000 Microsoft vulnerabilities, including an Outlook flaw that attackers are already exploiting to steal authentication information.
The release also fixes 48 critical remote code execution (RCE) vulnerabilities that could allow attackers to run code on affected machines, in some cases without user interaction.
While Windows updates address many of this month’s vulnerabilities, readers should check for Office updates as well: the exploited Outlook flaw is patched through the affected Office products.
To do this, follow these instructions:
- Open an Office application, such as Word.
- Go to File > Account. In Outlook, this may appear as Office Account.
- Under Product Information, select Update Options > Update Now.
- If necessary, select Enable Updates first. If the update controls are missing on a work device, contact your organization’s IT team; updates may be centrally managed.
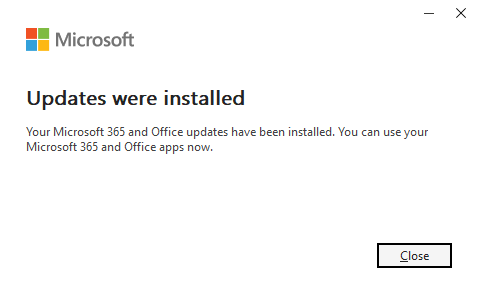
During the update, you may be prompted to save your work (check your open documents). Afterward, you should see something similar to this:
How to apply Windows patches and check if you’re protected
These updates fix security problems and help keep your Windows PC protected. Here’s how to make sure you’re up to date:
- Click the Start button, then open Settings.
- Select Windows Update (usually at the bottom of the menu on the left).
- Click Check for updates. Windows will search for the latest security updates. If you’ve enabled Get the latest updates as soon as they’re available under More options, you may be prompted to restart immediately to complete the update.
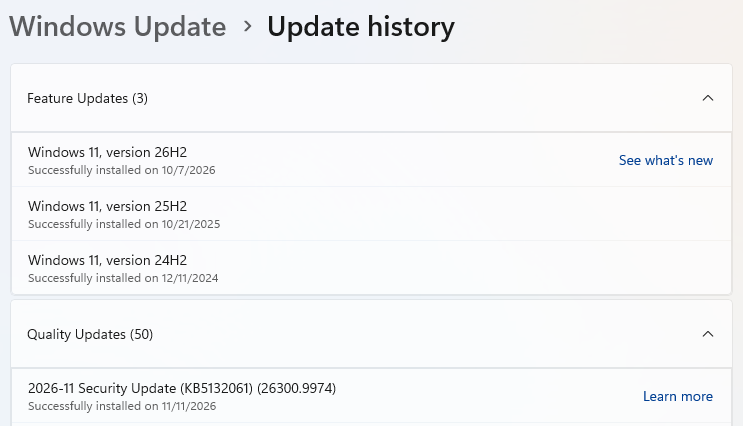
- You may find the update (Security Update KB5132061) already installed.
- If updates are available, they’ll start downloading automatically. When they’re ready, click Install or Restart now if prompted. Your computer may need a restart to finish the update.
- After restarting, go back to Windows Update and check again. If it says You’re up to date, you’re all set.
Technical details
As usual, we’ve selected a few vulnerabilities to highlight for readers interested in the technical details.
We’ll start with CVE-2026-124194, an Outlook vulnerability that attackers are already exploiting. It has a CVSS score of 6.5 out of 10 and could expose authentication information that attackers could use to impersonate the user. From Microsoft’s description:
“Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to perform spoofing over a network.”
To exploit this vulnerability, an attacker must convince someone to open a specially crafted message file in an affected version of Outlook. This can cause Outlook to connect to an attacker-controlled network location without its usual external-content warning, potentially exposing authentication information (the user’s NTLMv2 hash) that could be used to impersonate them.
As this vulnerability is being exploited in the wild, updating Office as described earlier is a priority.
One other vulnerability I want to highlight is CVE-2026-116928 (CVSS score 9.8 out of 10):
“Out-of-bounds write in Microsoft Windows Search Component allows an unauthorized attacker to execute code over a network.”
An out-of-bounds write vulnerability allows a program to write outside the memory boundaries it is supposed to use, which can lead to memory corruption or place malicious code in memory and trick the system into running it.
Microsoft describes an attack in which a malicious email attachment is processed automatically for indexing by Exchange Server. In that scenario, the recipient does not need to open the email or attachment. Processing it could be enough to let the attacker run code with the permissions of the affected service. Microsoft has not reported exploitation of this vulnerability.
From reporting threats to removing them.
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.