
Atlassian Data Center Products Unauthenticated Arbitrary File Read VulnerabilityCVE-2026-21 2026-10-6 23:15:0 Author: horizon3.ai(查看原文) 阅读量:32 收藏
Atlassian Data Center Products Unauthenticated Arbitrary File Read Vulnerability
CVE-2026-21589 allows unauthenticated remote attackers to read specific files within the web application root directory of affected Atlassian products. Attackers must know the exact filename and path, and cannot list directory contents. Sensitive information may be exposed depending on the files present. Atlassian classifies the vulnerability as critical.
Atlassian states that affected Cloud products have been patched and that its investigation found no evidence of exploitation. No Cloud customer action is required.
Technical Details
The vulnerability permits file access over the network without authentication. Atlassian confirms these requirements and limitations:
- Authentication: No credentials are required.
- Target knowledge: Exploitation requires the target file’s exact name and path.
- File-access scope: The disclosed vulnerability provides access to specific files within the web application root directory.
- Directory enumeration: Attackers cannot use this vulnerability to enumerate or list directory contents.
- Impact: Sensitive files within the accessible directory may be disclosed, depending on the installation’s configuration.
NodeZero® Proactive Security Platform Rapid Response
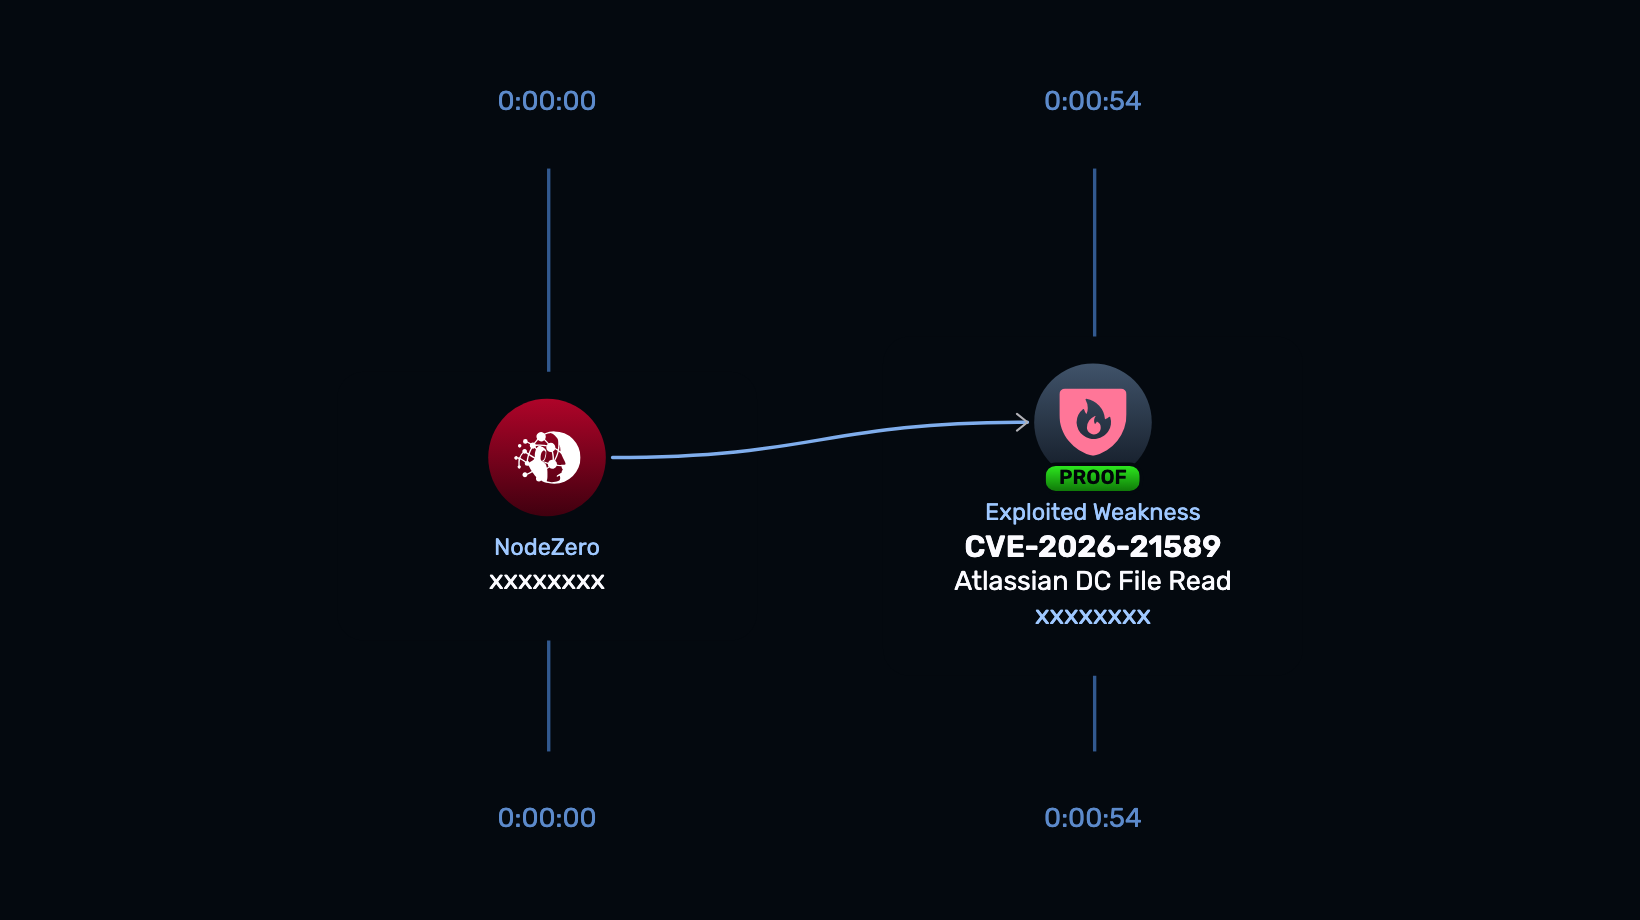
A NodeZero Rapid Response test has been developed to safely validate whether this vulnerability can be exploited in your environment. The test executes real attack techniques without causing damage, giving teams immediate clarity on exposure.
- Run the Rapid Response test: Launch from the NodeZero platform to determine whether exploitation is possible.
- Patch immediately: Upgrade to a fixed version or apply vendor-recommended mitigations.
- Re-run the test: Confirm the vulnerability is no longer exploitable after remediation.
Stop Guessing, Start Proving
Affected versions & patch
Affected
Atlassian identifies versions preceding the applicable fixed releases as affected. Installations outside the support window may also be affected and should be upgraded to a supported fixed release.
Fixed
| Product | Fixed versions |
| Bitbucket Data Center | 9.4.26, 10.2.8, 10.5.1 |
| Confluence Data Center | 9.2.26, 10.2.19 |
| Jira Service Management Data Center | 5.12.40, 10.3.26, 11.3.12 |
| Jira Software Data Center | 9.12.40, 10.3.26, 11.3.12 |
| Bamboo Data Center | 10.2.24, 12.1.12 |
| Crowd Data Center | 6.3.7, 7.0.3, 7.1.7, 7.2.4 |
| Crucible | 4.9.15 |
| Fisheye | 4.9.15 |
Upgrade to an applicable fixed release listed above or a later supported release containing the fix.
Mitigations
If immediate patching is not possible, restrict public internet access until patching or temporary mitigation is complete. Authentication alone does not protect an exposed instance.
Atlassian provides these temporary mitigation options:
- All affected products: Apply the vendor’s WAF or reverse-proxy filtering rule.
- Confluence, Jira Service Management, Jira Software, Bamboo, and Crowd: Configure Tomcat’s RewriteValve with the vendor-provided rules.
- Bitbucket: Apply the vendor’s
urlrewrite.xmlrule to all applicable cluster nodes, mirrors, and mirror farm nodes.
Follow the advisory’s complete configuration, testing, and restart instructions.
Timeline
- October 5, 2026: Atlassian published its security advisory, identifying affected products, fixed versions, and temporary mitigations.
- October 6, 2026: Horizon3 released the NodeZero Rapid Response test for CVE-2026-21589.
References
Read about other CVEs
NodeZero® Platform
Implement a continuous find, fix, and verify loop with NodeZero
The NodeZero® platform empowers your organization to reduce your security risks by autonomously finding exploitable weaknesses in your network, giving you detailed guidance around how to priortize and fix them, and having you immediately verify that your fixes are effective.
Recognized By
如有侵权请联系:admin#unsafe.sh