2026-10-01: Traffic analysis exercise - Natureforce
2026-10-01 - TRAFFIC ANALYSIS EXERCISE: NATUREFORCENOTE:Zip files are password-protected. Of 2026-10-5 02:54:0 Author: www.malware-traffic-analysis.net(查看原文) 阅读量:6 收藏
2026-10-01 - TRAFFIC ANALYSIS EXERCISE: NATUREFORCENOTE:Zip files are password-protected. Of 2026-10-5 02:54:0 Author: www.malware-traffic-analysis.net(查看原文) 阅读量:6 收藏
2026-10-01 - TRAFFIC ANALYSIS EXERCISE: NATUREFORCE
NOTE:
- Zip files are password-protected. Of note, this site has a new password scheme. For the password, see the "about" page of this website.
ASSOCIATED FILE:
- Zip archive of the pcap: 2026-10-01-traffic-analysis-exercise.pcap.zip 33.1 MB (33,137,313 bytes)
BACKGROUND
Working as an analyst at a security operations center (SOC), you see the following alerts:
- 107.175.82[.]242:9000 - Windows executable (EXE) file sent from IP address over unusual TCP port
- 195.64.128[.]106:443 - CNCmachineRMS RAT C2 traffic
You retrieve a packet capture (pcap) of traffic from the associated Windows host to review the activity and verify the alerts.
The characteristics of this environment are:
- LAN segment range: 10.10.1[.]0/24 (10.10.1[.]0 through 10.10.1[.]255)
- Domain: natureforce[.]com
- AD environment name: NATUREFORCE
- Active Directory (AD) domain controller: 10.10.1[.]10 - WIN-LEKBU2OY51N
- LAN segment gateway: 10.10.1[.]1
- LAN segment broadcast address: 10.10.1[.]255
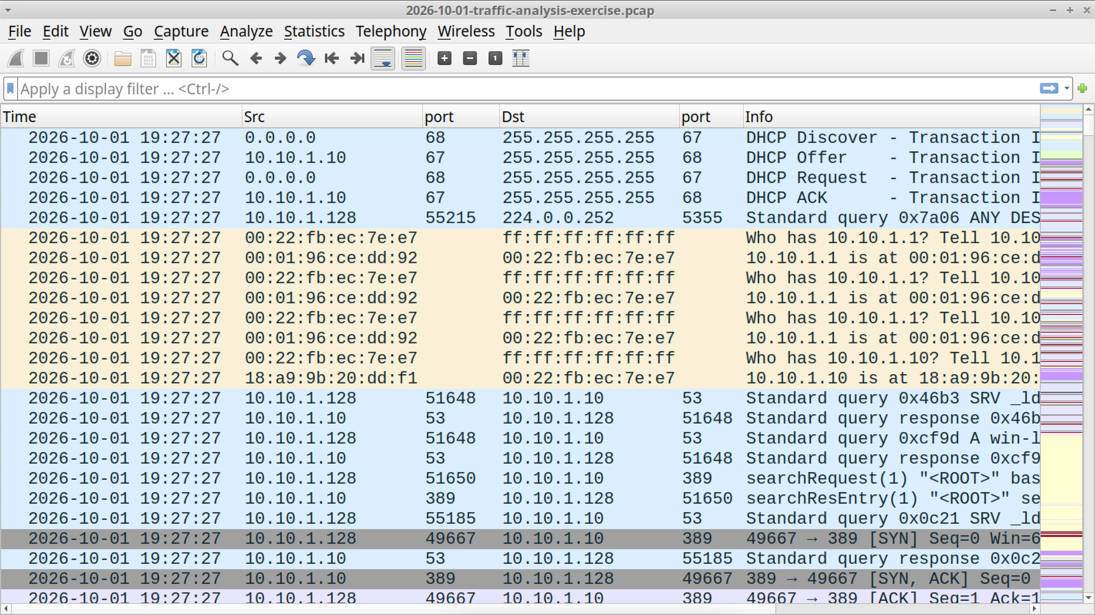
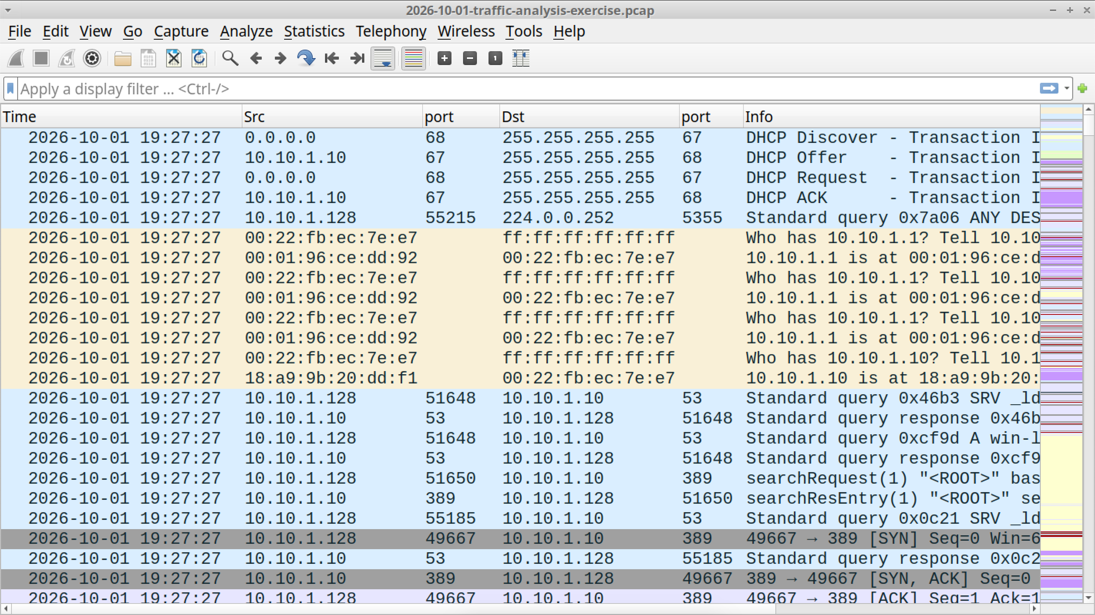
Shown above: Pcap for this exercise opened in Wireshark.
YOUR TASK
For this exercise, answer the following questions for your incident report:
- What is the IP address of the infected Windows client?
- What is the MAC address of the infected Windows client?
- What is the host name of the infected Windows client?
- What is the user account name from the infected Windows client?
- What is the SHA-256 hash of the Windows EXE file sent from 107.175.82[.]242:9000 to the Windows client
ANSWERS
- Click here for the answers.
Click here to return to the main page.
文章来源: https://www.malware-traffic-analysis.net/2026/10/01/index.html
如有侵权请联系:admin#unsafe.sh
如有侵权请联系:admin#unsafe.sh