The Federal Bureau of Investigation is investigating a breach of its job applications platform afte 2026-9-23 14:31:7 Author: therecord.media(查看原文) 阅读量:4 收藏
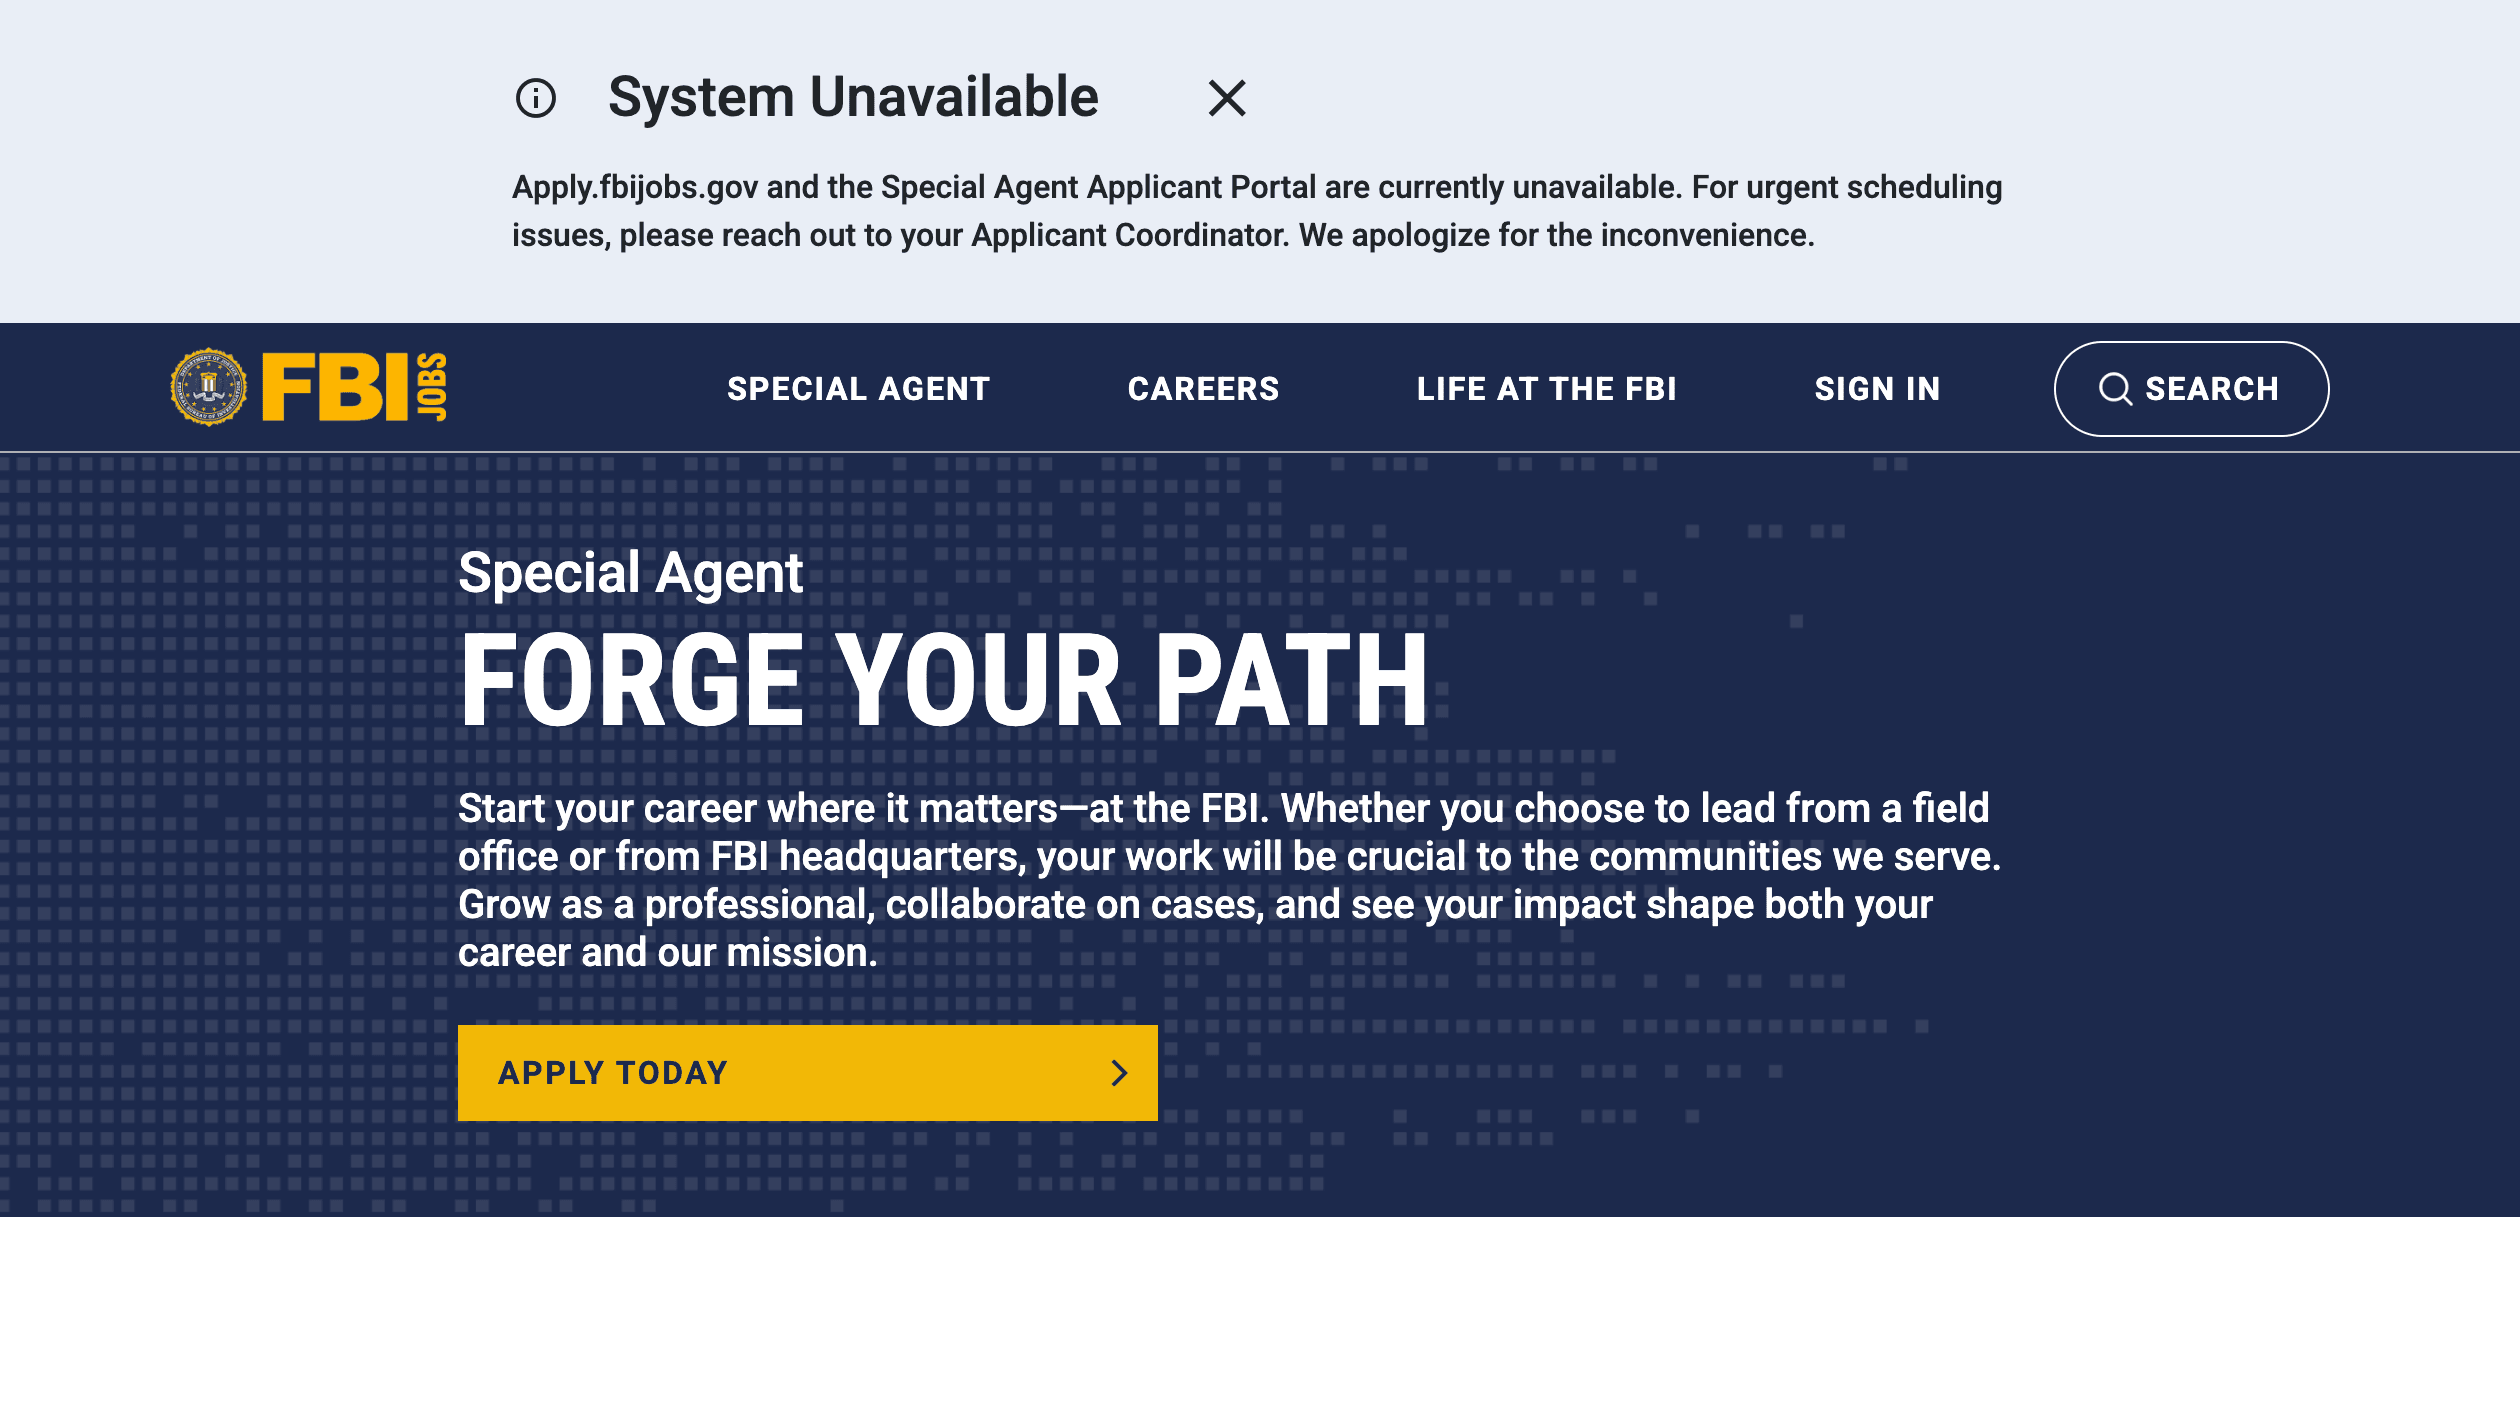
The Federal Bureau of Investigation is investigating a breach of its job applications platform after a cybercriminal group defaced the website and claimed to have stolen information on current and former employees and applicants. The ShinyHunters cybercriminal organization on Tuesday replaced agency images on the FBIjobs.gov site with a photo of a Pokemon that has become the group’s defacto mascot. The group then took to its leak site to post a lengthy statement criticizing the FBI for a public service announcement released earlier this year that made several assertions ShinyHunters’ claims are false. The group threatened to leak information on every FBI agent and anyone who has applied for a job at the FBI if the white notice was not taken down. “The FBI is aware of claims regarding unauthorized activity affecting FBIjobs.gov and is currently investigating,” an FBI spokesperson told Recorded Future News on Tuesday evening. The agency did not respond to several other questions about the claims made by ShinyHunters. As of Wednesday morning, the FBI jobs site still has a banner saying the special agent application portal is currently unavailable. ShinyHunters provided samples of 5,000 stolen FBI agent records to 404media and several other news outlets, which confirmed their legitimacy. In its message yesterday, ShinyHunters took issue with FBI claims that it exaggerated the data it stole and that it extorted the employees of the companies they hacked into. "We wish to state unequivocally we have never conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats,” the group claimed. “We wish to state unequivocally we have never claimed to have sensitive information, including embarrassing photographs and videos of victims. We are not sextortionists.” The group also denied being part of The Com — a larger group of young English-speaking hackers accused of various crimes targeting children online. The notice was issued by the FBI in May following ShinyHunters attack on educational software giant Instructure. The attack disrupted operations at thousands of universities and K-12 schools across the U.S., forcing the company to eventually pay the ransom to restore its services. The group has been in the crosshairs of the FBI for nearly one year after dozens of high-profile attacks on large companies like Ticketmaster and AT&T as well as educational publisher McGraw Hill, Carnival Cruise Line, 7-Eleven and other companies. Brett Leatherman, assistant director of the FBI’s Cyber Division, spoke at length about the group during a roundtable two weeks ago, telling reporters that after successfully securing the arrest of members of a related cybercriminal group, the FBI is now “focused” on ShinyHunters “because right now it's a big problem when it comes to data exfiltration and extortion attacks.” Several experts said it is likely the group will leak the stolen data because the FBI will not remove the alert. “The bigger worry is ShinyHunters selling the data to other criminal or nation-state groups who could put it to more damaging use, rather than dumping it themselves,” said Andrew Brandt, incident responder at cybersecurity firm Huntress. “These are law enforcement personnel who deal with serious and dangerous criminals, sometimes requiring infiltration into criminal networks. It could be abused in a multitude of ways, from financial fraud to serious threats of harm against staff and their immediate families, to future targeted attacks in cyberspace or the physical world.” Additional reporting by Martin Matishak. 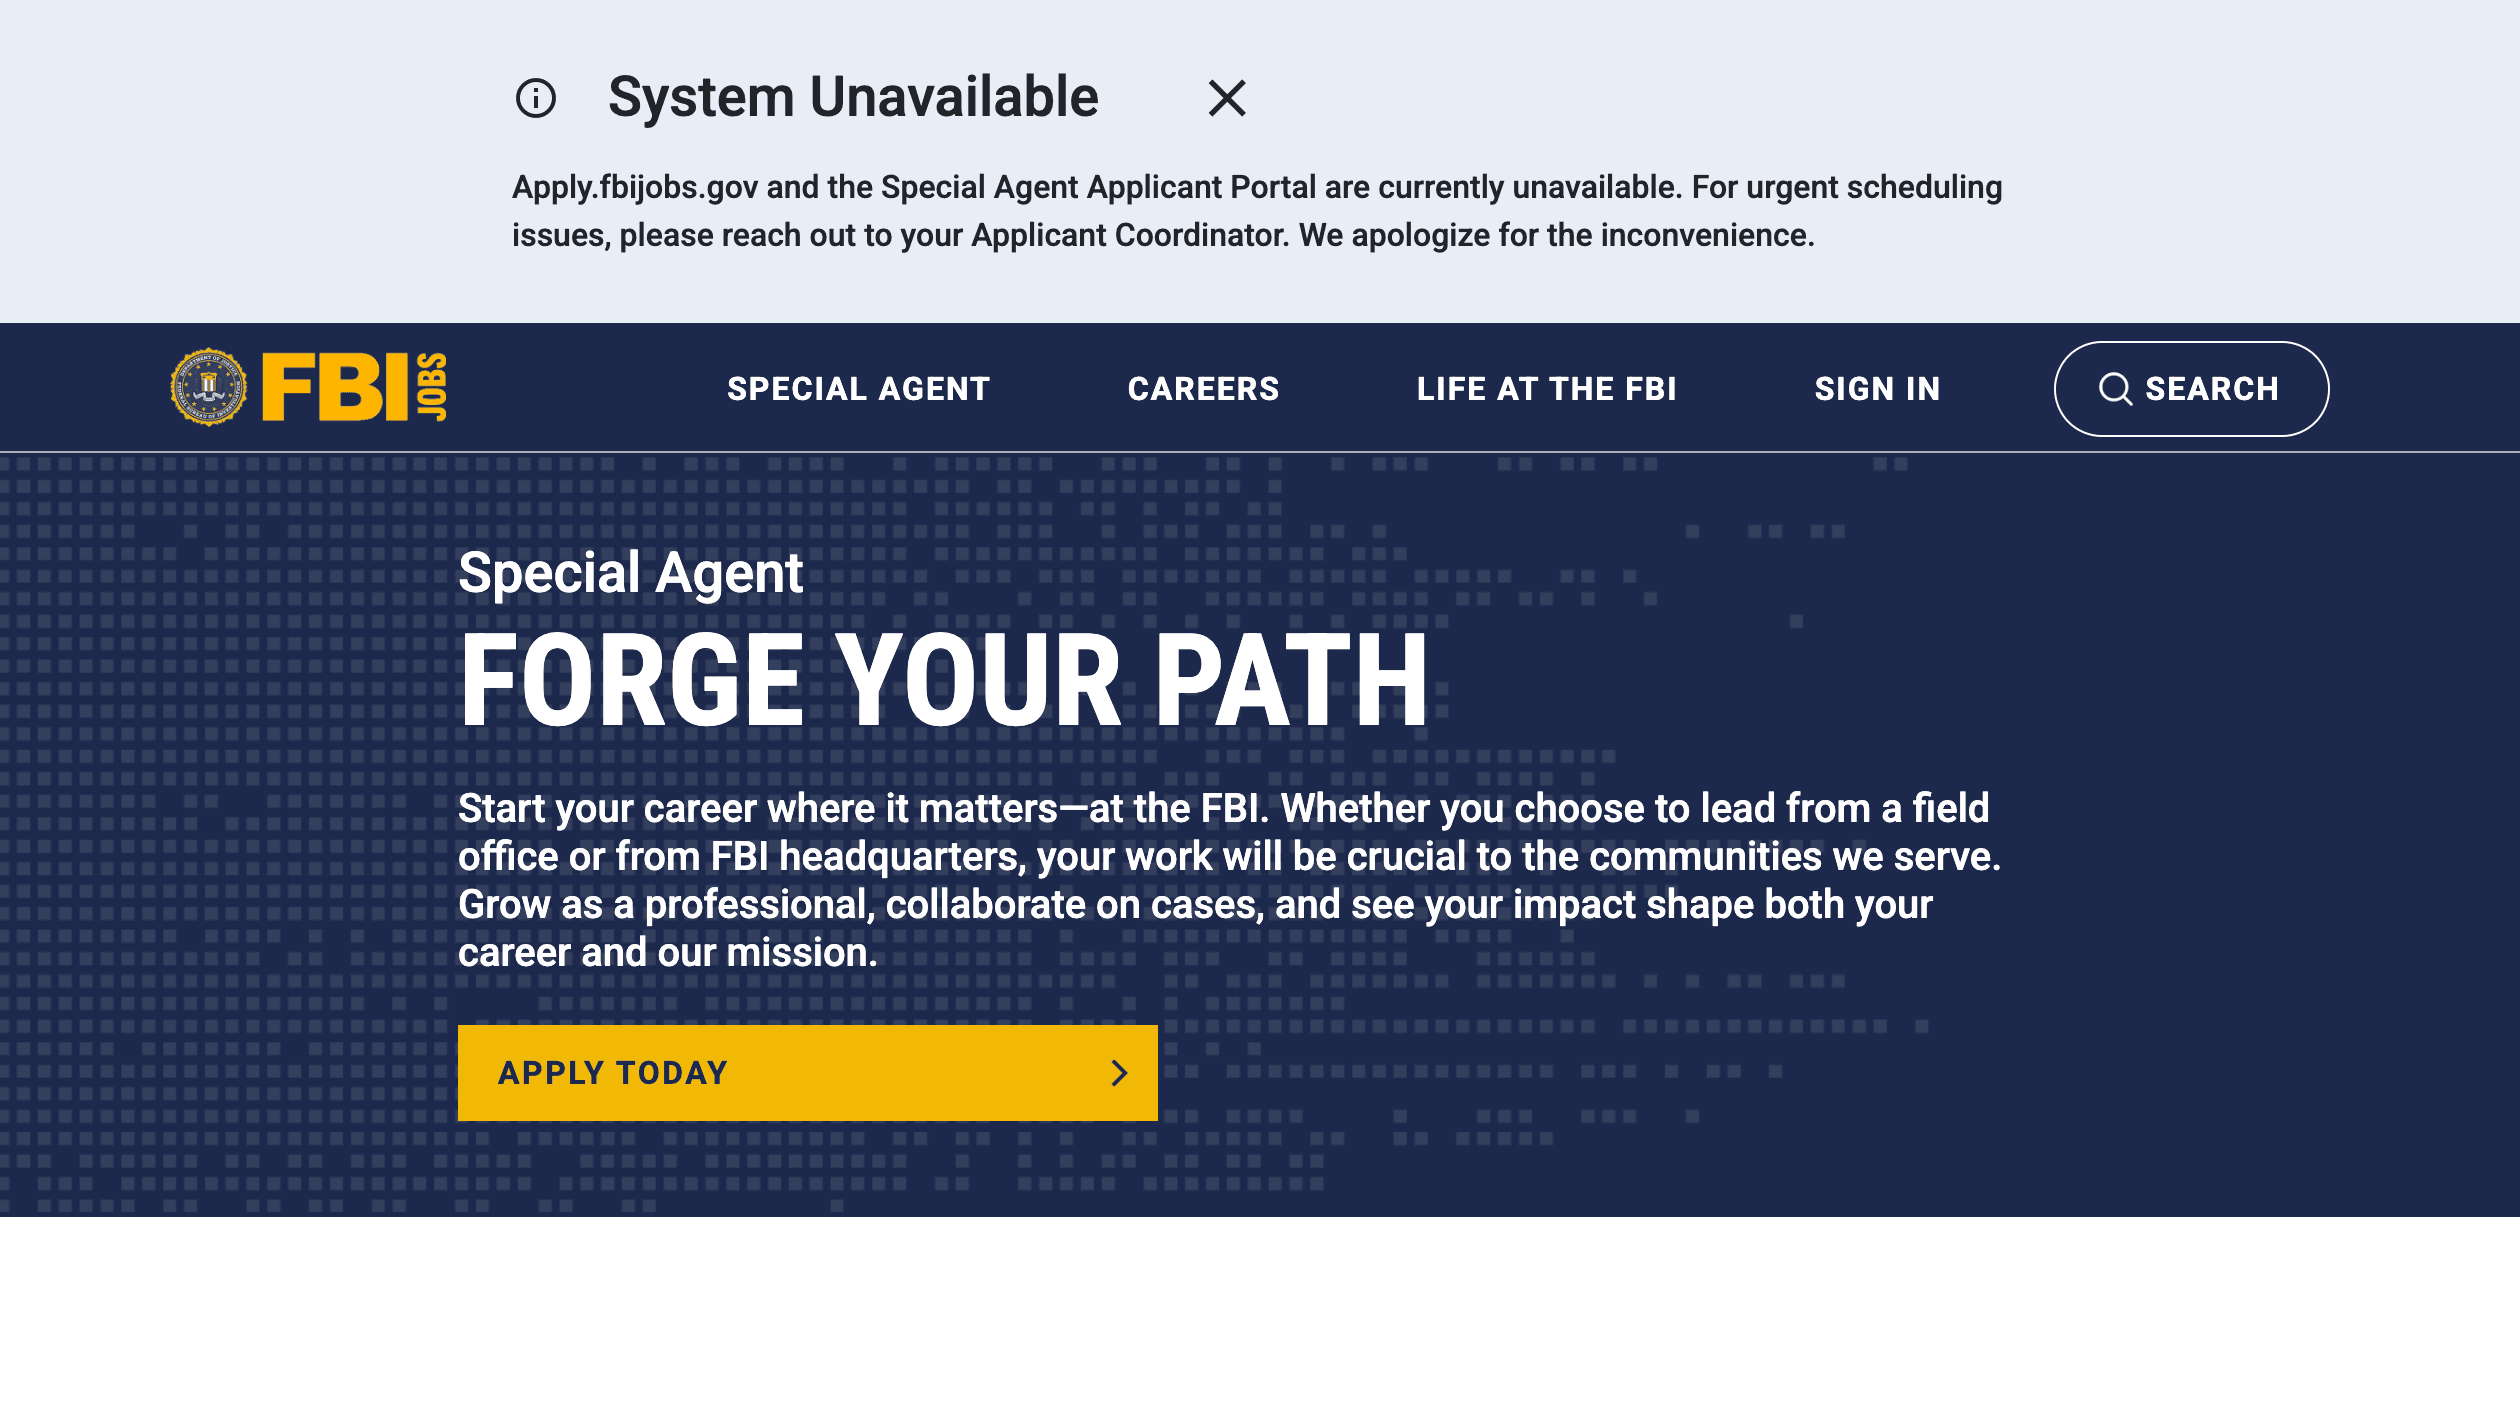
No previous article
No new articles

Jonathan Greig
is a Breaking News Reporter at Recorded Future News. Jonathan has worked across the globe as a journalist since 2014. Before moving back to New York City, he worked for news outlets in South Africa, Jordan and Cambodia. He previously covered cybersecurity at ZDNet and TechRepublic.
如有侵权请联系:admin#unsafe.sh