2026-09-14: Backdoor using ScreenConnect from malicious emailt
2026-09-14 (MONDAY): BACKDOOR USING SCREENCONNECT FROM MALICIOUS EMAILNOTICE:Zip files are pa 2026-9-21 01:4:0 Author: www.malware-traffic-analysis.net(查看原文) 阅读量:16 收藏
2026-09-14 (MONDAY): BACKDOOR USING SCREENCONNECT FROM MALICIOUS EMAILNOTICE:Zip files are pa 2026-9-21 01:4:0 Author: www.malware-traffic-analysis.net(查看原文) 阅读量:16 收藏
2026-09-14 (MONDAY): BACKDOOR USING SCREENCONNECT FROM MALICIOUS EMAIL
NOTICE:
- Zip files are password-protected. Of note, this site has a new password scheme. For the password, see the "about" page of this website.
ASSOCIATED FILES:
- 2026-09-14-IOCs-for-backdoor-suing-screenconnect.txt.zip 1.0 kB (1,013 bytes)
- 2026-09-14-ScreenConnect-from-malicious-email.pcap.zip 13.3 MB (13,257,539 bytes)
- 2026-09-14-email-and-malware-for-backdoor-suing-screenconnect.zip 11.0 MB (10,991,929 bytes)
2026-09-14 (MONDAY): BACKDOOR USING SCREENCONNECT FROM MALICIOUS EMAIL

SOME OF THE EMAIL HEADERS:

- Received: from allsecured[.]net (unknown [23.227.202[.]93])
  by [information removed]; Sun, 13 Sep 2026 14:05:44 +0000 (UTC)
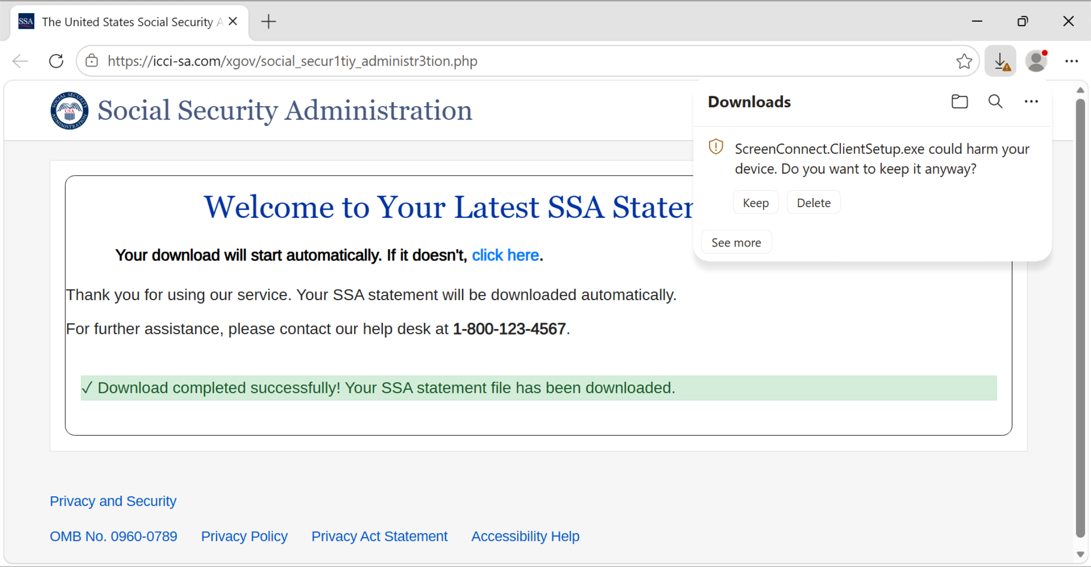
- From: Social Security Administration (Information@allsecured[.]net)
- Subject: Your Monthly SSA Electronic Statement is Available for Download
- Date: 13 Sep 2026 14:05:42 +0000
- Message-ID: 20260913140542.71B0635A54B0E91F@allsecured[.]net

LINK FROM EMAIL:

- hxxps[:]//t[.]co/LPz3zzwREa

FAKE SOCIAL SECURITY ADMINISTRATION PAGE AND FILE DOWNLOAD:

- hxxps[:]//icci-sa[.]com/xgov
- hxxps[:]//icci-sa[.]com/xgov/
- hxxps[:]//icci-sa[.]com/xgov/social_secur1tiy_administr3tion.php
- hxxps[:]//icci-sa[.]com/xgov/social_secur1tiy_administr3tion.php?download=exe

DOWNLOADED CUSTOMIZED SCREENCONNECT CLIENT INSTALLER:

- SHA-256 hash: f1d103dd77d09697fa30fa14c4f39e394b0331a33ffd2ef5df2916dbe79e474b
- File size: 12,828,216 bytes
- File type: PE32 executable (GUI) Intel 80386, for MS Windows
- File name: ScreenConnect.ClientSetup.exe

POST-INFECTION SCREENCONNECT TRAFFIC:

- tcp[:]//15.204.43.235[:]443 - instance-udppxf-relay.screenconnect.com - encoded/encrypted ScreenConnect traffic
IMAGES
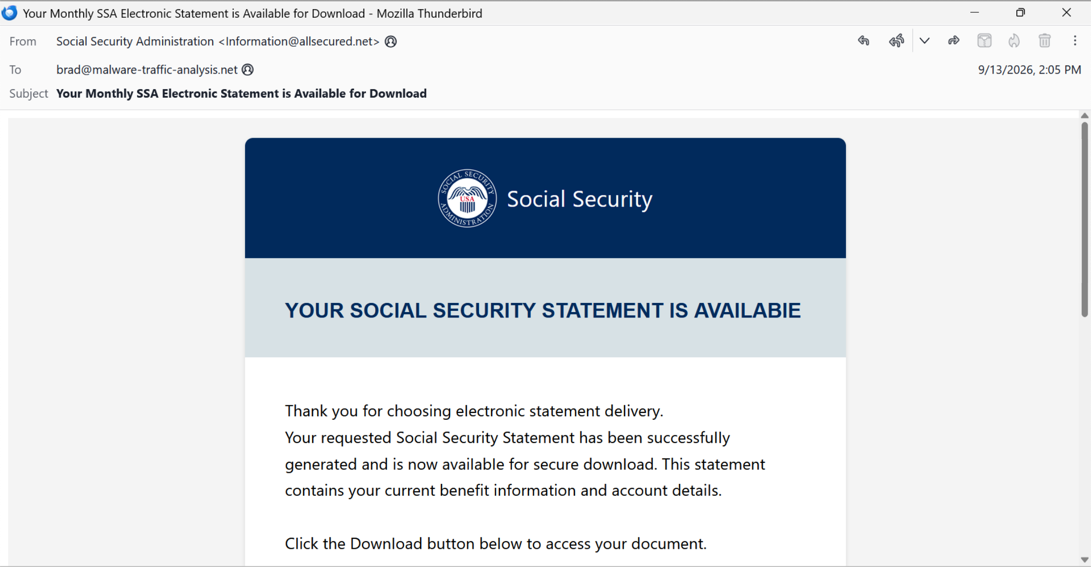
Shown above: Screenshot of the email.
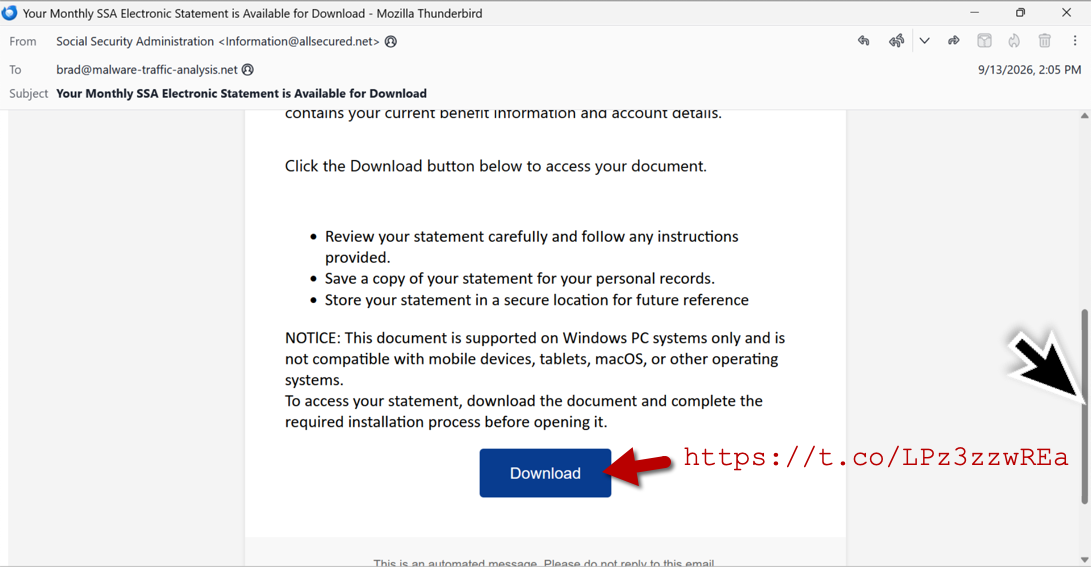
Shown above: Screenshot of the web page impersonating the Social Security Administration.
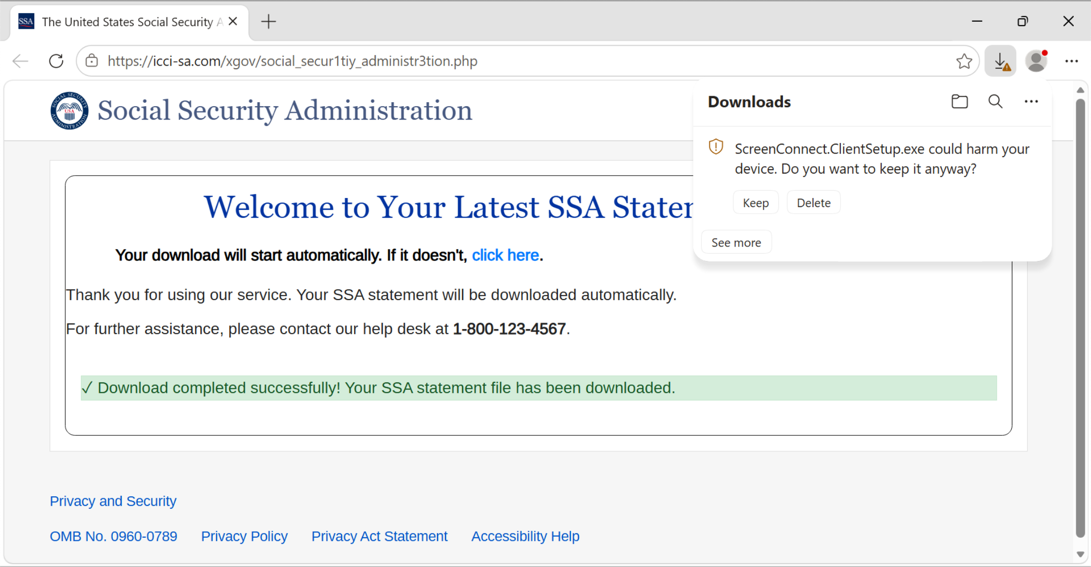
Shown above: Screenshot of the web page impersonating the Social Security Administration with the malicious download noted.
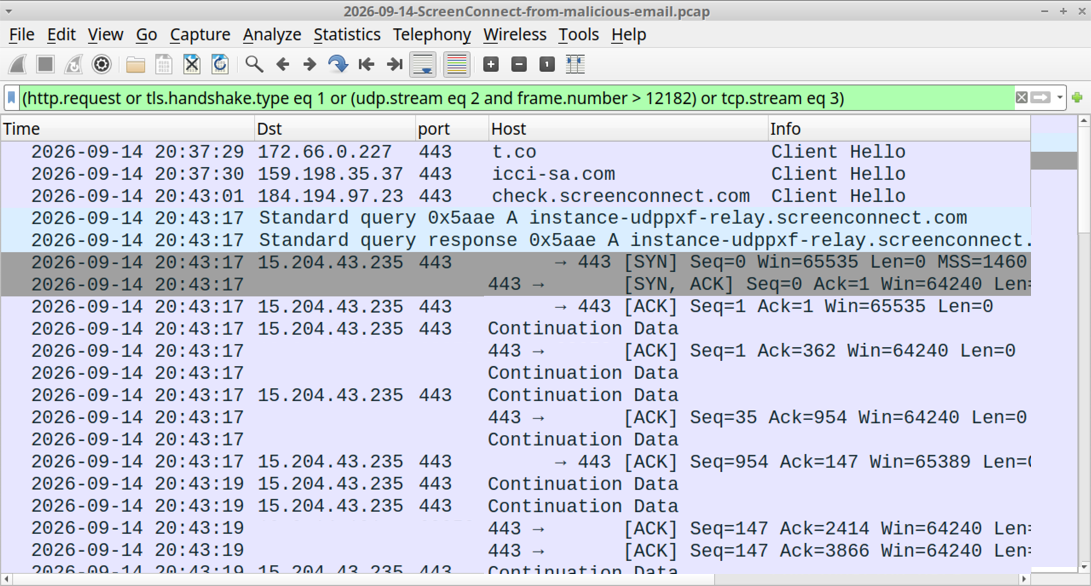
Shown above: Traffic from the infection filtered in Wireshark.
Click here to return to the main page.
文章来源: https://www.malware-traffic-analysis.net/2026/09/14/index.html
如有侵权请联系:admin#unsafe.sh
如有侵权请联系:admin#unsafe.sh