Home > Apple Push Notification Service, macOS, Mobile Device Management, Secure Enclave, Virtu 2026-9-15 19:0:42 Author: derflounder.wordpress.com(查看原文) 阅读量:27 收藏
Home > Apple Push Notification Service, macOS, Mobile Device Management, Secure Enclave, Virtualization > Enrolling macOS Golden Gate 27.0.0 virtual machines with MDM servers does not work correctly
Enrolling macOS Golden Gate 27.0.0 virtual machines with MDM servers does not work correctly
As part of testing macOS Golden Gate, it was discovered by myself and others that MDM enrollment does not appear to completely work. In my testing, here’s what I did:
- Create a macOS VM running macOS 27.0.0
- Enroll it in an MDM (in my case, Jamf Pro) using profile-based device enrollment.
- MDM enrollment profile is successfully installed.
Expected behavior following step #3:
- Additional configuration profiles and Jamf software components are installed on the macOS VM.
Actual behavior following step #3:
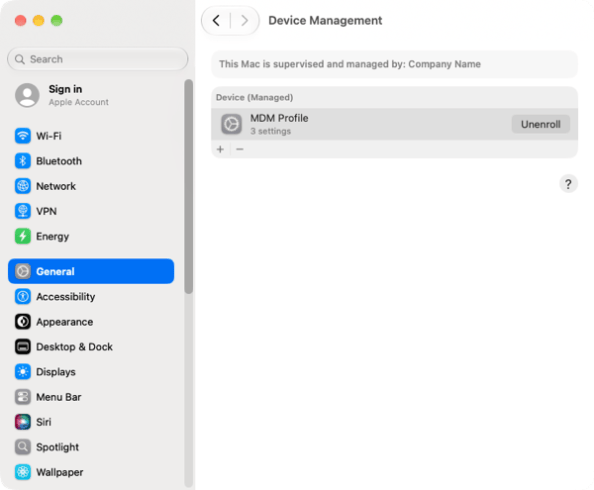
- No additional profiles or Jamf software components are installed. Only the MDM enrollment profile is visible in System Settings, in General: Device Management.

What’s happening after step #3? For more details, please see below the jump.
To check on this issue, I ran the following command using the log command line tool to see what was being logged within the last hour by apsd, the background system process on macOS responsible for maintaining macOS’s persistent connection to Apple’s Push Notification service (APNS):
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
| log show –info –debug –predicate 'process == "apsd" AND (eventMessage CONTAINS[c] "BAA" OR eventMessage CONTAINS[c] "unable to generate key" OR eventMessage CONTAINS[c] "server bag")' –last 1h |
When I checked the logging, I saw the following logging repeatedly appear:
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
| 2026-09-15 08:35:55.176162-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:courier] <private>: Identity provider has processed server bag update, user courier finished processing config | |
| 2026-09-15 08:35:55.176162-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:courier] <private> user courier finished processing server bag (1/2) | |
| 2026-09-15 08:35:55.176163-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:courier] <private>: Identity provider has processed server bag update, user courier finished processing config | |
| 2026-09-15 08:35:55.176164-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:courier] <private> user courier finished processing server bag (2/2) | |
| 2026-09-15 08:35:55.176164-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:courier] <private> all couriers have finished processing server bag | |
| 2026-09-15 08:35:55.176164-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:stream] <private>: Delegates have processed server bag update, checking if stream should connect | |
| 2026-09-15 08:35:55.176582-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider attempting to fetch BAA certs | |
| 2026-09-15 08:35:55.176632-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider fetching BAA cert | |
| 2026-09-15 08:35:55.178997-0700 0x3e8 Error 0x176f 133 0 apsd: (CryptoTokenKit) [com.apple.CryptoTokenKit:sepkey] <sepk:* kid=0000000000000000>: (apsd) unable to generate key: error e00002e2(-536870174) ACL=<SecAccessControlRef: dk;ock(true);odel(true);osgn(true);oa(true);okd(true)> params=<AKSp:{acmh:###,ag:[],ed:{acl:{ock:true,odel:true,osgn:true,oa:true,okd:true}}}> | |
| 2026-09-15 08:35:55.179032-0700 0x3e8 Error 0x176e 133 0 apsd: (Security) [com.apple.security:seckey] SecKeyCreateRandomKey_ios failed: Error Domain=NSOSStatusErrorDomain Code=-25308 "Failed to generate keypair" (errKCInteractionNotAllowed / errSecInteractionNotAllowed: / Interaction is not allowed with the Security Server.) UserInfo={numberOfErrorsDeep=0, NSDescription=Failed to generate keypair, NSUnderlyingError=0x7c56d55fe0 {Error Domain=NSOSStatusErrorDomain Code=-25308 "<sepk:* kid=0000000000000000>: unable to generate key" UserInfo={NSDebugDescription=<sepk:* kid=0000000000000000>: unable to generate key, AKSError=-536870174}}} | |
| 2026-09-15 08:35:55.179085-0700 0x2b5 Default 0x0 133 0 apsd: (DeviceIdentity) Error Domain=com.apple.MobileActivation.ErrorDomain Code=-1 "Failed to create reference key." UserInfo={NSLocalizedDescription=Failed to create reference key., NSUnderlyingError=0x7c56d560d0 {Error Domain=com.apple.MobileActivation.ErrorDomain Code=-1 "Failed to create ref key." UserInfo={NSLocalizedDescription=Failed to create ref key., NSUnderlyingError=0x7c56c55350 {Error Domain=NSOSStatusErrorDomain Code=-25308 "Failed to generate keypair" (errKCInteractionNotAllowed / errSecInteractionNotAllowed: / Interaction is not allowed with the Security Server.) UserInfo={numberOfErrorsDeep=0, NSDescription=Failed to generate keypair, NSUnderlyingError=0x7c56d55fe0 {Error Domain=NSOSStatusErrorDomain Code=-25308 "<sepk:* kid=0000000000000000>: unable to generate key" UserInfo=0x7c571c8860 (not displayed)}}}}}} | |
| 2026-09-15 08:35:55.179108-0700 0x2b5 Default 0x0 133 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider failed to obtain a BAA cert, error: Error Domain=com.apple.MobileActivation.ErrorDomain Code=-1 UserInfo={NSLocalizedDescription=<private>, NSUnderlyingError=0x7c56d560d0 {Error Domain=com.apple.MobileActivation.ErrorDomain Code=-1 UserInfo={NSLocalizedDescription=<private>, NSUnderlyingError=0x7c56c55350 {Error Domain=NSOSStatusErrorDomain Code=-25308 UserInfo={numberOfErrorsDeep=0, NSDescription=<private>, NSUnderlyingError=0x7c56d55fe0 {Error Domain=NSOSStatusErrorDomain Code=-25308 UserInfo=0x7c571c8860 (not displayed)}}}}}} |
Based on the information discussed in this post in the Apple Developer Forums, this logging appears to indicate the following:
- The macOS VM is trying to get a key from Secure Enclave. macOS VMs do not have Secure Enclave, so this effort fails.
- Without the key, a separate process called MobileActivation cannot create a reference key.
- Without the reference key from the MobileActivation process, a BAA device identity certificate cannot be retrieved.
In the logging on my end, this process repeats multiple times.
When I attempted to enroll a macOS VM running macOS 26.6.2 using the test procedure described above, I saw the following logging:
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
| 2026-09-15 10:40:39.275906-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] <private>: Identity provider has processed server bag update, user courier finished processing config | |
| 2026-09-15 10:40:39.275909-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] <private> user courier finished processing server bag (1/2) | |
| 2026-09-15 10:40:39.275911-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] <private>: Identity provider has processed server bag update, user courier finished processing config | |
| 2026-09-15 10:40:39.275911-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] <private> user courier finished processing server bag (2/2) | |
| 2026-09-15 10:40:39.275911-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] <private> all couriers have finished processing server bag | |
| 2026-09-15 10:40:39.275912-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:stream] <private>: Delegates have processed server bag update, checking if stream should connect | |
| 2026-09-15 10:40:39.275914-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider attempting to fetch BAA certs | |
| 2026-09-15 10:40:39.275994-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider fetching BAA cert | |
| 2026-09-15 10:40:39.291432-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider obtained BAA certs! | |
| 2026-09-15 10:40:39.362477-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider attempting to fetch BAA certs | |
| 2026-09-15 10:40:39.362538-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider fetching BAA cert | |
| 2026-09-15 10:40:39.366687-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider obtained BAA certs! | |
| 2026-09-15 10:40:39.782712-0700 0x65d Default 0x0 332 0 apsd: [com.apple.apsd:courier] APSBAAClientIdentityProvider signed nonce data with host VM identity! |
This appears to show the following:
- The macOS VM does not attempt to get a key from Secure Enclave
- The macOS VM successfully retrieves a BAA device identity certificate
- The macOS VM specifically identifies itself as a virtual machine
From this evidence, my assumptions are as follows:
When a virtual machine running macOS Golden Gate 27.0.0 tries to register itself with APNS, macOS 27.0.0 erroneously assumes itself to be running on a Mac equipped with a Secure Enclave. That assumption is incorrect. That incorrect assumption by macOS then triggers a series of downstream failures which results in the macOS VM being unable to register itself with APNS.
If this is correct, the failure to register with APNS explains why the macOS VM never gets the additional configuration profiles and Jamf software components from my Jamf Pro MDM server. The macOS VM’s registration failure means the VM is unable to communicate with APNS and that’s essential to be able to communicate back to the MDM server. Failure to communicate with the MDM server means that the VM never receives anything from the MDM server.
That said, that’s my conclusions based on what I observed in the logs. I do not know for certain if my assumptions and resulting conclusions are correct. If someone has more information, please share it in the comments.
如有侵权请联系:admin#unsafe.sh