Reporting period: September 7–14, 2026Executive assessmentThe dominant intelligence deve 2026-9-14 15:15:50 Author: krypt3ia.wordpress.com(查看原文) 阅读量:11 收藏
Reporting period: September 7–14, 2026
Executive assessment
The dominant intelligence development this week is the further exposure of a Russian reconnaissance-to-sabotage architecture operating across NATO territory. Romania disrupted surveillance of NATO facilities and Ukrainian military logistics, Britain charged a citizen with allegedly identifying drone factories and preparing sabotage for a GRU-controlled network, Germany indicted an alleged Russian agent who helped a Moscow intelligence officer penetrate political and defense circles, and new reporting disclosed that the United States, Britain, and Norway disrupted a Russian GUGI exercise designed to covertly disable Arctic subsea cables. (Serviciul Român de Informații)
The significance is cumulative. These are not four versions of the same operation. They represent different layers of an intelligence-support ecosystem:

Russia’s apparent target set is increasingly concentrated on the infrastructure that enables NATO support to Ukraine: drone manufacturing, military transport, communications, aviation logistics, and strategic subsea connectivity.
A second major development is the emergence of evidence that AI is materially changing espionage tradecraft rather than merely assisting analysts. Anthropic disclosed Russia-nexus cyber operators using agentic AI to automate phishing, infrastructure acquisition, malware modification, persistence, and exfiltration, while PRC-aligned actors used AI to profile targets, identify vulnerabilities for recruitment, conduct covert outreach in languages operators did not speak, and generate intelligence reporting for state security organizations. (Anthropic)
Key judgment: Russia currently presents the clearest near-term espionage-to-sabotage threat against NATO. China presents a different but increasingly scalable intelligence threat in which AI, commercial contractors, surveillance systems, and traditional HUMINT recruitment are converging.
On September 8, Romania’s domestic intelligence service, SRI, announced that it had disrupted a Russian-coordinated sabotage operation involving a Russian citizen resident in Romania. The suspect had been under surveillance since February.
According to SRI, he photographed or filmed:
- communications centers
- Romanian military bases used by NATO allies
- national-security institutions
- critical infrastructure
- and Ukrainian Antonov cargo aircraft operating in Romania
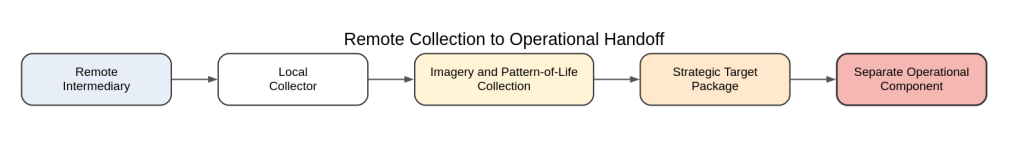
SRI says an intermediary instructed the suspect to collect imagery of military targets and that the methodology resembled Russian-directed sabotage networks previously disrupted in Romania and elsewhere in Europe.
Tradecraft
The workflow is straightforward:

The collector does not necessarily need access to classified information. Photography can reveal aircraft schedules, security posture, facility access, vehicle movement, storage areas, communications infrastructure, and vulnerabilities.
Assessed objective
The presence of Ukrainian Antonov aircraft in the collection requirement is particularly important. It links the activity directly to the Ukraine military-logistics chain, rather than general political espionage.
Possible downstream uses include:
- sabotage planning
- drone targeting
- explosive-device placement
- timing attacks against aircraft
- disruption of NATO logistics
- or identifying vulnerabilities for subsequent operators
Veracity
Incident and collection activity: high confidence.
Russian coordination: high-moderate confidence.
SRI made the attribution publicly and says national and foreign partner services participated in the investigation. Reuters independently confirmed the announcement.
Disinformation risk
Moderate.
Moscow routinely denies involvement in European sabotage. Public evidence identifying the intermediary and chain back to a specific Russian intelligence service has not yet been released.
British prosecutors charged Joshua Cammidge, 31, under the National Security Act on September 9 with assisting a foreign intelligence service and preparing an act of sabotage. (Crown Prosecution Service)
The Crown Prosecution Service alleges that Cammidge communicated with someone believed to represent the GRU Volunteer Corps, which British authorities describe as controlled by Russian military intelligence.
At his September 10 court appearance, prosecutors alleged that he had:
- researched four drone-manufacturing locations around Swindon,
- supplied Google Maps images of their locations,
- reported activity at one facility,
- conducted physical reconnaissance,
- researched a Wi-Fi jamming device,
- and offered to conduct sabotage. (ITVX)
He denies intending to carry out sabotage. The allegations have not been proven.
Tradecraft
This case is exceptionally useful analytically because it shows the potential escalation ladder from information collection to direct action:

The intelligence collector and prospective saboteur may be the same individual.
Assessed objective
The apparent target set is the British drone industrial base.
That directly overlaps with:
- Russian intelligence collection against European drone manufacturers,
- the Romanian surveillance of Ukrainian military aircraft,
- earlier German cases targeting companies supplying drones to Ukraine,
- and Russian cyber collection against drone technology.
Veracity
Charges: very high confidence.
Underlying Russian operational direction: moderate-high confidence pending trial.
The CPS and Metropolitan Police explicitly identify the alleged foreign-intelligence relationship.
Disinformation risk
Low-moderate.
The primary analytic danger is premature conversion of criminal allegations into adjudicated fact.
Reuters disclosed on September 10 that the United States, United Kingdom, and Norway disrupted a covert Russian underwater operation near Svalbard earlier this year. (Reuters)
According to two Western officials, Russia’s Main Directorate for Deep Sea Research, GUGI, used deep-sea submersibles to simulate deployment of technology designed to disable subsea cables while minimizing forensic evidence. Allied forces tracked and confronted the Russian vessels, causing the exercise to terminate.
No cable was damaged.
The target environment is strategically important. Two approximately 1,400-kilometer fiber-optic cables connect Svalbard with mainland Norway and carry data from SvalSat, a major satellite ground station that is part of NASA’s Near Space Network.
Tradecraft
This represents strategic technical intelligence and covert-action preparation rather than ordinary espionage.
The operational concept appears designed around:

Subsea infrastructure is attractive because physical damage can initially resemble accidental cable failure, commercial-anchor damage, or natural events.
Strategic objective
Western officials reportedly believe the capability was being rehearsed for possible conflict with NATO. Some U.S. intelligence analysts are concerned Russia could attempt to test Article 5, with subsea infrastructure potentially forming part of such an operation.
A cable attack could affect:
- satellite data,
- financial connectivity,
- military communications,
- civil telecommunications,
- intelligence collection,
- and Arctic situational awareness.
Connection to Ratcliffe Moscow visit
Reuters additionally reports that CIA Director John Ratcliffe’s August Moscow visit was partly intended to warn Russia against escalating sabotage operations in Europe. Reuters could not determine whether the GUGI operation was specifically discussed. That substantially reinforces the assessment from the earlier Ratcliffe special brief: Washington’s concern appears focused less on conventional invasion than on ambiguous Russian operations below the conventional-war threshold.
Veracity
Existence of allied interception: moderate-high confidence.
Exact Russian weapon capability and intended wartime employment: moderate confidence.
The report is based on two Western officials and supporting British MOD imagery, but the classified system itself has not been publicly demonstrated.
Disinformation risk
Moderate.
This is precisely the kind of covert capability around which both operational secrecy and strategic signaling can distort public descriptions. The basic event is credible; claims about the technology’s precise capabilities should remain provisional.
German federal prosecutors filed charges against German-Ukrainian citizen Ilona W. on September 7, disclosed publicly on September 14, alleging intelligence-agent activity for Russia. (AOL.com)
Prosecutors allege she maintained contact from at least October 2023 with a professional Russian intelligence officer assigned to the Russian embassy in Berlin. Her utility appears to have come from legitimate social and professional access. She operated a marketing agency and headed a lobbying organization that gave her contacts in German political, military, and defense-industry circles.
She allegedly:
- identified high-level political events
- enabled her Russian contact to attend some under false identities
- helped him build his own network of contacts
- identified potentially recruitable individuals
- approached people connected with the Defense Ministry and defense industry
- and collected information concerning German defense policy
Earlier investigation also concerned defense-industry locations, drone tests, and planned drone deliveries to Ukraine. (tagesschau.de)
Tradecraft
This resembles a classic access-agent model. The most valuable function was potentially not the information she personally collected. It was her ability to create introductions between a Russian intelligence officer and people he otherwise could not approach safely.
The progression would be:

The alleged Russian officer’s diplomatic status also offered legal and operational protection until Germany expelled him. (rbb24.de)
Assessed objective
German:
- defense policy,
- Ukraine-support planning,
- drone capabilities,
- defense-industrial personnel,
- and potential human sources.
Veracity
High-moderate confidence.
The indictment means German federal prosecutors believe evidence is sufficient for trial. It remains an allegation until adjudicated.
Intelligence significance
This case provides the traditional HUMINT counterpart to Russia’s disposable-proxy model.
Russia appears to be operating simultaneously through:

Anthropic’s September threat-intelligence report provides one of the clearest public examples yet of agentic AI becoming operational infrastructure for state-nexus espionage. Anthropic tracks an actor as GTG-20006 and says its attribution is consistent with public reporting linking the activity to Midnight Blizzard, while noting a Russian-speaking operator and tradecraft consistent with Russian state-nexus espionage. (Anthropic)
Targets included:
- Ukrainian government organizations,
- military and intelligence entities,
- European governments,
- diplomatic missions,
- defense organizations,
- U.S. foreign-policy-linked individuals,
- and drone manufacturers and suppliers.
AI-enabled tradecraft
The actor reportedly automated significant portions of:

When automated monitoring detected that a security product recognized a malware sample, AI agents could iteratively modify and rebuild it until detection ceased. (Anthropic)
The actor also used compromised hotel Wi-Fi providers to hijack DNS resolution and target selected guests, particularly Ukrainian officials and drone-sector personnel.
It additionally:
- compromised WhatsApp accounts,
- silently exported conversations,
- attacked government remote-access infrastructure,
- stole drone manufacturers’ mailboxes,
- obtained a proprietary drone-vision SDK,
- and reverse-engineered hardware, supplier dependencies, and unreleased products.
Assessed objective
The target set strongly emphasizes:

This directly overlaps with Russia’s physical surveillance and sabotage requirements exposed in Romania and Britain.
Veracity
Technical activity: high confidence.
Specific Midnight Blizzard attribution: moderate confidence.
Anthropic deliberately states that its attribution is consistent with public reporting rather than presenting a definitive government attribution.
Intelligence significance
The important development is not simply that an intelligence actor “used AI.”
AI appears to be reducing the labor required to maintain bespoke offensive infrastructure.
That could allow relatively small teams to operate at a tempo previously requiring significantly larger development and operations staffs.
The same Anthropic report describes a China-based operation targeting Uyghurs and Uyghur military formations in Syria, including individuals with possible access to formations incorporated into the new Syrian Army. Anthropic assesses with low confidence that the operator was a contractor supporting PRC state security rather than a Chinese state-security organization directly.
The actor reportedly monitored more than 100 WhatsApp groups and dozens of Telegram channels and converted the collected data into targeting profiles.
Potential vulnerabilities included:
- financial problems
- ideological disillusionment
- family separation
- and relatives remaining in Xinjiang
The actor then used AI to conduct multi-day covert recruitment conversations in Syrian Arabic despite apparently not speaking Arabic, translating responses, checking dialect and cultural plausibility, coaching deceptive communications, and formatting intelligence for handoff.
Tradecraft evolution
This is materially different from AI simply drafting a phishing email.
The system assisted with:

That covers much of a traditional HUMINT spotting and development cycle.
Parallel PRC operations
Anthropic also identified China-based actors conducting surveillance against:
- Hong Kong democracy activists
- Uyghur advocacy groups
- Tibetan organizations
- Falun Gong
- Taiwanese Christian organizations
- Catholic religious leaders
- and overseas human-rights organizations
One PRC-linked religious-affairs operation used AI to produce intelligence dossiers that explicitly identified exploitable “leverage” against subjects.
Assessed objective
The collection priorities are consistent with:
- transnational repression
- diaspora surveillance
- recruitment of sources
- penetration of Uyghur organizations
- religious and political control
- and identification of individuals usable by Chinese state security
Veracity
Observed platform activity: high confidence.
PRC alignment: high-moderate.
Specific contractor-to-state command relationship: low-moderate.
This qualification matters. Anthropic itself uses low confidence for the contractor assessment.
Huawei’s long-running U.S. prosecution entered trial proceedings in New York this week. Prosecutors accuse the company of racketeering, sanctions-related offenses, fraud, and systematic theft of technology from U.S. companies over many years. Huawei denies wrongdoing and says the prosecution is politically motivated. (Reuters)
The espionage relevance is principally economic and technological intelligence, rather than clandestine state espionage in the conventional sense.
Because the allegations are historical and highly contested, this brief does not treat the trial itself as evidence that Huawei conducted intelligence activity on behalf of the PRC government.
Veracity
Existence and content of criminal allegations: very high.
Underlying criminal responsibility: unresolved at trial.
PRC intelligence direction: not established by the current proceedings.
Disinformation risk
High.
The case exists within intense U.S.-China strategic competition, creating incentives on both sides to collapse legal allegations into broader geopolitical narratives.
Analytical language should remain narrower than political rhetoric.
Russia: reconnaissance and sabotage now appear increasingly integrated
This week’s Russian cases align unusually well and appear to reflect a broader intelligence-to-action model spanning collection, access, technical preparation, and potential sabotage. In Romania, the activity centers on strategic imagery collection against NATO bases, communications infrastructure, critical infrastructure, and Ukrainian aircraft. In Britain, the focus shifts toward operational reconnaissance, including identifying drone factories, providing geolocation, investigating jamming systems, and allegedly preparing sabotage. In Germany, Russia appears to have used an access agent to map political, defense, drone, and industrial networks while facilitating direct engagement between a professional Russian intelligence officer and potential targets. In the Arctic, Russian activity is focused on developing technical means to covertly disable NATO-relevant subsea communications. The cyber dimension complements these efforts by targeting governments, drone manufacturers, communications networks, and infrastructure for both intelligence collection and access. Taken together, the cases suggest a coordinated pattern in which Russia is building target knowledge, access, and technical options that could support future disruption or sabotage operations against NATO states.
The resulting operational model is:

Assessment: high confidence.
This does not prove that every Russian espionage case feeds an attack plan. It does show that multiple independent investigations now expose components of the same operational continuum.
One target category recurs across collection disciplines: unmanned systems.
This week alone:
- Romanian intelligence identified surveillance of Ukrainian Antonov logistics supporting Ukraine.
- British prosecutors allege reconnaissance against four drone-production facilities.
- German investigations involve information about drone testing and Ukraine deliveries.
- Anthropic observed Russia-nexus cyber theft from drone-component manufacturers and a drone-vision technology developer. (Serviciul Român de Informații)
This strongly suggests Russian collection requirements are focused not merely on finished Ukrainian weapons systems but the industrial ecosystem supporting drone production:
- component suppliers
- firmware
- optics
- vision systems
- logistics
- manufacturing locations
- personnel
- and transportation
Confidence: high.
The PRC and Russia cases show two distinct operational applications.
Russia
AI increases the speed of technical espionage:

China
AI increases the scale of human intelligence and surveillance:

- The consequential development is that AI removes specialist bottlenecks.
- A Russian operator requires fewer malware developers.
- A Chinese operator does not necessarily require an Arabic-speaking case officer.
A surveillance organization can produce thousands of dossiers without corresponding analyst staffing. Anthropic describes one PRC religious-affairs intelligence office using AI to replace work formerly distributed across multiple analytical teams. (Anthropic)
Assessment: AI is becoming a capability multiplier for intelligence services, not an independent intelligence capability.
Russia / Romania
The underlying surveillance operation is strongly supported by SRI reporting and an international investigation. The publicly available evidence connecting the suspect to the full Russian command chain remains limited.
Veracity: high-moderate.
Russia / Britain
This is an active criminal proceeding. The GRU connection is a prosecution allegation, not a conviction.
Veracity: moderate-high.
GUGI cable operation
The report is highly credible but relies substantially on anonymous Western officials. Claims concerning a new sabotage technology should remain qualified.
Veracity: moderate-high.
Anthropic attribution
Anthropic’s telemetry provides unusually strong evidence about what actors actually did on its platform. Its state attribution judgments vary in confidence and should not be flattened into certainty.
Technical evidence: high.
Actor attribution: case-dependent, moderate to high.
Russian denial narrative
Moscow continues to deny responsibility for European sabotage operations. Given the increasing number of independently investigated cases across separate NATO jurisdictions, a blanket assertion that there is no Russian campaign is becoming increasingly difficult to reconcile with the evidence.
However, this does not justify automatic Russian attribution of every unexplained fire, drone sighting, communications failure, or infrastructure incident in Europe.
That would itself constitute analytical failure.
- GRU Volunteer Corps: identify digital recruitment infrastructure, handles, payment mechanisms, Telegram accounts, intermediaries, and connections between the British case and European sabotage investigations.
- Russian drone collection requirement: map known espionage, HUMINT, cyber, and sabotage cases involving drone manufacturers, component suppliers, logistics providers, optics, AI vision, and firmware.
- Romanian intermediary: identify the handler or intermediary directing imagery collection and determine whether the same individual or infrastructure appears in Poland, Germany, Britain, or Denmark.
- Ilona W. network: reconstruct the Russian embassy officer’s contact network, events attended under aliases, potential recruitment targets, and any defense-sector relationships established through the alleged access agent.
- GUGI: watch for vessel movements, Svalbard/Bear Gap activity, Russian special-purpose submarines, oceanographic cover, and unexplained failures affecting Norwegian or Arctic subsea infrastructure.
- Midnight Blizzard / GTG-20006: correlate Anthropic’s infrastructure and victimology with Microsoft and other vendor reporting, particularly hotel Wi-Fi compromise, WhatsApp companion-device abuse, and drone supply-chain collection.
- PRC AI-enabled HUMINT: monitor whether the Syrian Uyghur operation can be connected to identifiable MSS, MPS, United Front, Xinjiang security, or contractor organizations.
- Information operations following sabotage: monitor narratives designed to generate competing attributions immediately after incidents, especially claims blaming Ukraine, criminals, extremists, or technical malfunction before forensic investigations mature.
The strongest intelligence signal this week is not simply that Russia continues to spy on NATO countries.
It is that Russian intelligence collection increasingly appears designed to answer questions required for physical operations:
- Where are the factories?
- When are the aircraft present?
- Who enters the facility?
- What communications systems are used?
- Where are the vulnerable network points?
- How can access be disrupted?
- Which local person can perform the task?
- How can critical infrastructure be disabled without immediately identifying Russia?
The operational boundary between espionage and sabotage is consequently eroding.
At the same time, Chinese intelligence-related activity illustrates another structural shift. AI can allow a relatively small operator to conduct surveillance, target development, translation, personality assessment, recruitment preparation, and intelligence-report production across populations and languages at a scale previously requiring much larger organizations.
Current assessments
Russian espionage-to-sabotage activity against NATO: High confidence, elevated.
Russian collection against European/Ukrainian drone ecosystems: High confidence.
Russian preparation for attacks on strategic communications infrastructure: Moderate-high confidence.
PRC use of AI in surveillance and HUMINT-support operations: High confidence.
AI materially reducing manpower requirements for state cyberespionage: High confidence.
The principal warning indicator going forward is therefore reconnaissance that looks too mundane to be espionage. Photography, facility details, hotel Wi-Fi compromise, maps, employee identification, logistics schedules, and supplier data may increasingly represent the upstream portion of an operation whose destructive purpose becomes visible only later.
如有侵权请联系:admin#unsafe.sh