嗯,用户让我帮忙总结一篇文章的内容,控制在100字以内,而且不需要特定的开头。首先,我需要仔细阅读文章内容,抓住主要观点。 文章主要讨论了模糊测试(Fuzzing)中的一个关键问题:长时间运行后覆盖率 plateau,无法继续增加。现有的解决方案是使用新的种子输入或变异操作符。但作者观察到即使在Google多年的努力下,Syzbot在Linux内核中的模糊测试也达到了 plateau。 于是他们提出了一种新方法:Sysyphuzz。这种方法通过分析基本块的执行频率,发现有些块执行次数极少,可能隐藏着漏洞。Sysyphuzz分为两个阶段:第一阶段收集现有语料库的数据,第二阶段通过boost delegator来决定哪些块需要加强,并进行上下文保留的变异。 总结下来,文章的核心是Sysyphuzz如何在覆盖率 plateau后,通过平衡基本块的执行频率来发现新漏洞。这种方法有效且开源,评估结果也优于syskaller。 现在需要将这些内容浓缩到100字以内,确保涵盖主要点:问题、解决方案、方法、效果。 </think> 文章探讨了模糊测试(Fuzzing)中覆盖率 plateau 的问题,并提出了一种名为 Sysyphuzz 的新方法。该方法通过分析基本块的执行频率,识别和加强较少被覆盖的区域以发现潜在漏洞。该技术分为两阶段:首先收集现有语料库数据;然后通过 boost delegator 决定哪些区域需要加强,并进行上下文保留的变异操作。实验表明该方法在 Linux 内核模糊测试中有效。 2026-3-2 08:45:48 Author: nebelwelt.net(查看原文) 阅读量:0 收藏
Fuzzing faces a key challenge: after running for an extensive time, coverage plateaus and will no longer increase despite extensive mutations. Only new seed inputs or mutation operators will likely change that. We have observed that for Syzbot fuzzing in the Linux kernel has essentially plateaued due to Google's multi-year fuzzing efforts.
Instead of blindly rerunning campaigns with slightly adjusted operators, we wondered if we can find bugs in already covered areas. We observed that execution frequency of basic blocks is heavily skewed with some basic blocks executed extremely frequently while many are executed rarely at all. On average, basic blocks are executed less than 30 times. Our goal was therefore to balance the execution frequency of basic blocks by boosting under-fuzzed areas. Our intuition is that bugs are hiding in these under-fuzzed areas.
Two key challenges when boosting under-fuzzed areas are (i) resource constraints and (ii) context-destroying mutations. First, adding new fuzzing tasks will deflect energy from other areas and blindly iterating on seeds that do not create new findings simply wastes energy. Second, these under-fuzzed basic block are hard to reach and often require precise system call sequences. Mutations therefore often destroy the context and make the target unreachable.
Sysyphuzz runs in two phases: first, we replay the existing corpus during a warm up phase to get approximate counts of under-fuzzed areas. During this time we simply count basic block execution frequencies along with creating a map between basic blocks and seeds. In the second phase, we introduce a boost delegator that tracks frequency of basic blocks to decide which ones should be boosted. During boost tasks, sysyphuzz checks that the target basic blocks remain reachable and then issues context-preserving mutations.
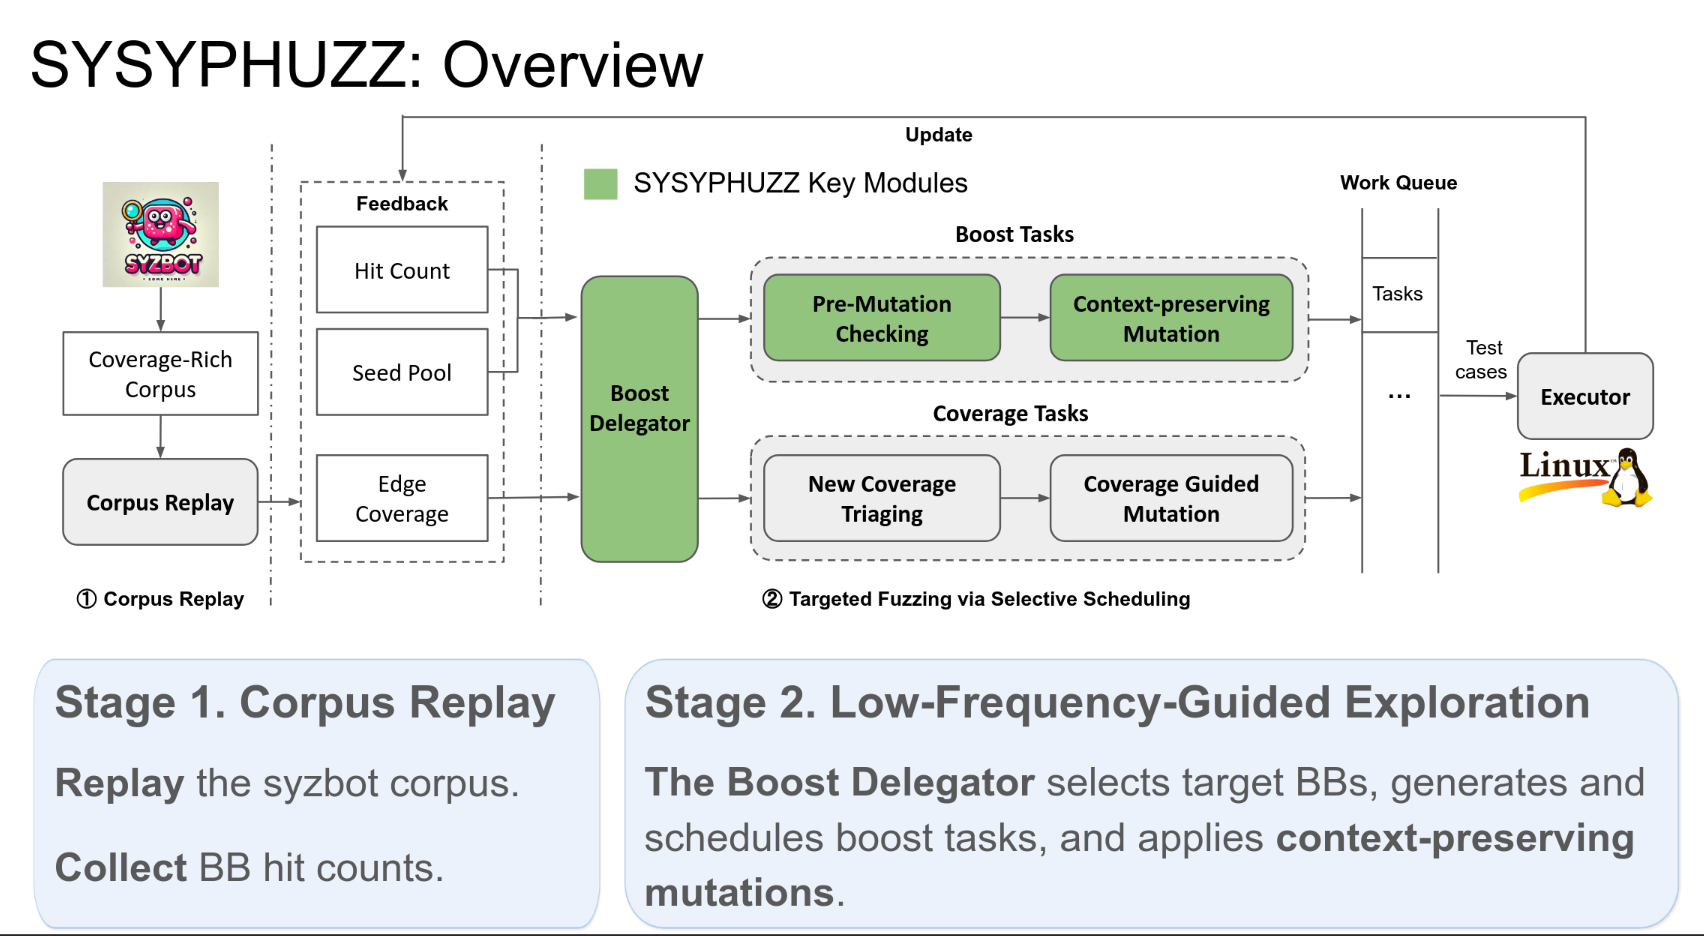
The sysyphuzz implementation is open source and we carefully evaluated it against syskaller. The exact evaluation details are in the paper.
The key takeaway of Sysyphuzz is that, after plateauing, fuzzers can still find bugs when focusing on under-fuzzed areas. For this, we need to track seeds that reach certain areas and carefully boost them.
This work was led by Zezhong Ren during his visit in the lab along with Han Zheng, Zhiyao Feng, Qinying Wang, Marcel Busch, Yuqing Zhang, and Chao Zhang. Zezhong deserves the majority of the credit for the hard work on the system, the evaluation, and the revision.
如有侵权请联系:admin#unsafe.sh