unSafe.sh - 不安全
我的收藏
今日热榜
公众号文章
导航
Github CVE
Github Tools
编码/解码
文件传输
Twitter Bot
Telegram Bot
Search
Rss
黑夜模式
Protecting organizations from AI-assisted executive impersonation and invoice fraud
Threat actors are increasingly improving their tactics to make suspicious emails look like legi...
2026-9-10 17:23:5 | 阅读: 14 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
invoice
defender
servicenow
security
Detect and disrupt AI-themed attacks with Microsoft Defender
Every wave of technology excitement creates a new opportunity for cyberattackers, and AI is no exce...
2026-9-10 16:0:0 | 阅读: 11 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
defender
themed
lure
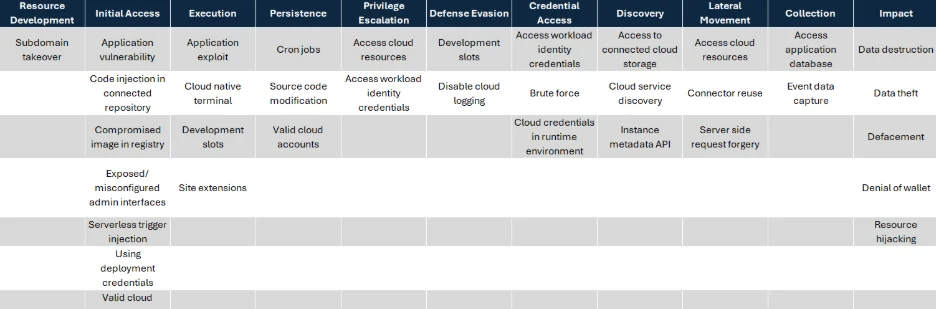
Threat Matrix: Mapping threats across cloud web applications
Microsoft introduces the cloud web applications threat matrix, a MITRE ATT&CK-aligned framework...
2026-9-9 21:30:0 | 阅读: 14 |
收藏
|
Microsoft Security Blog - www.microsoft.com
cloud
tactic
microsoft
malicious
workload
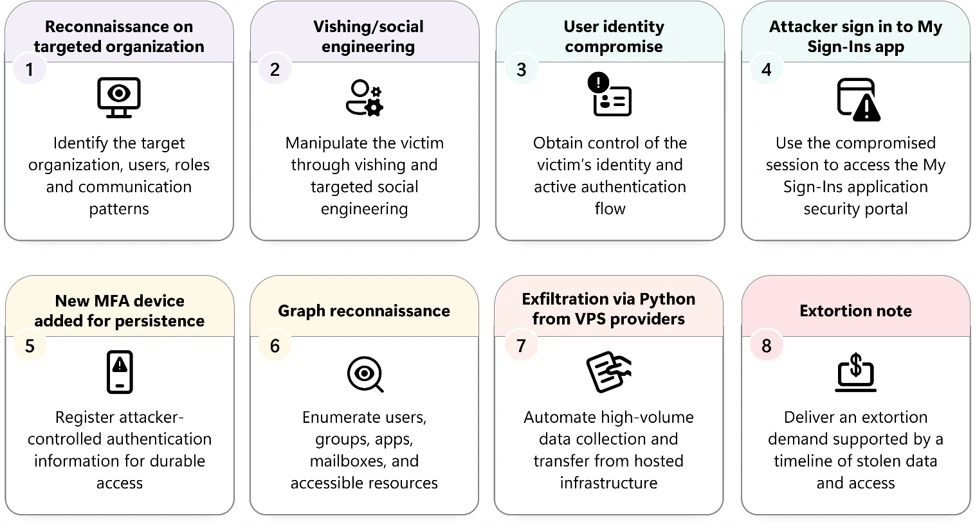
Passkey-themed social engineering leads to identity and cloud compromise
Microsoft Security Research is tracking active cloud-based intrusions spanning multiple account...
2026-9-9 17:41:18 | 阅读: 16 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
cloud
requesturi
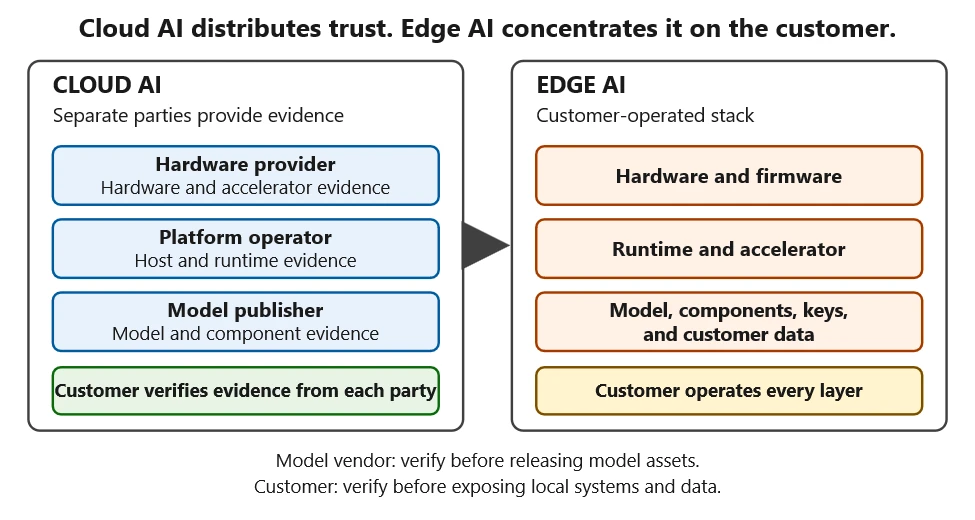
How to secure edge AI in customer-owned environments
Edge AI moves model execution, model IP, customer data, and system authority into infrastructur...
2026-9-4 19:10:10 | 阅读: 14 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
artifacts
approved
hardware
artifact
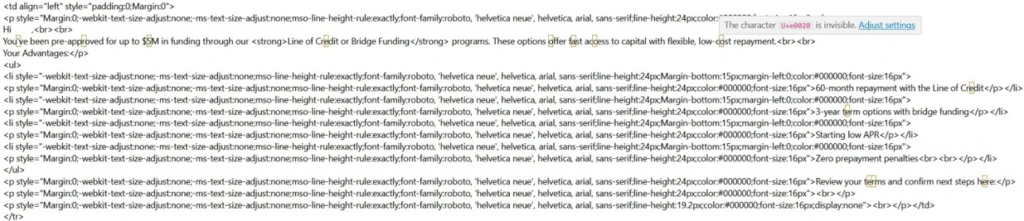
ASCII smuggling crosses over from AI prompt injection to phishing evasion
Microsoft researchers observed a high-volume phishing campaign using invisible Unicode tag char...
2026-9-3 16:0:0 | 阅读: 17 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
finance
invisible
phishing
security
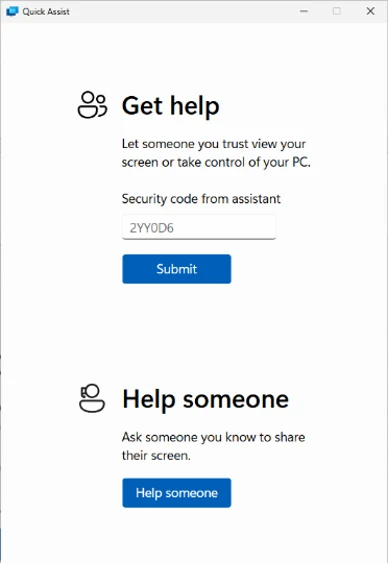
Impersonating IT support: how threat actors turn a remote session into enterprise-wide access
Microsoft Threat Intelligence has observed a human-operated intrusion campaign that abuses Micr...
2026-9-2 22:51:18 | 阅读: 20 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
remote
loader
malicious
defender
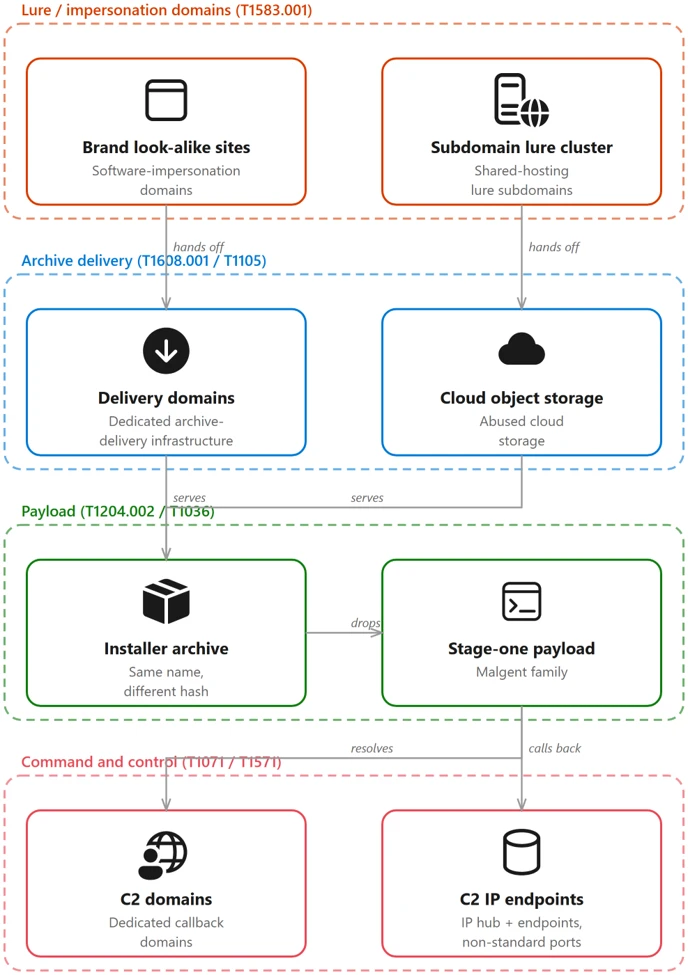
Counterfeit installers to system compromise: Tracking a deceptive software download campaign
Microsoft Defender Experts is tracking an active malware campaign that uses counterfeit softwar...
2026-9-1 22:48:28 | 阅读: 30 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
defender
payload
windows
stage
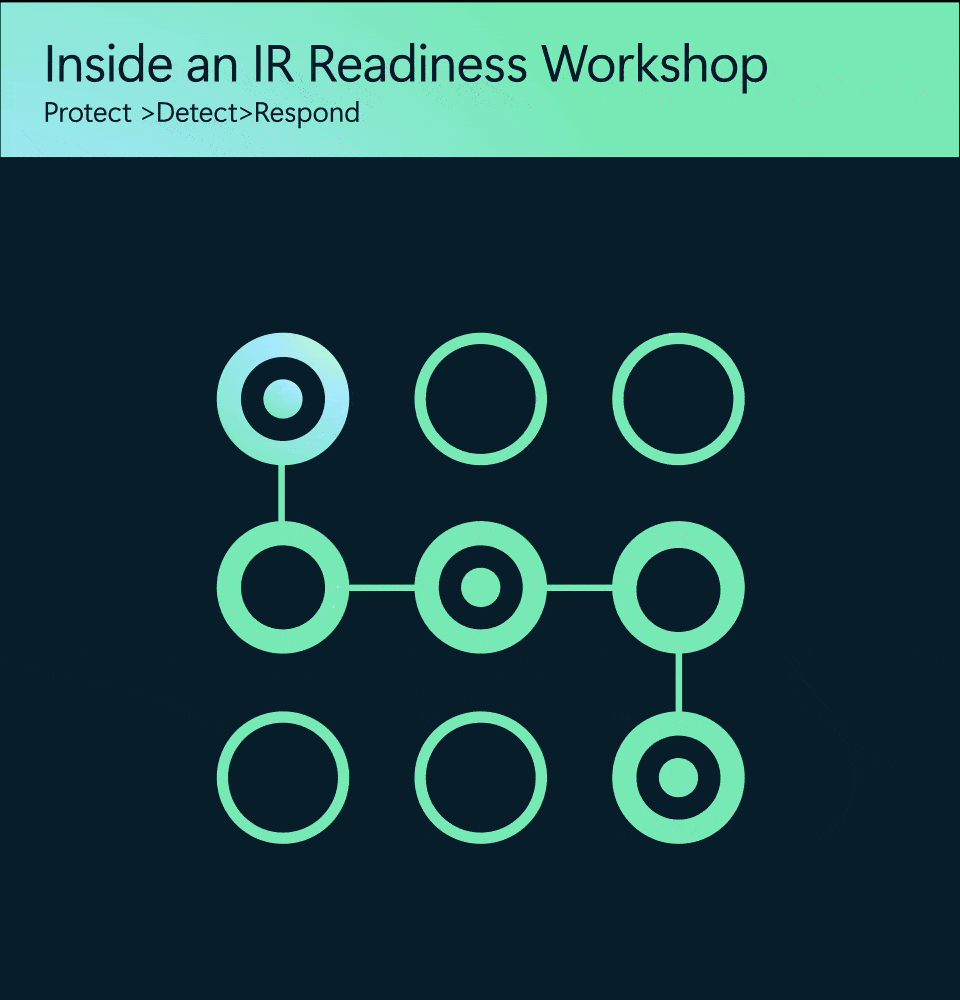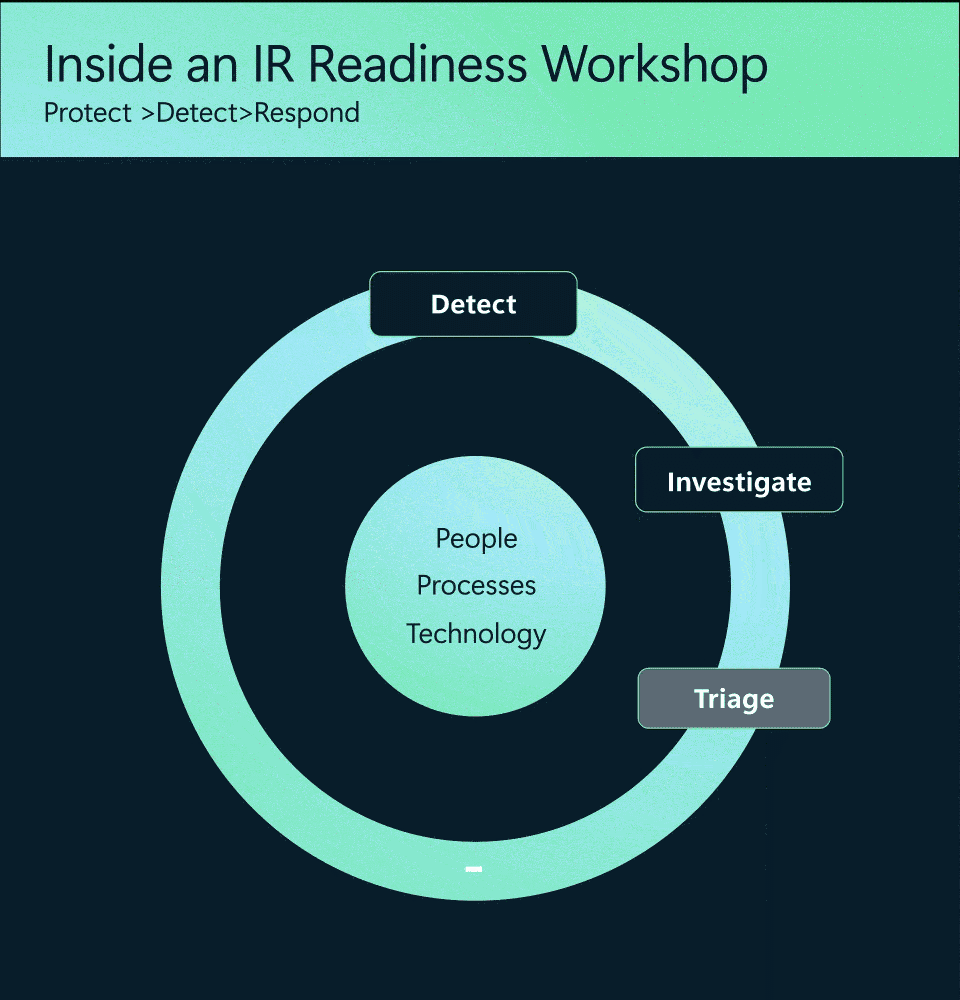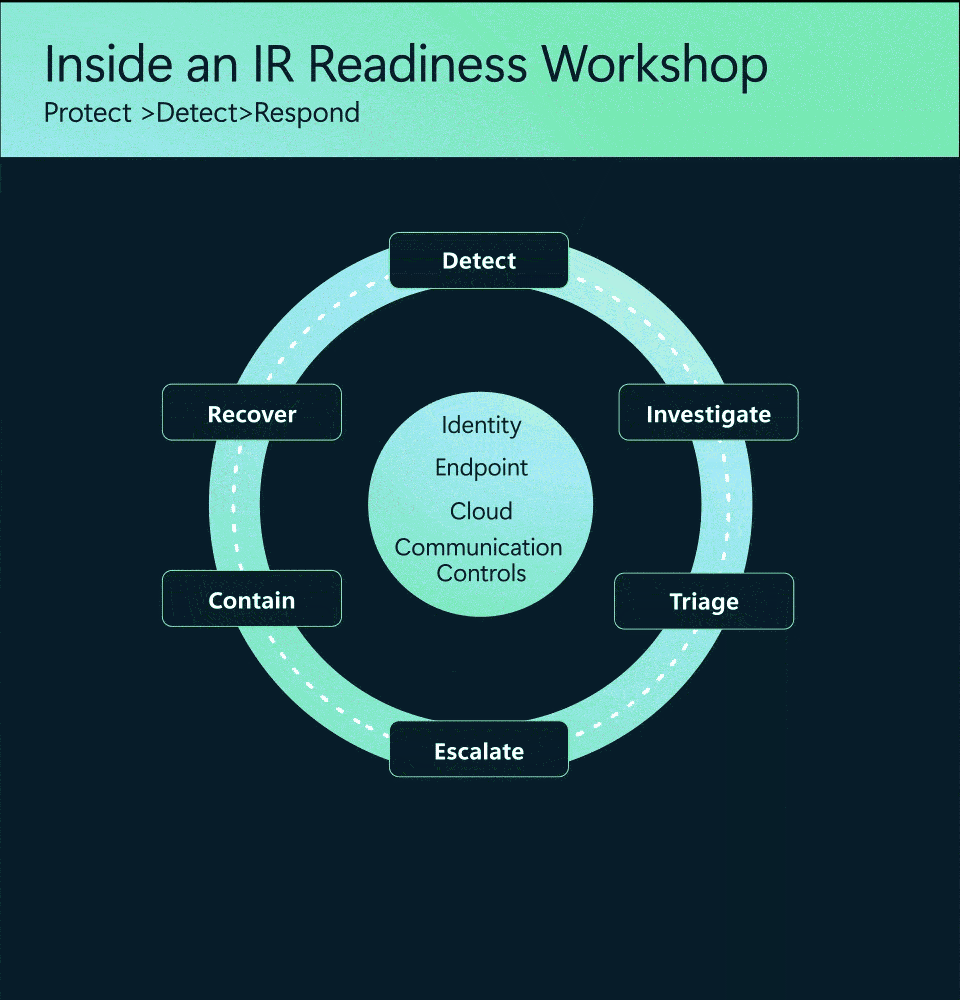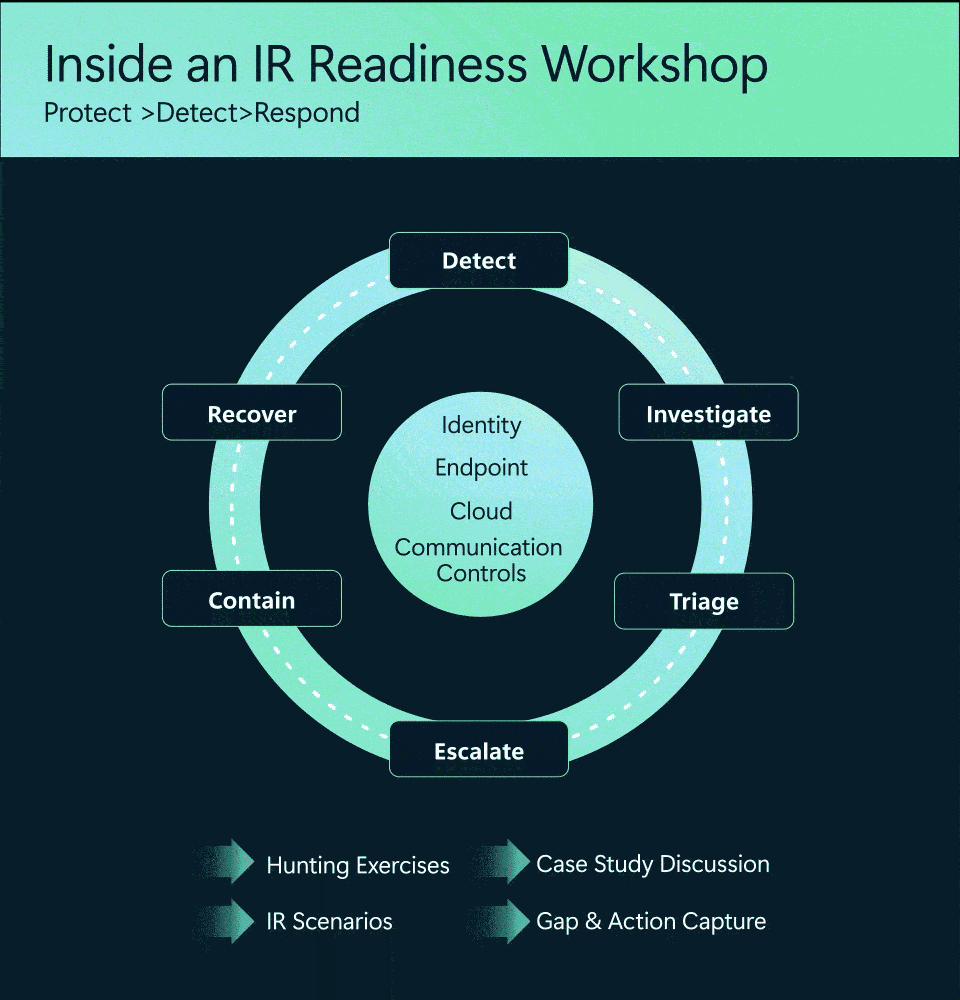
Cybersecurity IR Workshop: The workshop you shouldn’t miss
Cybersecurity incidents can unfold in hours, but response plans often fail at the point of exec...
2026-9-1 18:55:35 | 阅读: 15 |
收藏
|
Microsoft Security Blog - www.microsoft.com
workshop
dart
microsoft
processes
TerminalFix campaign deploys a reverse tunnel through multistage intrusion
Microsoft Threat Intelligence has observed a TerminalFix campaign, a variant of ClickFix, targe...
2026-8-29 03:43:27 | 阅读: 28 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
powershell
defender
dui70
malicious
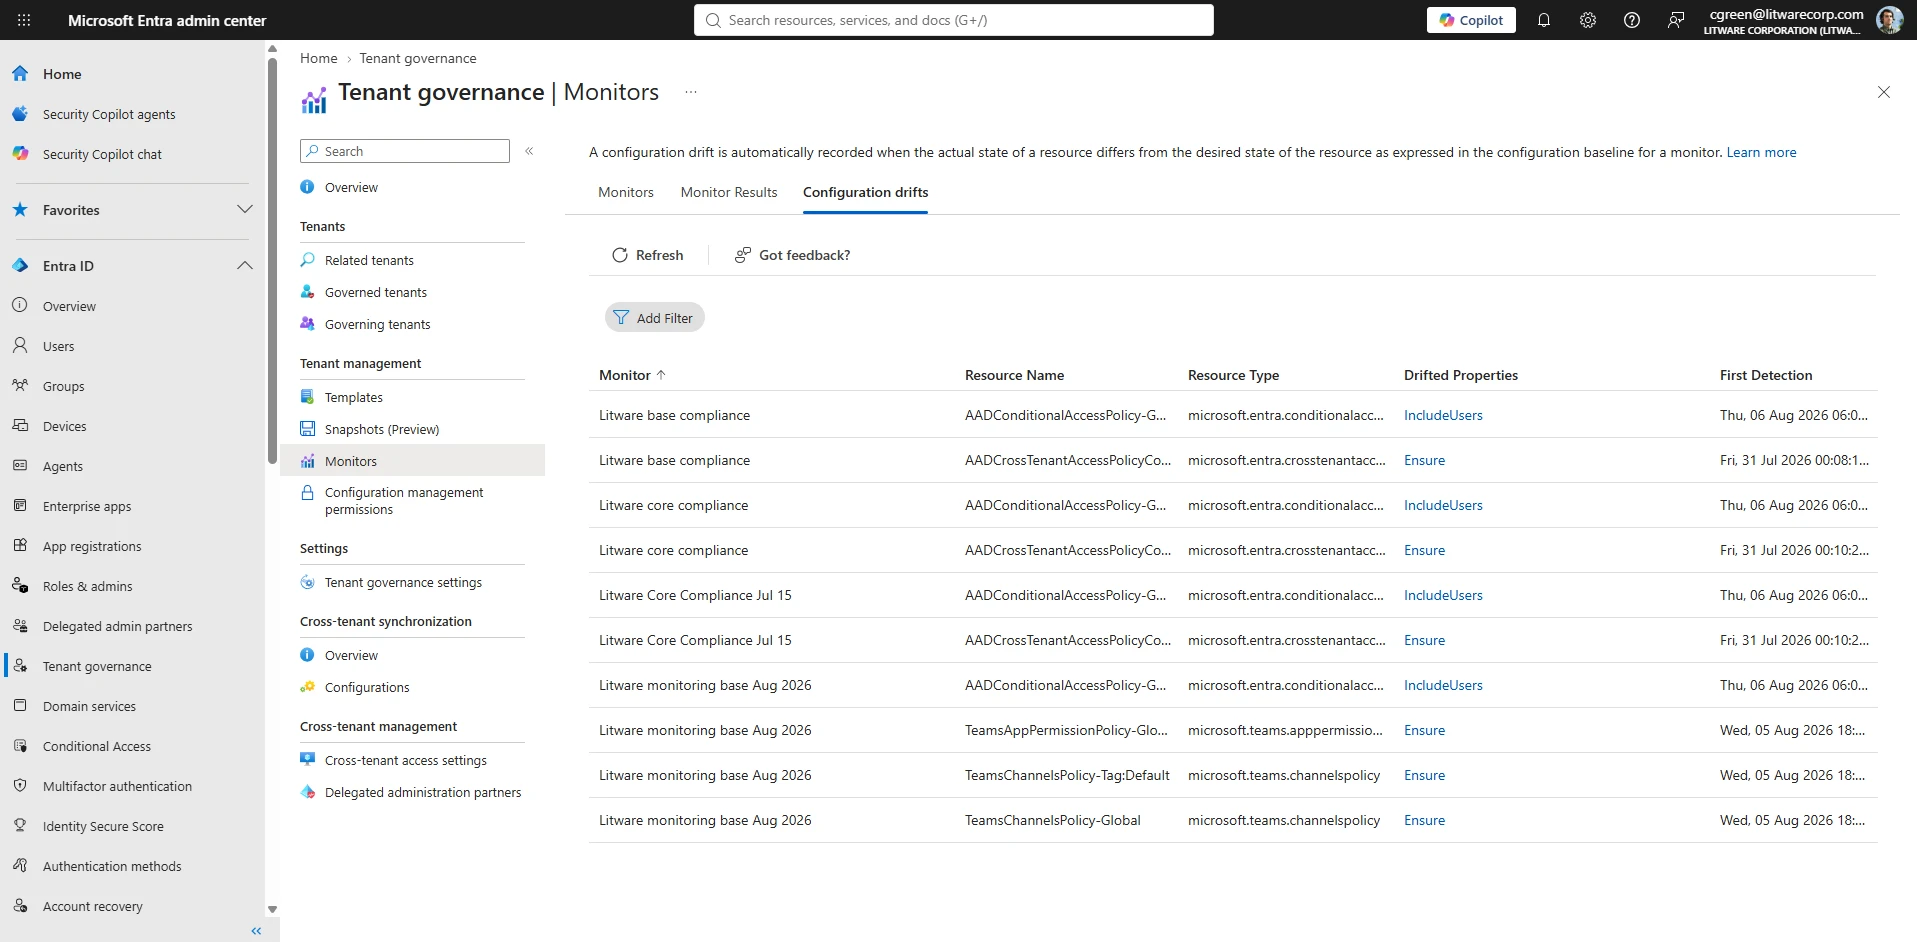
What’s new in Microsoft Security: August 2026
As organizations incorporate AI agents into more processes across business and operations, security...
2026-8-27 16:0:0 | 阅读: 15 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
security
defender
labeling
drift
When AI infrastructure becomes the target: Securing gateways and control points
AI is creating a new layer of enterprise infrastructure. Gateways, retrieval platforms, orchest...
2026-8-26 16:43:53 | 阅读: 18 |
收藏
|
Microsoft Security Blog - www.microsoft.com
litellm
database
microsoft
ragflow
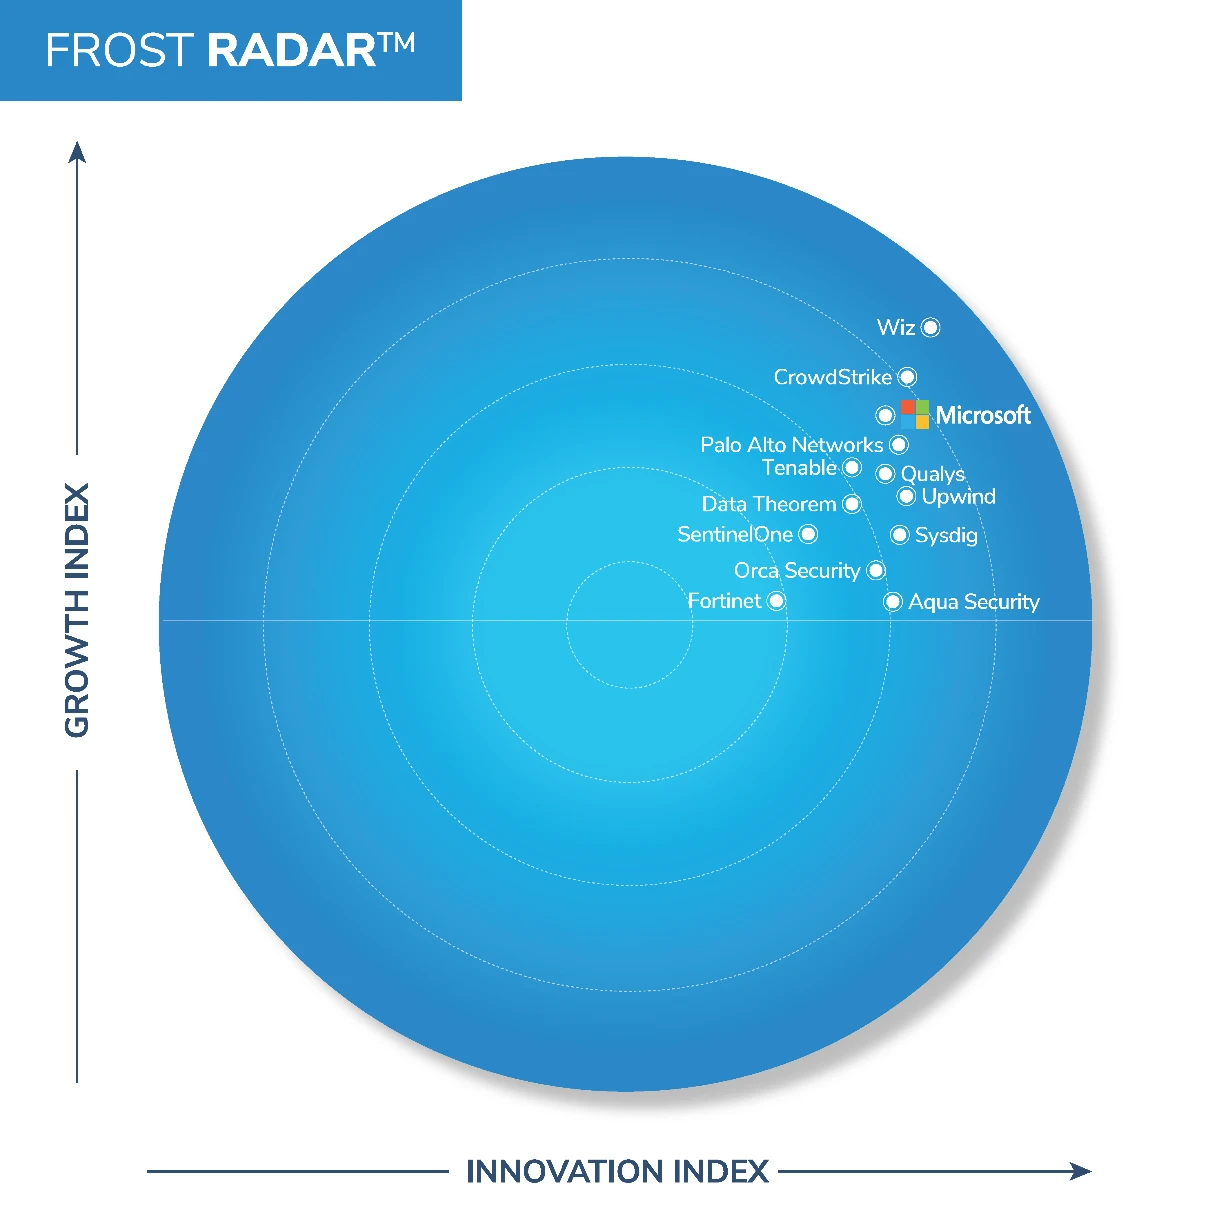
Microsoft named a Leader in the Frost Radar™: Cloud Workload Protection Platforms, 2026
Security teams are overwhelmed with findings but still struggle to answer a simple question: which...
2026-8-19 17:30:0 | 阅读: 30 |
收藏
|
Microsoft Security Blog - www.microsoft.com
cloud
security
microsoft
workload
frost
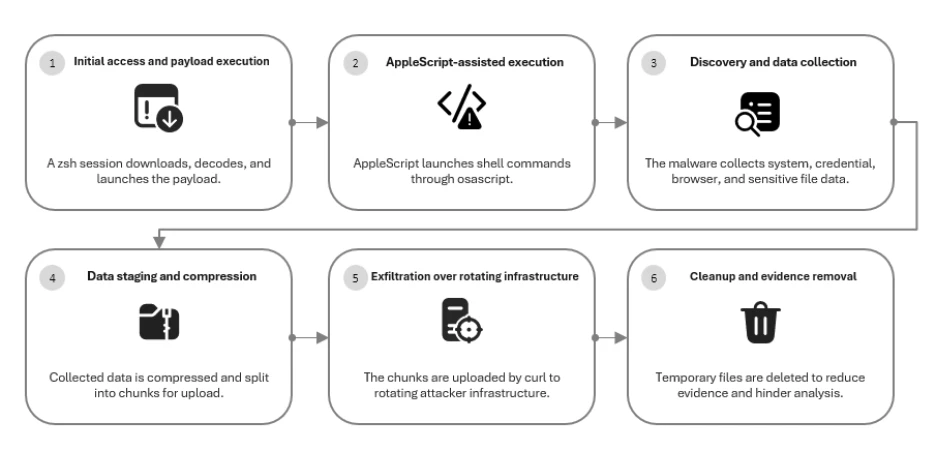
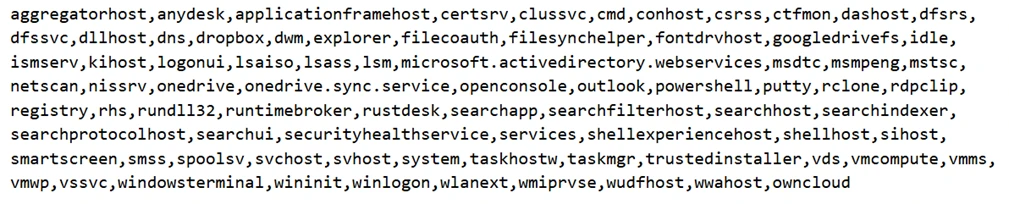
Hunting MacSync Stealer infrastructure through behavioral pivots
MacSync Stealer is a macOS-focused information stealer that relies on changing infrastructure t...
2026-8-18 17:8:28 | 阅读: 34 |
收藏
|
Microsoft Security Blog - www.microsoft.com
stealer
macsync
behavioral
microsoft
payload
Microsoft named a Leader in the 2026 IDC MarketScape for MDR/MXDR for the Enterprise
Security teams are being asked to defend a growing attack surface with fewer people and around the...
2026-8-10 16:0:0 | 阅读: 25 |
收藏
|
Microsoft Security Blog - www.microsoft.com
defender
microsoft
security
mdr
marketscape
DeadLock ransomware: Breaking down a Rust-based encryptor with decentralized recovery infrastructure
Microsoft Threat Intelligence tracks DeadLock ransomware as an emerging financially motivated o...
2026-8-10 15:0:0 | 阅读: 35 |
收藏
|
Microsoft Security Blog - www.microsoft.com
encryption
ransomware
microsoft
deadlock
defender
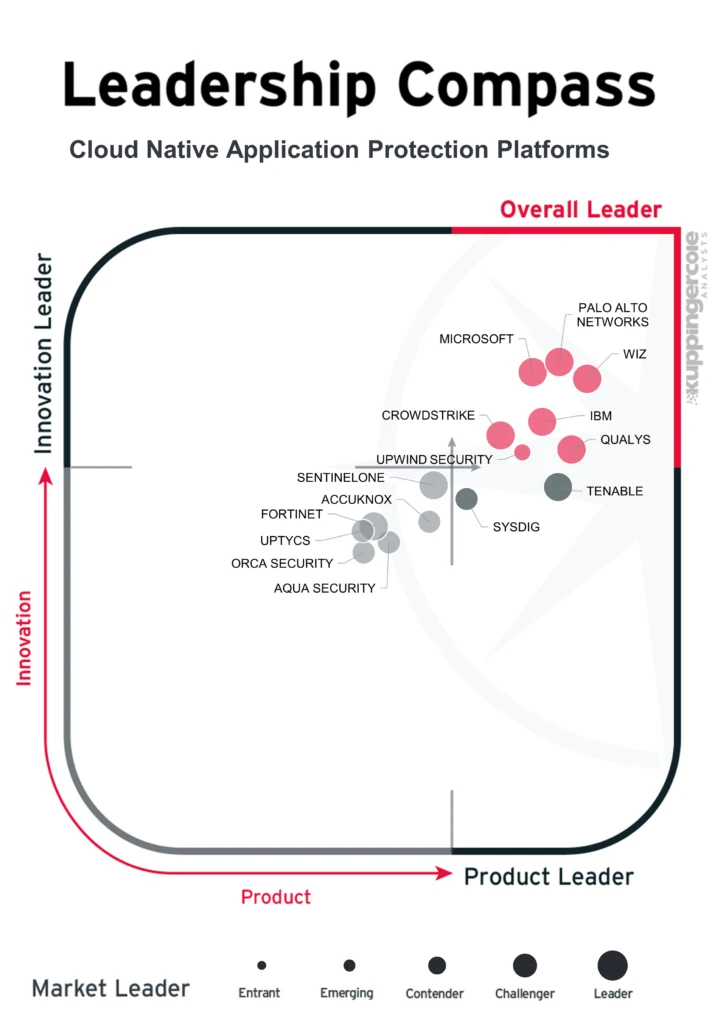
Microsoft named a Leader in the KuppingerCole Leadership Compass for Cloud Native Application Protection Platforms (CNAPP)
As organizations adopt AI, they must secure both cloud and AI environments through a unified securi...
2026-8-5 16:30:0 | 阅读: 33 |
收藏
|
Microsoft Security Blog - www.microsoft.com
cloud
security
posture
cnapp
prioritize
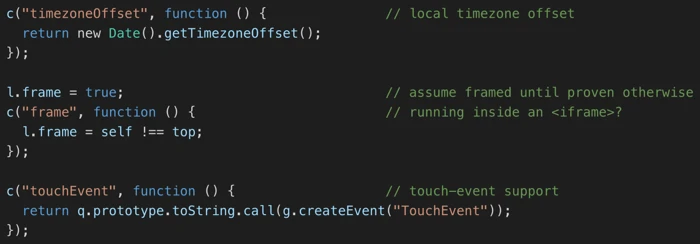
From open lures to cloaked gates: How a macOS ClickFix campaign learned to hide
Microsoft Threat Intelligence observed a macOS ClickFix campaign distributing infostealers, inc...
2026-8-5 15:48:39 | 阅读: 37 |
收藏
|
Microsoft Security Blog - www.microsoft.com
clickfix
microsoft
gate
lure
ChainDrop supply chain compromise: Anatomy of a self-propagating worm
Microsoft Threat Intelligence identified a large-scale npm supply chain attack affecting more t...
2026-8-4 23:46:41 | 阅读: 56 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
github
defender
payload
malicious
Advance Zero Trust for AI: New tools and guidance to secure AI agents and DevSecOps
The calculus of cybersecurity has changed. AI is reshaping how organizations build, deploy, operate...
2026-8-4 18:30:0 | 阅读: 38 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
microsoft
workshop
pillar
development
Previous
-1
0
1
2
3
4
5
6
Next