unSafe.sh - 不安全
我的收藏
今日热榜
公众号文章
导航
Github CVE
Github Tools
编码/解码
文件传输
Twitter Bot
Telegram Bot
Search
Rss
黑夜模式
Insights from the 2026 Microsoft Digital Defense Report
Every year, the Microsoft Digital Defense Report gives us an opportunity to step back from individu...
2026-10-1 14:0:0 | 阅读: 20 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
microsoft
identities
software
Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026
In the agentic era, the stakes are higher: AI agents now act with real access to your identitie...
2026-9-30 19:31:0 | 阅读: 25 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
microsoft
agents
ignite
2026
Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570
Microsoft Threat Intelligence identified and tracked exploitation of CVE-2026-73570, an unauthe...
2026-9-30 14:0:0 | 阅读: 41 |
收藏
|
Microsoft Security Blog - www.microsoft.com
zimbra
microsoft
defender
injection
Phishing Abuses RMM Tools for Persistent Access
In July 2026, Microsoft Defender Experts observed phishing campaigns targeting organizations ac...
2026-9-29 21:39:27 | 阅读: 36 |
收藏
|
Microsoft Security Blog - www.microsoft.com
msp360
rmm
microsoft
remote
Beyond source code: A path to the keys to the kingdom
What began as a single compromised identity quickly expanded into an organization’s development and...
2026-9-29 16:0:0 | 阅读: 30 |
收藏
|
Microsoft Security Blog - www.microsoft.com
cloud
development
dart
pipelines
microsoft
Star Blizzard refines phishing and malware delivery with the RedFlick technique
Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve thei...
2026-9-29 15:0:0 | 阅读: 27 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
2026
blizzard
phishing
redflick
NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence has identified NeedyMantis, a modular post-compromise malware fam...
2026-9-28 15:0:0 | 阅读: 29 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
needymantis
defender
loader
c2
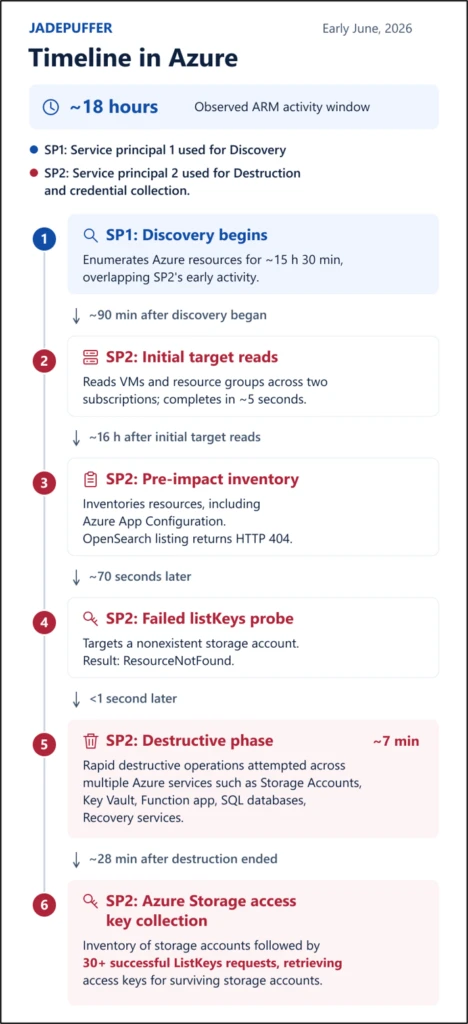
Storm-3168: Agentic-driven cloud attacks using compromised service principals
Microsoft Security Research has identified malicious cloud activity associated with JADEPUFFER,...
2026-9-25 15:35:8 | 阅读: 33 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
defender
destructive
security
cloud
Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments
Activity associated with Storm-2570, a ransomware affiliate linked to multiple ransomware paylo...
2026-9-24 16:0:0 | 阅读: 32 |
收藏
|
Microsoft Security Blog - www.microsoft.com
2570
ransomware
microsoft
defender
remote
What’s new in Microsoft Security: September 2026
AI agents are now running on employee devices, cloud platforms, and across developer workflows. Sec...
2026-9-24 16:0:0 | 阅读: 20 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
security
copilot
purview
labeling
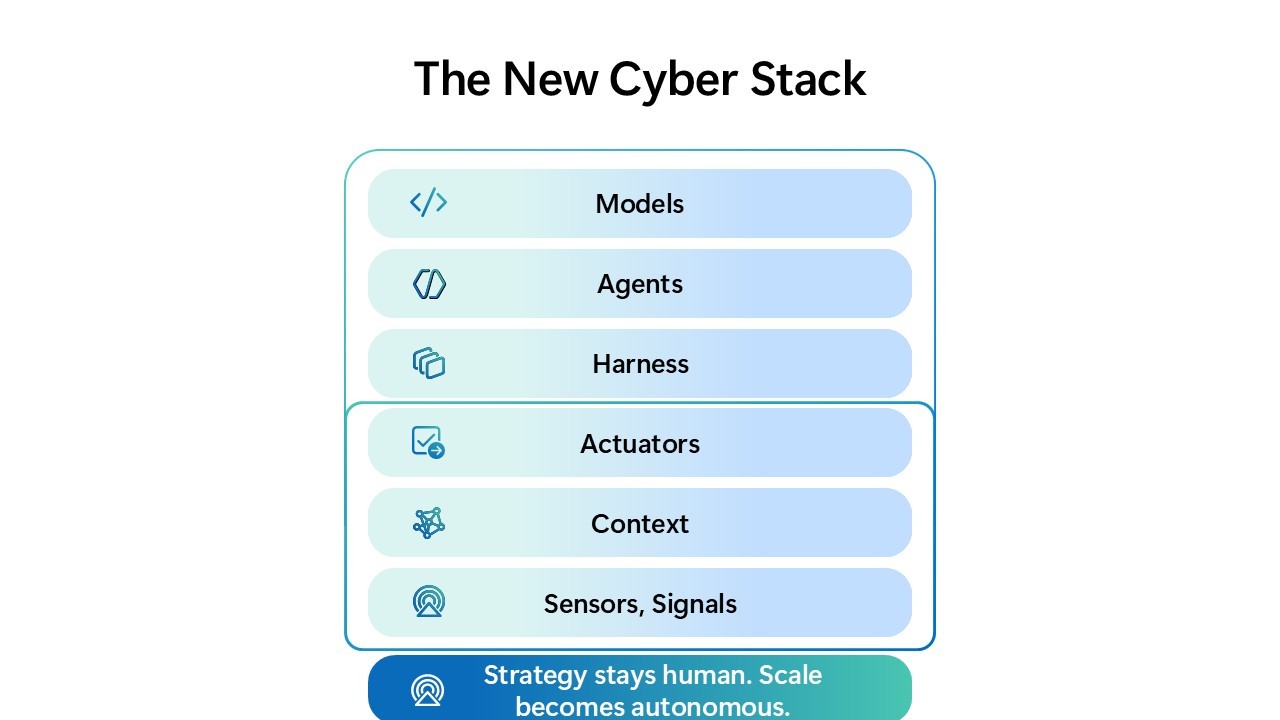
Reimagining the SOC for the agentic era in Microsoft Defender
The physics of cybersecurity are changing. So must the security operations center (SOC).Cyberat...
2026-9-23 16:0:0 | 阅读: 35 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
agents
isoc
signals
agentic
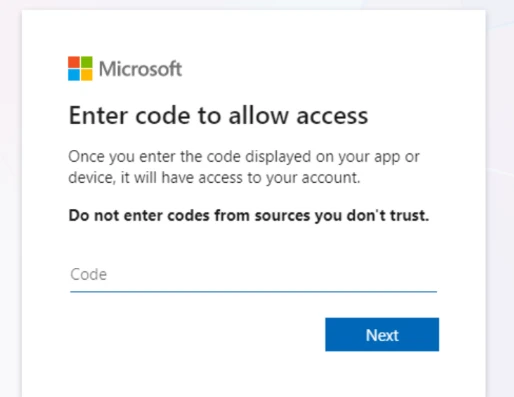
Unmasking EvilTokens: Getting to the root of device code phishing
Following its emergence in February 2026, EvilTokens quickly became one of the most widely used...
2026-9-22 15:0:0 | 阅读: 28 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
phishing
eviltokens
defender
From guidance to action: Security fundamentals that materially reduce risk
AI has already made fundamental changes to the operating environment for cybersecurity. Cyberattack...
2026-9-17 17:0:0 | 阅读: 40 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
microsoft
exposure
agents
weaknesses
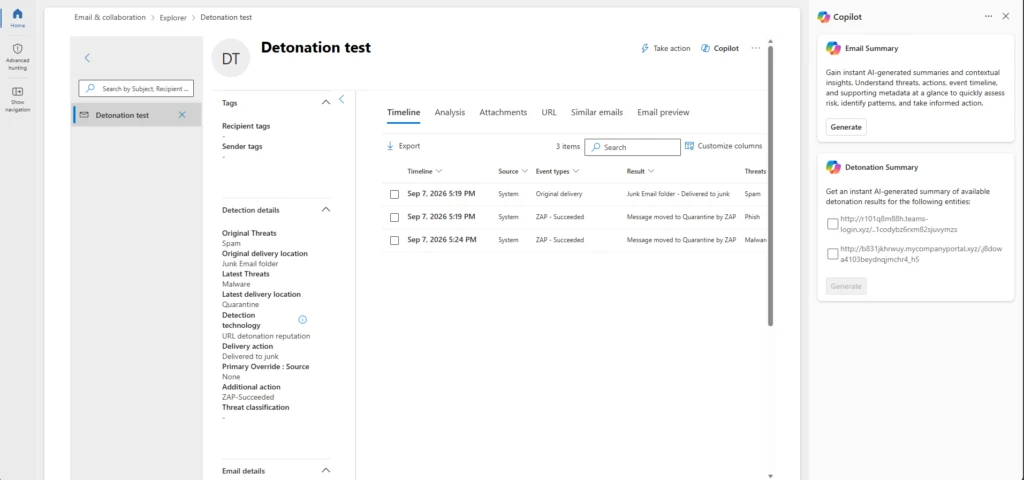
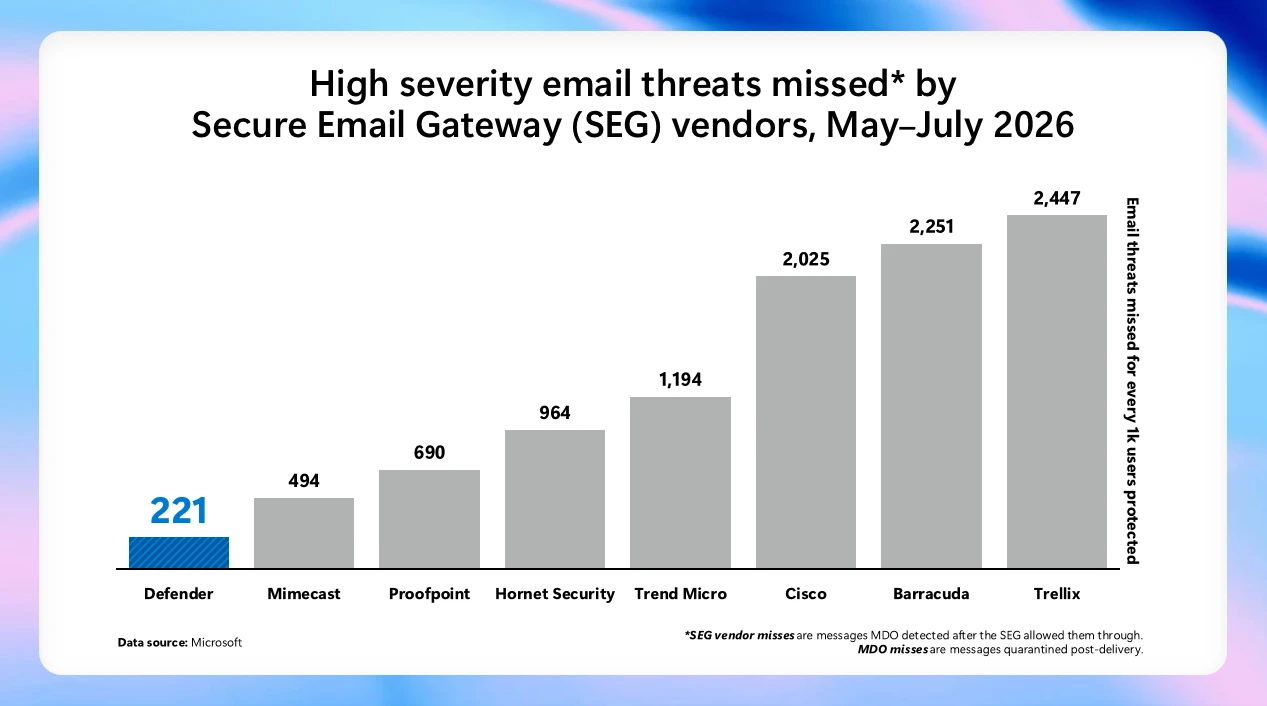
Improving email security outcomes with real-world Microsoft Defender insights
Every benchmark tells a story. The most valuable ones tell us where to improve next. For five c...
2026-9-17 16:0:0 | 阅读: 29 |
收藏
|
Microsoft Security Blog - www.microsoft.com
defender
microsoft
threats
2026
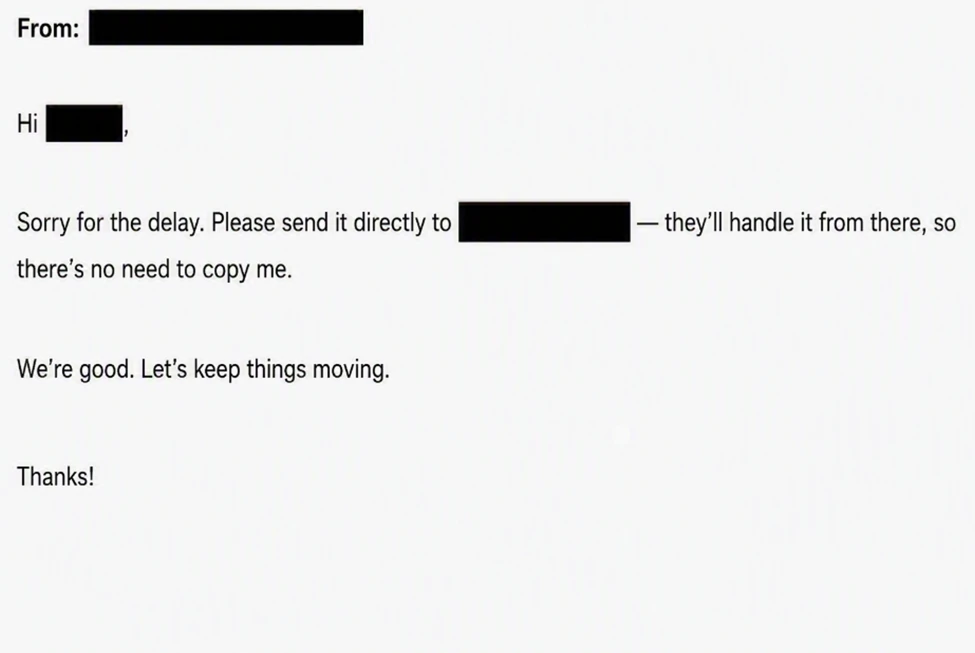
Protecting organizations from AI-assisted executive impersonation and invoice fraud
Threat actors are increasingly improving their tactics to make suspicious emails look like legi...
2026-9-10 17:23:5 | 阅读: 35 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
invoice
defender
servicenow
security
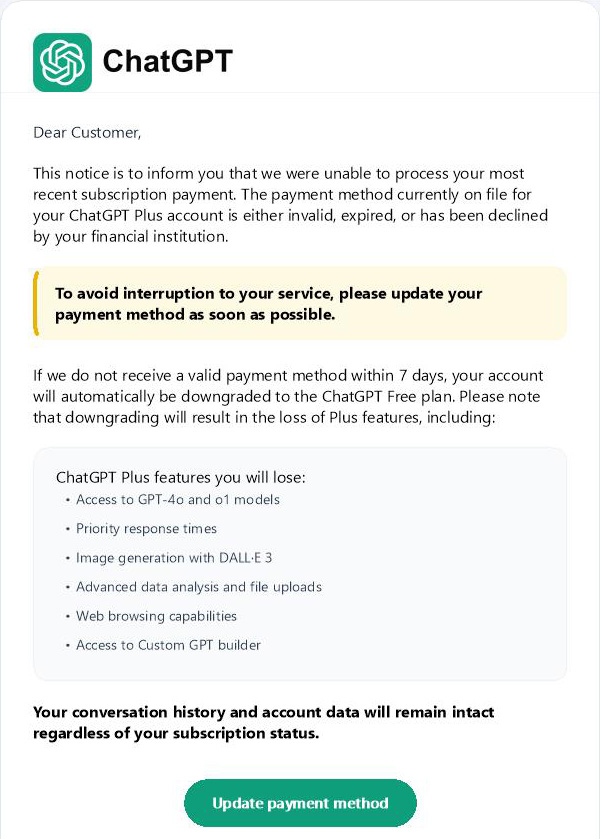
Detect and disrupt AI-themed attacks with Microsoft Defender
Every wave of technology excitement creates a new opportunity for cyberattackers, and AI is no exce...
2026-9-10 16:0:0 | 阅读: 35 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
defender
themed
lure
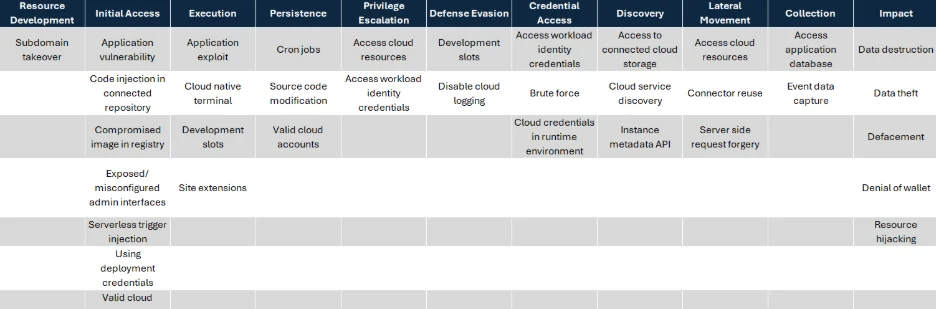
Threat Matrix: Mapping threats across cloud web applications
Microsoft introduces the cloud web applications threat matrix, a MITRE ATT&CK-aligned framework...
2026-9-9 21:30:0 | 阅读: 38 |
收藏
|
Microsoft Security Blog - www.microsoft.com
cloud
tactic
microsoft
malicious
workload
Passkey-themed social engineering leads to identity and cloud compromise
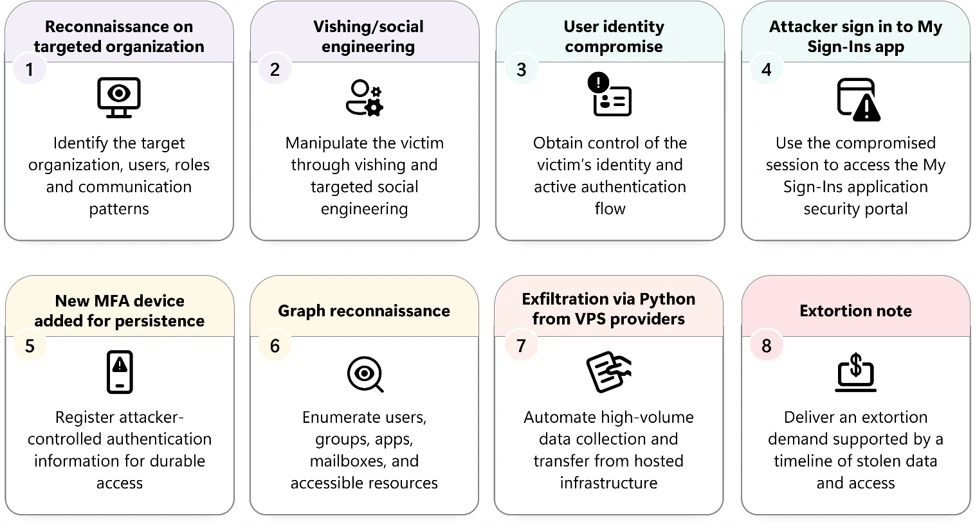
Microsoft Security Research is tracking active cloud-based intrusions spanning multiple account...
2026-9-9 17:41:18 | 阅读: 39 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
cloud
requesturi
How to secure edge AI in customer-owned environments
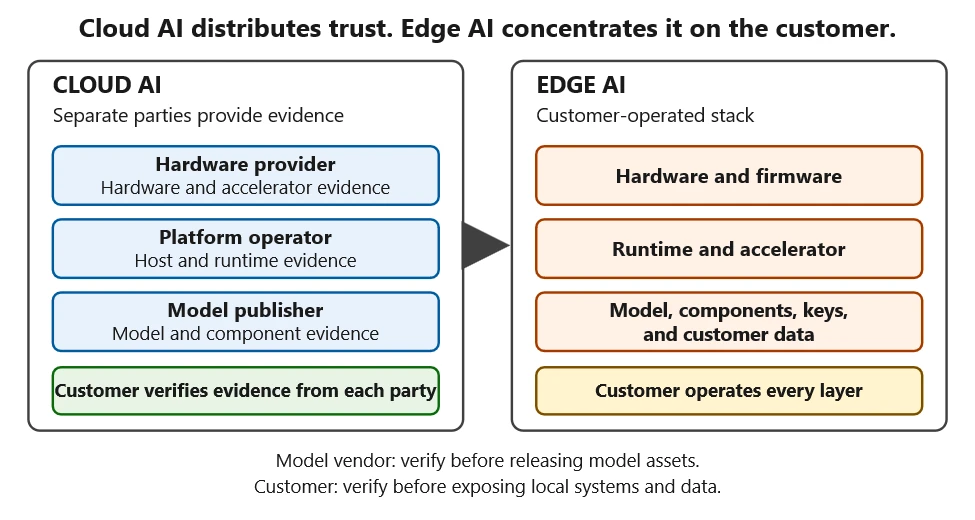
Edge AI moves model execution, model IP, customer data, and system authority into infrastructur...
2026-9-4 19:10:10 | 阅读: 28 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
artifacts
approved
hardware
artifact
ASCII smuggling crosses over from AI prompt injection to phishing evasion
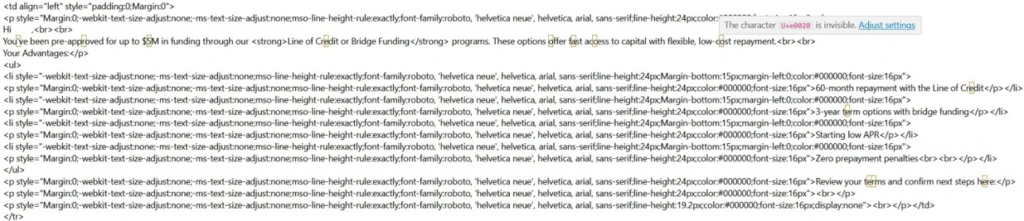
Microsoft researchers observed a high-volume phishing campaign using invisible Unicode tag char...
2026-9-3 16:0:0 | 阅读: 42 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
finance
invisible
phishing
security
Previous
2
3
4
5
6
7
8
9
Next