unSafe.sh - 不安全
我的收藏
今日热榜
公众号文章
导航
Github CVE
Github Tools
编码/解码
文件传输
Twitter Bot
Telegram Bot
Search
Rss
黑夜模式
Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments
Activity associated with Storm-2570, a ransomware affiliate linked to multiple ransomware paylo...
2026-9-24 16:0:0 | 阅读: 4 |
收藏
|
Microsoft Security Blog - www.microsoft.com
2570
ransomware
microsoft
defender
remote
What’s new in Microsoft Security: September 2026
AI agents are now running on employee devices, cloud platforms, and across developer workflows. Sec...
2026-9-24 16:0:0 | 阅读: 0 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
security
copilot
purview
labeling
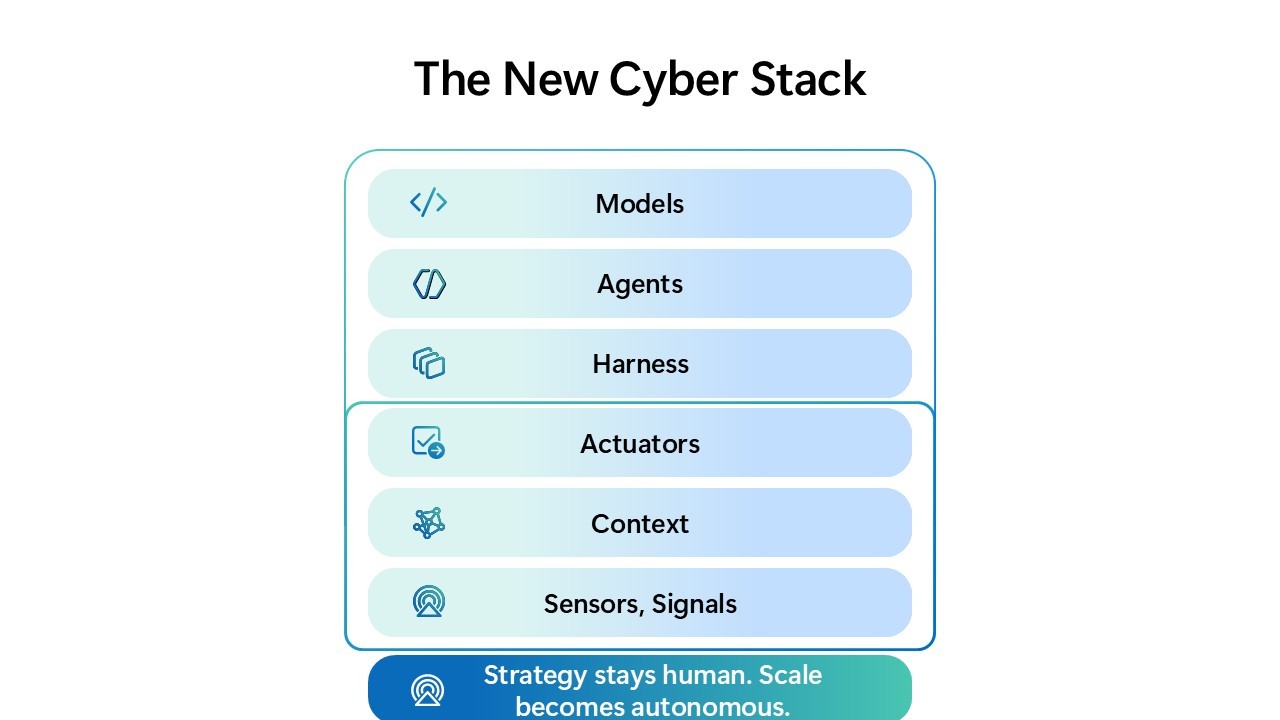
Reimagining the SOC for the agentic era in Microsoft Defender
The physics of cybersecurity are changing. So must the security operations center (SOC).Cyberat...
2026-9-23 16:0:0 | 阅读: 11 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
agents
isoc
signals
agentic
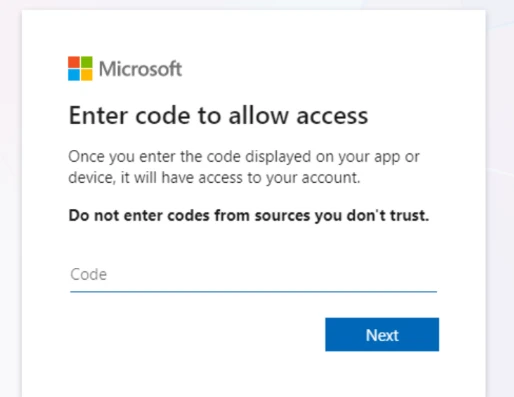
Unmasking EvilTokens: Getting to the root of device code phishing
Following its emergence in February 2026, EvilTokens quickly became one of the most widely used...
2026-9-22 15:0:0 | 阅读: 17 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
phishing
eviltokens
defender
From guidance to action: Security fundamentals that materially reduce risk
AI has already made fundamental changes to the operating environment for cybersecurity. Cyberattack...
2026-9-17 17:0:0 | 阅读: 20 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
microsoft
exposure
agents
weaknesses
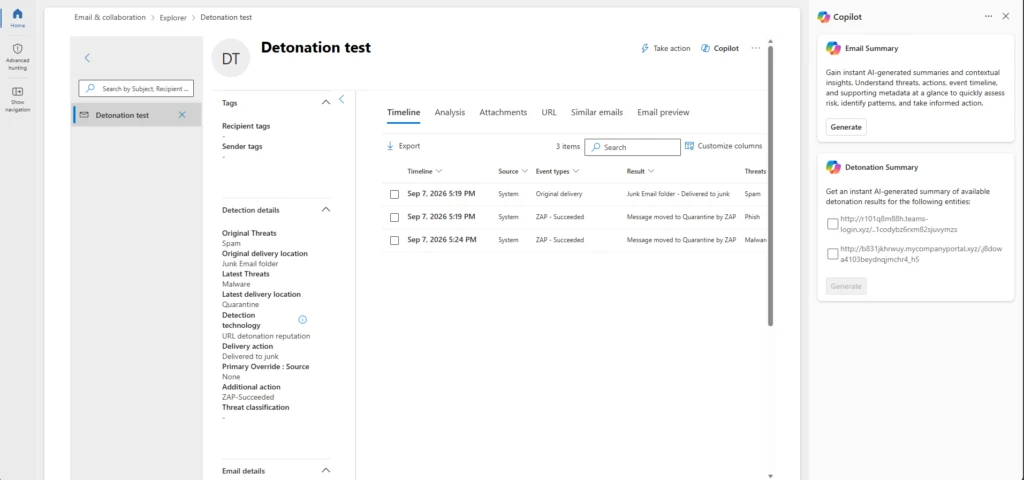
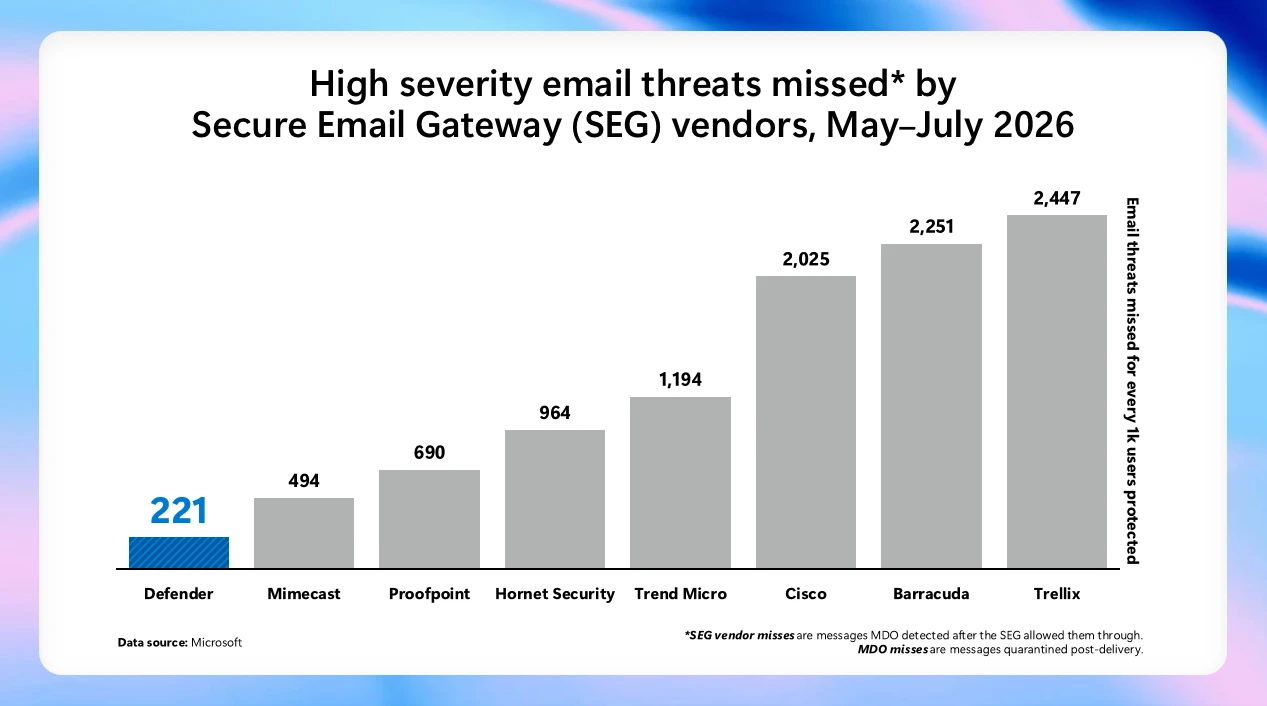
Improving email security outcomes with real-world Microsoft Defender insights
Every benchmark tells a story. The most valuable ones tell us where to improve next. For five c...
2026-9-17 16:0:0 | 阅读: 16 |
收藏
|
Microsoft Security Blog - www.microsoft.com
defender
microsoft
threats
2026
Protecting organizations from AI-assisted executive impersonation and invoice fraud
Threat actors are increasingly improving their tactics to make suspicious emails look like legi...
2026-9-10 17:23:5 | 阅读: 24 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
invoice
defender
servicenow
security
Detect and disrupt AI-themed attacks with Microsoft Defender
Every wave of technology excitement creates a new opportunity for cyberattackers, and AI is no exce...
2026-9-10 16:0:0 | 阅读: 22 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
defender
themed
lure
Threat Matrix: Mapping threats across cloud web applications
Microsoft introduces the cloud web applications threat matrix, a MITRE ATT&CK-aligned framework...
2026-9-9 21:30:0 | 阅读: 22 |
收藏
|
Microsoft Security Blog - www.microsoft.com
cloud
tactic
microsoft
malicious
workload
Passkey-themed social engineering leads to identity and cloud compromise
Microsoft Security Research is tracking active cloud-based intrusions spanning multiple account...
2026-9-9 17:41:18 | 阅读: 24 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
cloud
requesturi
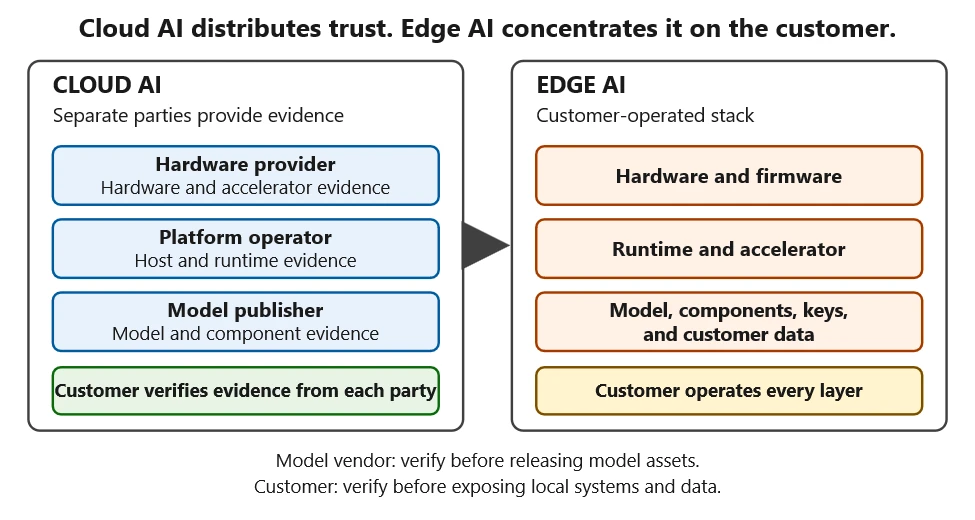
How to secure edge AI in customer-owned environments
Edge AI moves model execution, model IP, customer data, and system authority into infrastructur...
2026-9-4 19:10:10 | 阅读: 20 |
收藏
|
Microsoft Security Blog - www.microsoft.com
security
artifacts
approved
hardware
artifact
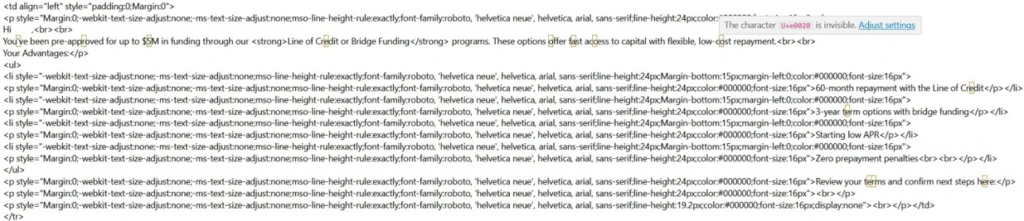
ASCII smuggling crosses over from AI prompt injection to phishing evasion
Microsoft researchers observed a high-volume phishing campaign using invisible Unicode tag char...
2026-9-3 16:0:0 | 阅读: 23 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
finance
invisible
phishing
security
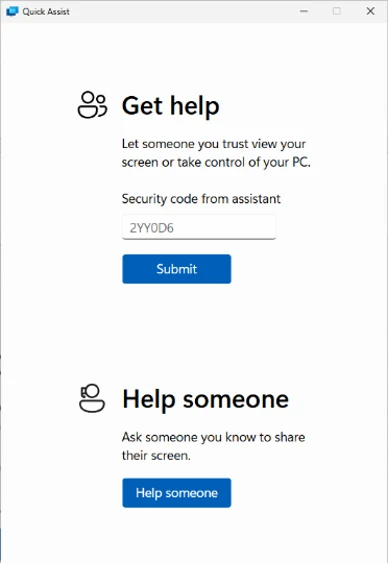
Impersonating IT support: how threat actors turn a remote session into enterprise-wide access
Microsoft Threat Intelligence has observed a human-operated intrusion campaign that abuses Micr...
2026-9-2 22:51:18 | 阅读: 26 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
remote
loader
malicious
defender
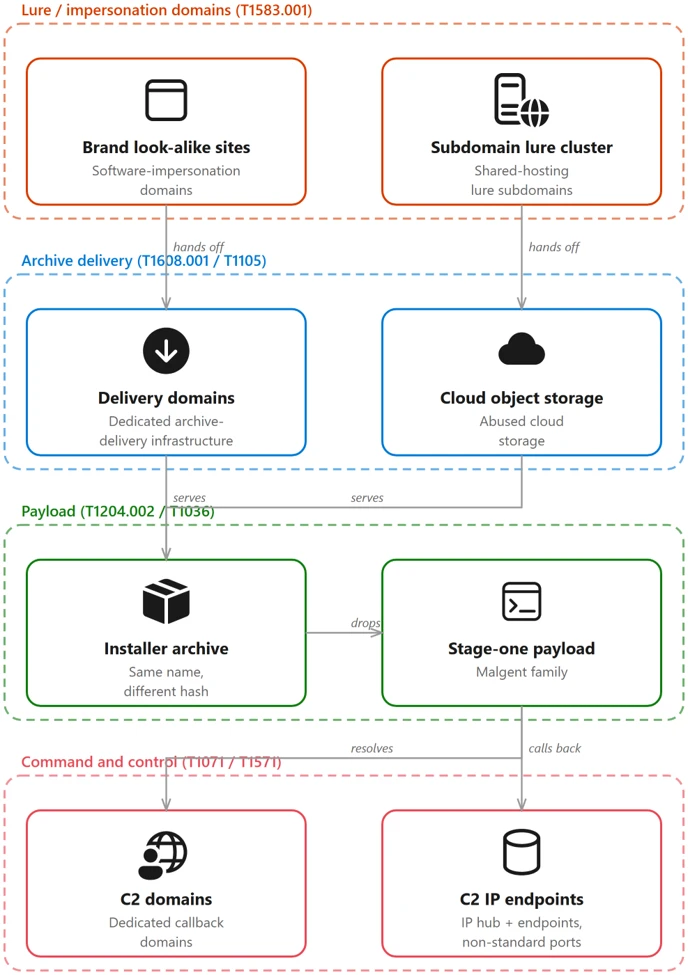
Counterfeit installers to system compromise: Tracking a deceptive software download campaign
Microsoft Defender Experts is tracking an active malware campaign that uses counterfeit softwar...
2026-9-1 22:48:28 | 阅读: 37 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
defender
payload
windows
stage
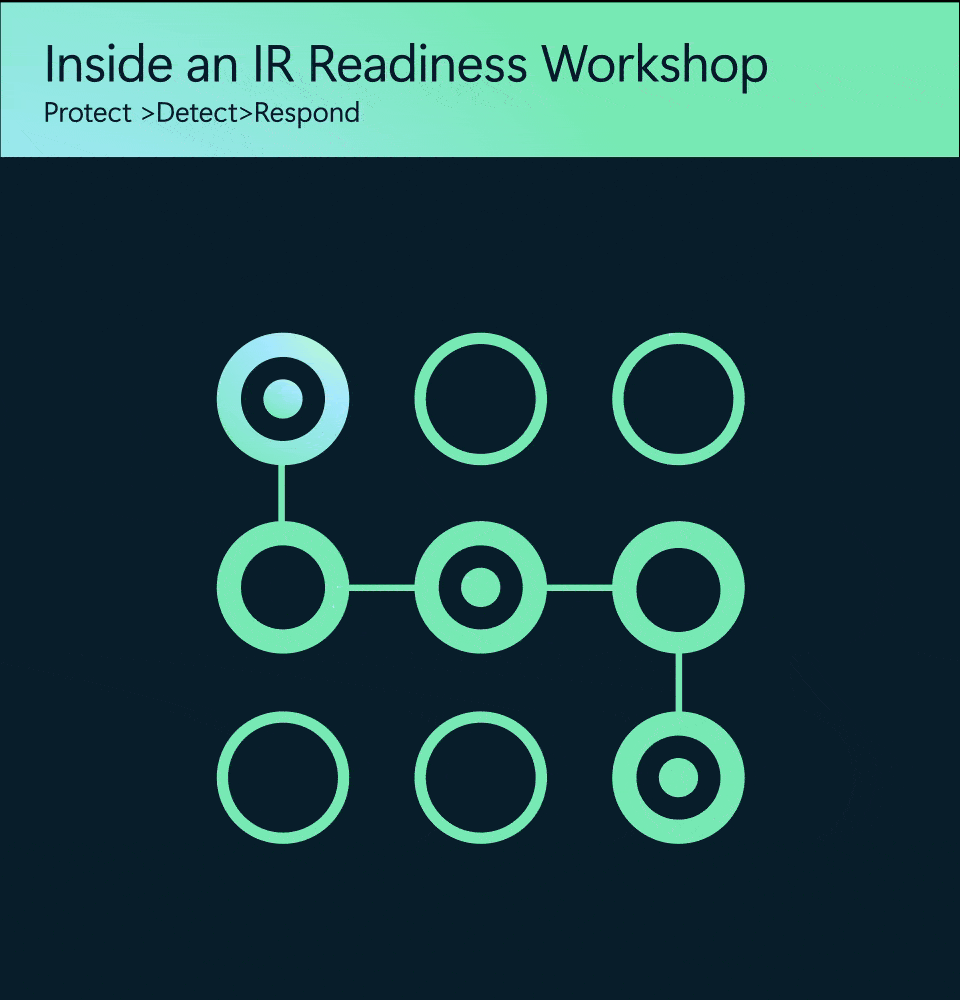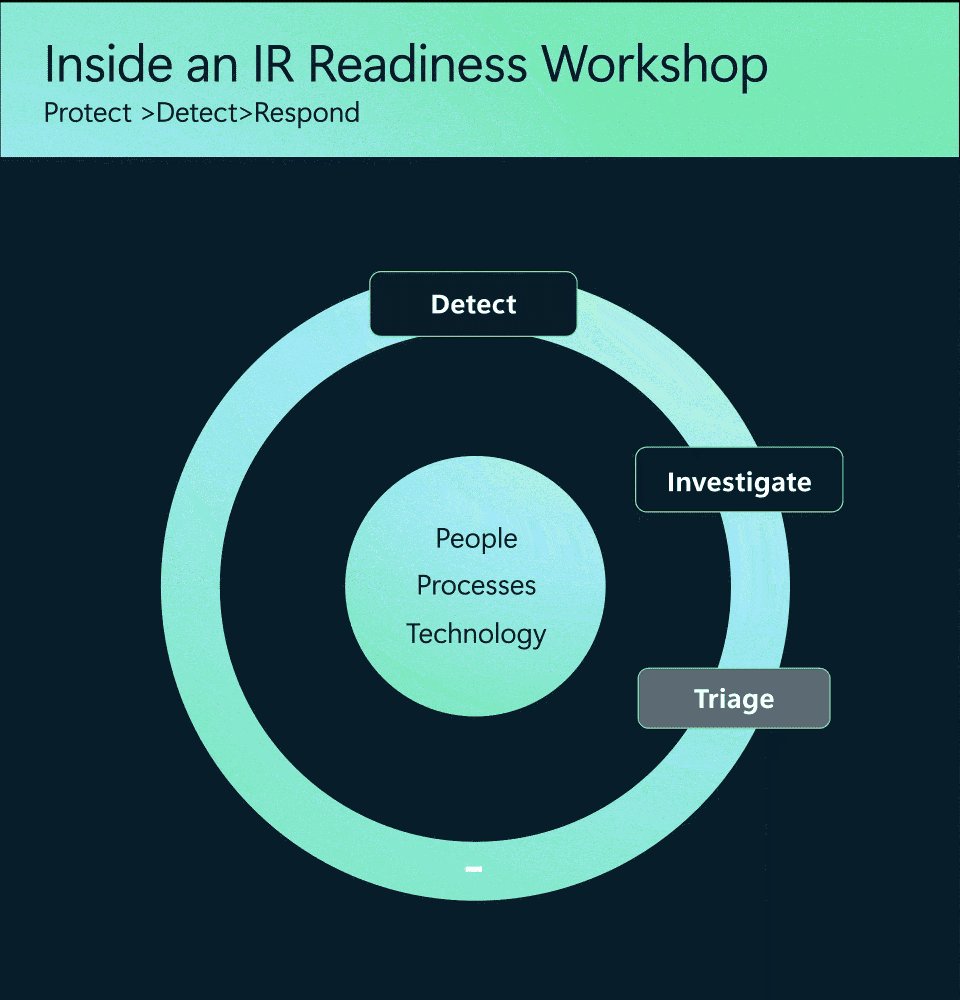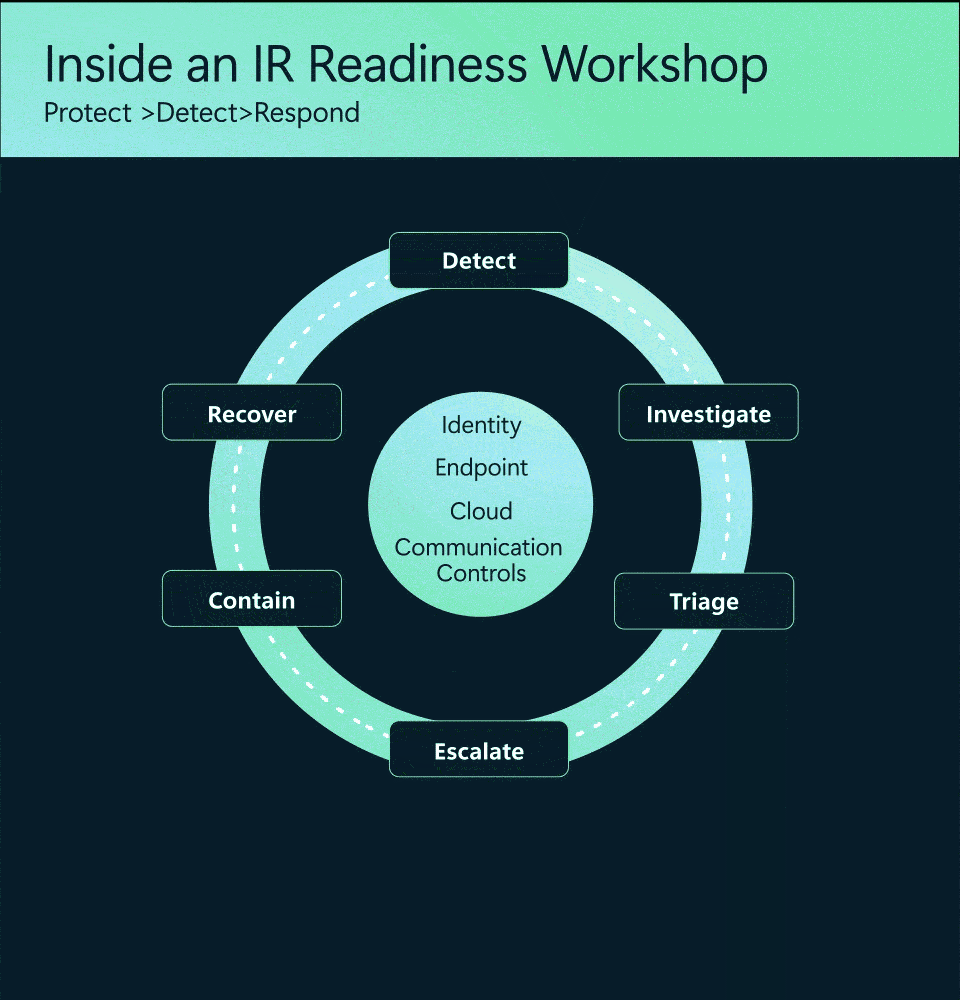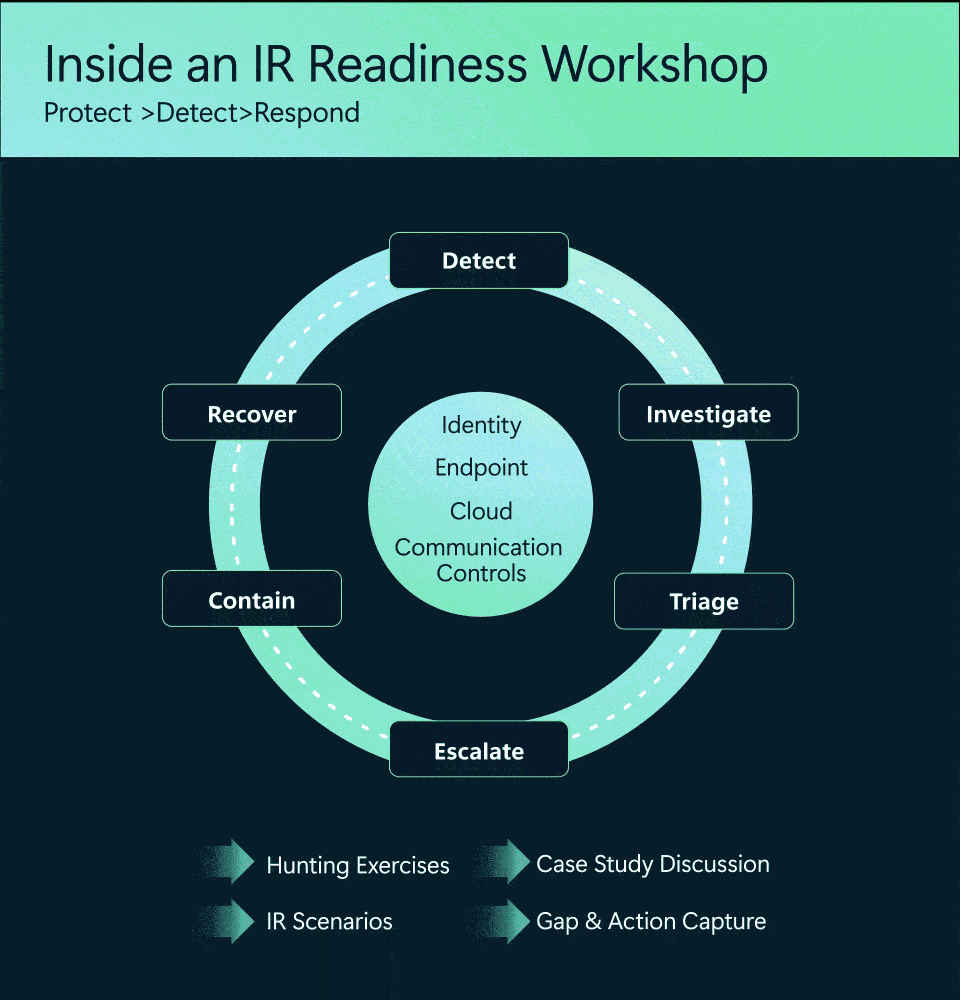
Cybersecurity IR Workshop: The workshop you shouldn’t miss
Cybersecurity incidents can unfold in hours, but response plans often fail at the point of exec...
2026-9-1 18:55:35 | 阅读: 19 |
收藏
|
Microsoft Security Blog - www.microsoft.com
workshop
dart
microsoft
processes
TerminalFix campaign deploys a reverse tunnel through multistage intrusion
Microsoft Threat Intelligence has observed a TerminalFix campaign, a variant of ClickFix, targe...
2026-8-29 03:43:27 | 阅读: 40 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
powershell
defender
dui70
malicious
What’s new in Microsoft Security: August 2026
As organizations incorporate AI agents into more processes across business and operations, security...
2026-8-27 16:0:0 | 阅读: 20 |
收藏
|
Microsoft Security Blog - www.microsoft.com
microsoft
security
defender
labeling
drift
When AI infrastructure becomes the target: Securing gateways and control points
AI is creating a new layer of enterprise infrastructure. Gateways, retrieval platforms, orchest...
2026-8-26 16:43:53 | 阅读: 24 |
收藏
|
Microsoft Security Blog - www.microsoft.com
litellm
database
microsoft
ragflow
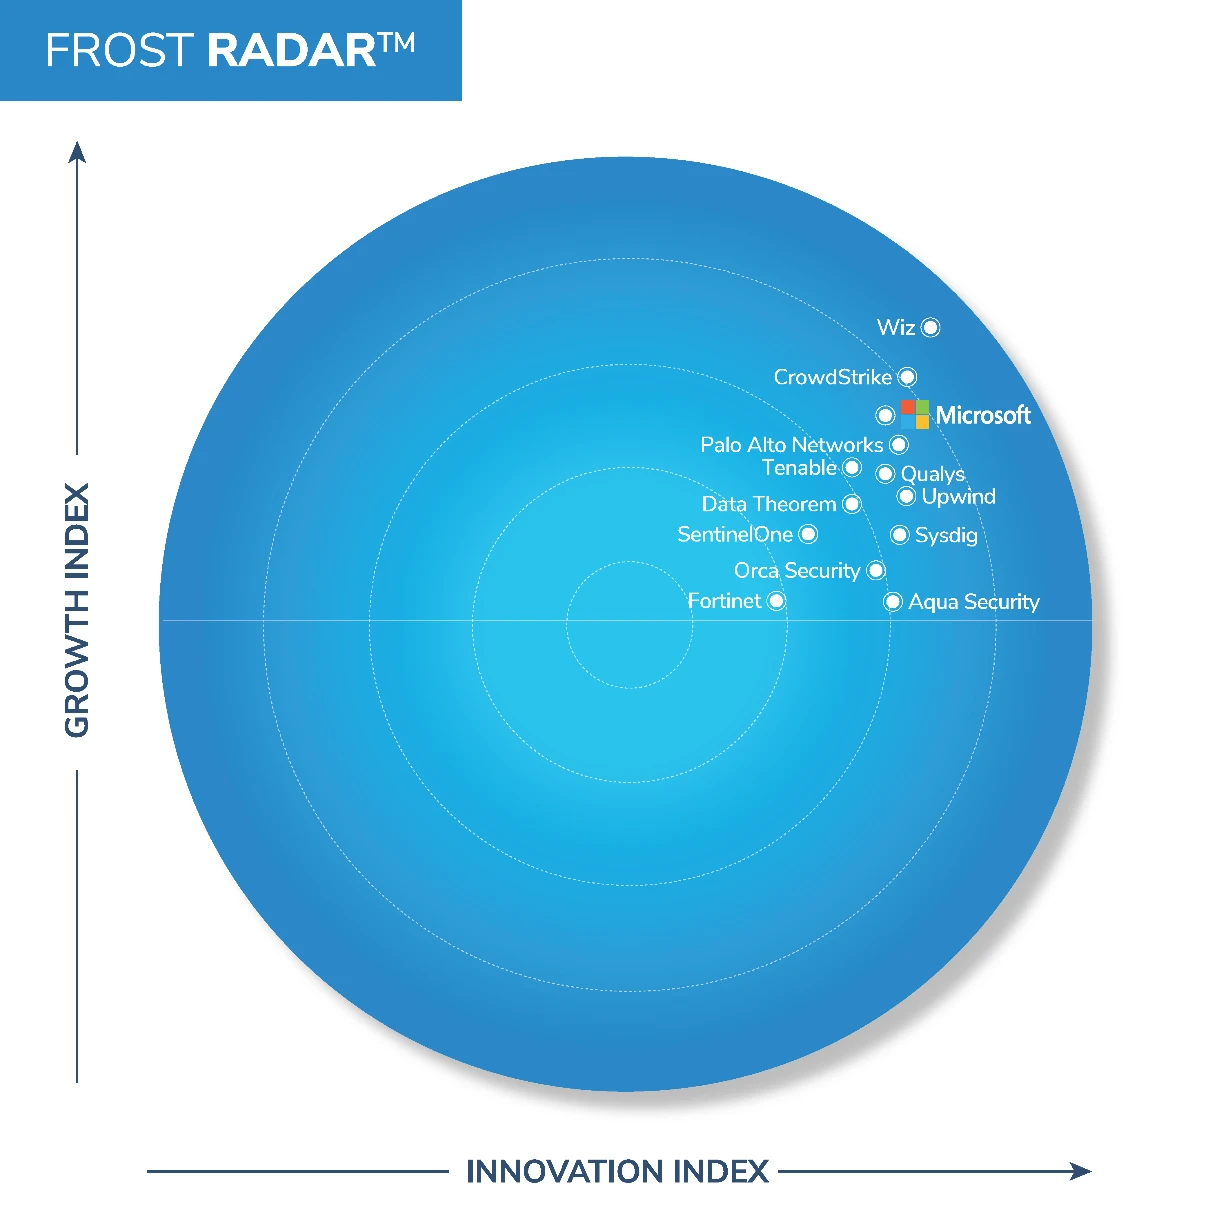
Microsoft named a Leader in the Frost Radar™: Cloud Workload Protection Platforms, 2026
Security teams are overwhelmed with findings but still struggle to answer a simple question: which...
2026-8-19 17:30:0 | 阅读: 36 |
收藏
|
Microsoft Security Blog - www.microsoft.com
cloud
security
microsoft
workload
frost
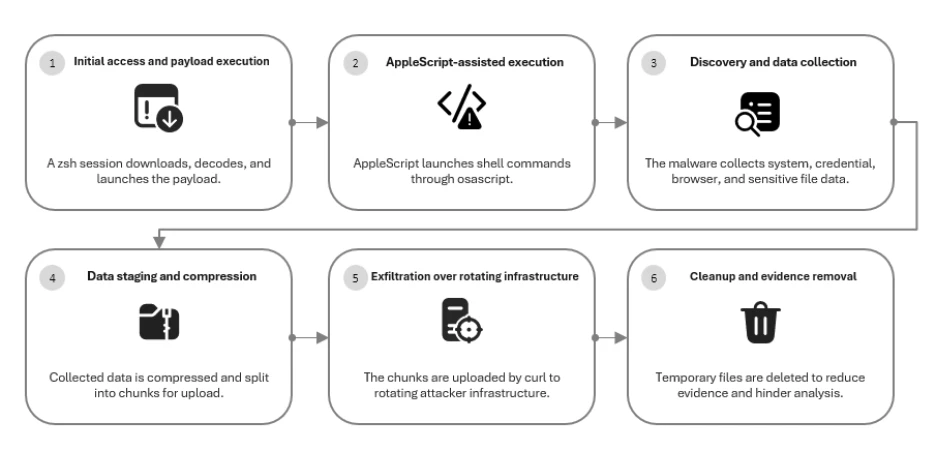
Hunting MacSync Stealer infrastructure through behavioral pivots
MacSync Stealer is a macOS-focused information stealer that relies on changing infrastructure t...
2026-8-18 17:8:28 | 阅读: 37 |
收藏
|
Microsoft Security Blog - www.microsoft.com
stealer
macsync
behavioral
microsoft
payload
Previous
-3
-2
-1
0
1
2
3
4
Next