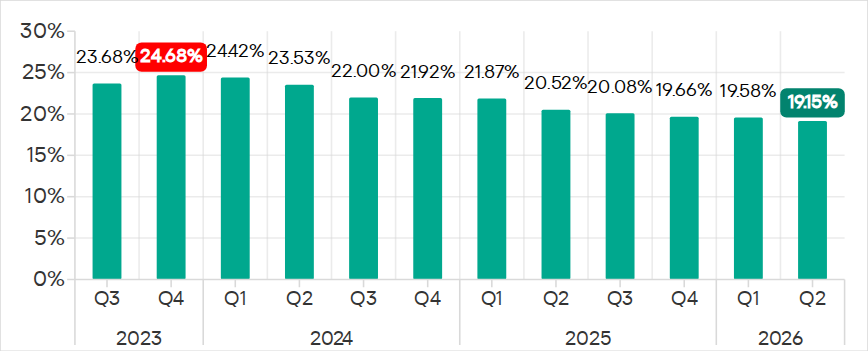unSafe.sh - 不安全
我的收藏
今日热榜
公众号文章
导航
Github CVE
Github Tools
编码/解码
文件传输
Twitter Bot
Telegram Bot
Search
Rss
黑夜模式
MacSync under the microscope: new delivery methods and a new payload
MacSync is a relatively young, rapidly evolving family of crypto/info stealers. First...
2026-9-24 10:0:21 | 阅读: 13 |
收藏
|
Securelist - securelist.com
stage
macsync
payload
hxxps
malicious
Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO
Executive summaryIn April 2026, we at Kaspersky’s Global Emergency Response Team (GER...
2026-9-21 10:0:40 | 阅读: 25 |
收藏
|
Securelist - securelist.com
gpo
payload
windows
ransomware
sysvol
The Odyssey and trojans again: MovieReaper attacks users in multiple countries via compromised torrents
IntroductionTorrent trackers have long been abused for distributing malicious softwar...
2026-9-17 13:0:53 | 阅读: 32 |
收藏
|
Securelist - securelist.com
stage
torrent
c2
loader
shellcode
NightEagle targets Russian companies
Over the past year, our Global Emergency Response Team (GERT) has investigated several...
2026-9-16 10:0:11 | 阅读: 24 |
收藏
|
Securelist - securelist.com
attackers
network
microsoft
tunneling
Angry Birds: Toy Ghouls’ new toys
SOC, TI and IR posts...
2026-9-4 10:15:39 | 阅读: 24 |
收藏
|
Over Security - Cybersecurity news aggregator - securelist.com
hivemq
broker
attackers
bird
windows
Mirage Kitten targeting aviation and FinTech sectors across the Middle East and Africa with a new malware set
While monitoring Mirage Kitten activity, we uncovered a previously undocumented malwar...
2026-9-1 07:16:3 | 阅读: 29 |
收藏
|
Over Security - Cybersecurity news aggregator - securelist.com
c2
pollcat
noderabbit
windows
ValleyRAT masquerading as adware
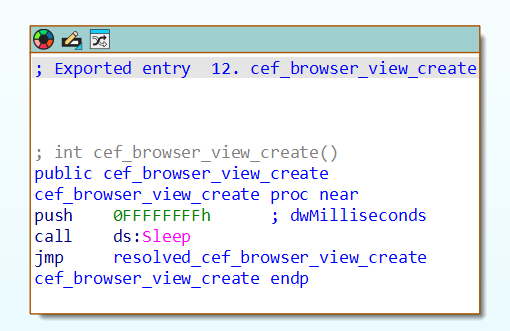
Attackers typically try to pass off malware as legitimate applications or as potential...
2026-8-31 10:15:43 | 阅读: 28 |
收藏
|
Over Security - Cybersecurity news aggregator - securelist.com
library
malicious
libcef
qnwallpaper
valleyrat
Threat landscape for industrial automation systems. Q2 2026
All threatsIn Q2 2026, the percentage of ICS computers on which malicious objects wer...
2026-8-27 10:5:43 | 阅读: 18 |
收藏
|
Securelist - securelist.com
industries
regions
malicious
q2
threats
Exploits and vulnerabilities in Q2 2026
The vulnerability landscape shifted significantly in Q2 2026. First, the number of reg...
2026-8-26 10:0:4 | 阅读: 53 |
收藏
|
Securelist - securelist.com
2026
q2
windows
privileges
The invisible passenger in your car
Malware descriptions...
2026-8-21 08:0:29 | 阅读: 53 |
收藏
|
Securelist - securelist.com
stage
payload
hxxp
sbs
jarservice
APT group HoneyMyte upgrades CoolClient: the backdoor gets a kernel-level Windows rootkit
IntroductionCoolClient is a backdoor family attributed to the HoneyMyte APT group (al...
2026-8-14 09:0:14 | 阅读: 57 |
收藏
|
Securelist - securelist.com
coolclient
stage
windows
defender
processes
Armored Likho expands its cyber-espionage toolkit
In May 2026, we discovered a new cyber-espionage campaign by the Armored Likho group,...
2026-8-13 08:0:15 | 阅读: 52 |
收藏
|
Securelist - securelist.com
attackers
c2
recording
2026
threshold
Head Mare APT is exploiting vulnerabilities in an unpatched TrueConf server to deliver PhantomCore and PhantomGraph to video conference participants
Overview of the attackIn July 2026, Kaspersky experts detected a new attack by the He...
2026-8-11 12:0:55 | 阅读: 43 |
收藏
|
Securelist - securelist.com
trueconf
phantomcore
attackers
headmare
windows
Project CAV3RN continues: Google Apps Script as C2 relay and DNS-based C2 channel selection
Project CAV3RN is a modular espionage framework used against targets in Israel. This r...
2026-8-11 10:0:19 | 阅读: 48 |
收藏
|
Securelist - securelist.com
broker
studiotikva
c2
client
rnp
IT threat evolution in Q2 2026. Non-mobile statistics
IT threat evolution in Q2 2026. Non-mobile statisticsIT threat evolution in Q2 2026....
2026-8-10 10:0:37 | 阅读: 55 |
收藏
|
Securelist - securelist.com
ransomware
2026
q2
territory
malicious
IT threat evolution in Q2 2026. Mobile statistics
IT threat evolution in Q2 2026. Mobile statisticsIT threat evolution in Q2 2026. Non-...
2026-8-10 10:0:9 | 阅读: 50 |
收藏
|
Securelist - securelist.com
trojan
banker
q2
2026
mamont
How legitimate cloud platforms enable phishers to bypass MFA
Threat actors are increasingly exploiting legitimate cloud services to evade detection...
2026-8-4 12:0:12 | 阅读: 41 |
收藏
|
Securelist - securelist.com
phishing
cloud
stage
security
captcha
An analysis of incidents at Brazilian educational institutions
IntroductionBecause of the amount of data that can be obtained and the high impact th...
2026-8-3 13:0:17 | 阅读: 46 |
收藏
|
Securelist - securelist.com
software
windows
microsoft
attackers
Network Anomaly Detection in KATA
IntroductionOnce the attacker has breached the corporate network, subsequent stages o...
2026-7-31 10:0:25 | 阅读: 47 |
收藏
|
Securelist - securelist.com
network
tunneling
client
nad
signs
OctLurk and SilkLurk: newly identified tailored backdoors in cyber-espionage campaign in Central Asia
IntroductionWe have been tracking two new backdoors, OctLurk and SilkLurk, observed i...
2026-7-30 11:0:12 | 阅读: 59 |
收藏
|
Securelist - securelist.com
c2
octlurk
network
loader
microsoft
Previous
-5
-4
-3
-2
-1
0
1
2
Next