unSafe.sh - 不安全
我的收藏
今日热榜
公众号文章
导航
Github CVE
Github Tools
编码/解码
文件传输
Twitter Bot
Telegram Bot
Search
Rss
黑夜模式
Crypto Hardware Wallet Users Under Attack
Introduction A new attack campaign targeting users of cryptocurrency and specifically those using h...
2026-11-17 00:31:59 | 阅读: 14 |
收藏
|
Over Security - Cybersecurity news aggregator - bartblaze.blogspot.com
remote
ledger
coldcard
Autumn Dragon: China-nexus APT Group Targets South East Asia
In this report, we describe how we tracked for several months a sustained espionage campaign agains...
2025-11-19 23:3:31 | 阅读: 60 |
收藏
|
Over Security - Cybersecurity news aggregator - bartblaze.blogspot.com
philippines
nexus
espionage
victimology
indonesia
Earth Estries alive and kicking
Earth Estries(Salt Typhoon)是一个与中国相关的APT组织,近期利用WinRAR漏洞发起攻击,通过恶意文件和加密组件传播 implants 如Snappybee和ShadowPad,并使用C2服务器控制受感染设备。...
2025-10-27 22:15:17 | 阅读: 23 |
收藏
|
Over Security - Cybersecurity news aggregator - bartblaze.blogspot.com
winrar
commonsdk
hijacked
earth
estries
Steam Phishing: popular as ever
文章描述了一起针对 Steam 用户的钓鱼攻击事件。攻击者通过好友发送看似正常的优惠券链接,实则指向伪造的 Steam 社区页面以窃取账户信息。类似的钓鱼网站还包括多个伪装域名。提醒用户仅在官方 Steam 社区登录、警惕陌生好友及异常链接,并使用 URLscan.io 或 VirusTotal 检查可疑链接的安全性,同时保持谨慎以防受骗。...
2025-6-20 17:20:0 | 阅读: 28 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
phishing
friend
bookmark
bells
alarm
Microsoft Word and Sandboxes
Today's post is a brief one on some Microsoft Word and sandbox detection / discovery / fun.Collect...
2024-8-15 01:45:17 | 阅读: 30 |
收藏
|
Over Security - Cybersecurity news aggregator - bartblaze.blogspot.com
microsoft
username
asd
sandboxes
userinfo
New North Korean based backdoor packs a punch
2024-6-21 05:10:0 | 阅读: 24 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
Analyse, hunt and classify malware using .NET metadata
IntroductionEarlier this week, I ran into a sample that turned out to be PureCrypter, a loader and...
2024-3-26 03:13:0 | 阅读: 34 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
mvid
typelib
f0
python
quasar
Fara: Faux YARA
FARA, or Faux YARA, is a simple repository that contains a set of purposefully erroneous Yara rules...
2023-12-5 03:15:17 | 阅读: 21 |
收藏
|
Over Security - Cybersecurity news aggregator - bartblaze.blogspot.com
fara
faux
github
bartblaze
veterans
Yara rules collection
Quite a while ago, I've published some of my private Yara rules online, on Github. They can be foun...
2022-12-10 23:20:0 | 阅读: 17 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
github
workflows
natively
convenience
artifacts
Digital artists targeted in RedLine infostealer campaign
2021-06-17: updated with information from Twitter user ARC In this post, we'll look at a campaign,...
2021-6-15 03:30:0 | 阅读: 22 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
attacker
redline
tweet
windows
machine
Blue Team Puzzle
Several years ago, I created a "malware puzzle" - basically, a crossword puzzle but with terms rela...
2020-11-24 04:33:0 | 阅读: 21 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
puzzle
crossword
bartblaze
mediafire
mirror
Satan ransomware rebrands as 5ss5c ransomware
The cybercrime group that brought us Satan, DBGer and Lucky ransomware and perhaps Iron ransomware...
2020-1-15 06:48:0 | 阅读: 27 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
ransomware
5ss5c
satan
spreader
cpt
Monero download site and binaries compromised
Earlier this evening I saw a tweet appear which claimed Monero has been hacked and a malicious bi...
2019-11-20 06:18:0 | 阅读: 24 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
monero
windows
filehash
getmonero
c2
Run applications and scripts using Acer's RunCmd
This weekend I was cleaning up an old Acer laptop of mine and discovered a hidden folder on the ro...
2019-3-18 05:17:0 | 阅读: 30 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
runcmd
02d
193c
acer
attackers
Analysing a massive Office 365 phishing campaign
Last week, a friend of mine reached out with a query: a contact in his address book had sent him a...
2019-3-5 03:57:0 | 阅读: 20 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
phishing
attacker
o365
microsoft
MAFIA ransomware targeting users in Korea
A new ransomware family was discovered and sent to me by MalwareHunterTeam, which we'll call MAFIA...
2018-8-12 23:31:0 | 阅读: 20 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
mafia
ransomware
korean
appcheck
c2
RedEye ransomware: there's more than meets the eye
A rather anonymous account reached out to me on Twitter asking to check out a "scary & really nas...
2018-6-7 06:30:0 | 阅读: 34 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
ransomware
redeye
mbr
annabelle
icorex
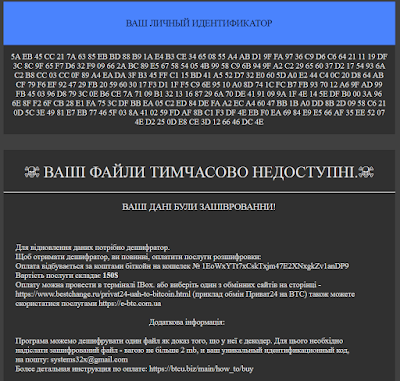
PSCrypt ransomware: back in business
PSCrypt is ransomware first discovered last year, in 2017, targeting users and organisations alike...
2018-5-7 19:45:0 | 阅读: 21 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
windows
ransomware
pscrypt
btc
не
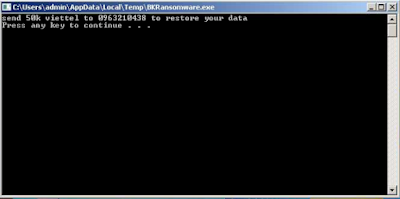
Vietnamese ransomware wants you to add credit to a mobile phone
In this quick blog post we'll have a look at BKRansomware, a Vietnamese ransomware that wants you...
2018-5-6 01:20:0 | 阅读: 20 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
ransomware
vietnamese
viettel
hainhc
Ransomnix ransomware variant encrypts websites
Ransomnix is a (supposedly Jigsaw, but not really) ransomware variant that holds websites for ran...
2018-4-28 22:27:0 | 阅读: 24 |
收藏
|
Blaze's Security Blog - bartblaze.blogspot.com
ransomware
btc
tips
ransomnix
Previous
-75
-74
-73
-72
-71
-70
-69
-68
Next